The CW Corner – Webmail vs. Email Client: Which Should You Use for Your Business Email?

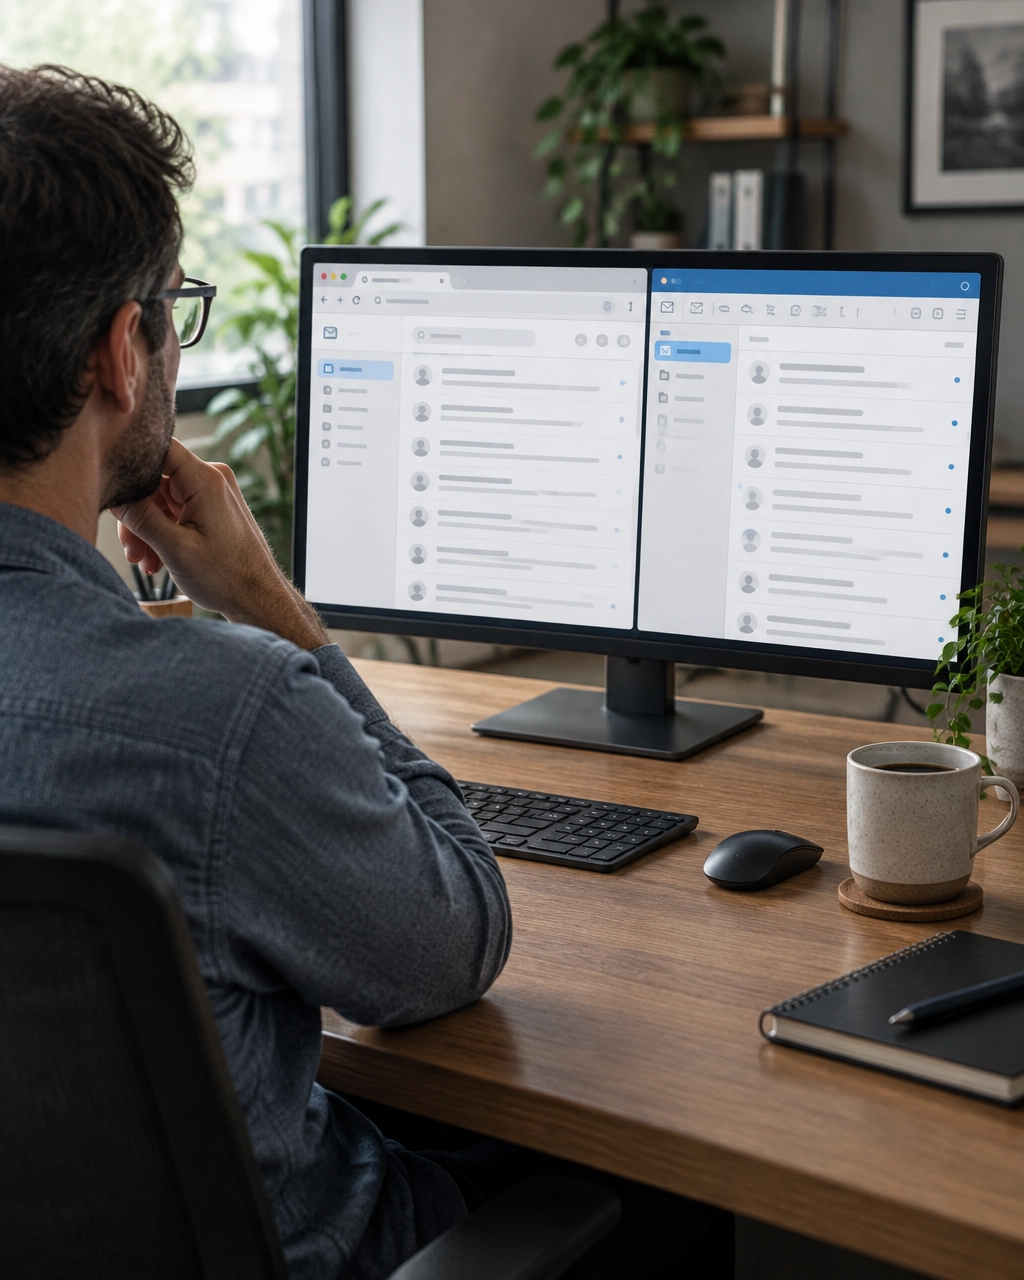
Business owner comparing a webmail inbox in a browser with a desktop email appWebmail vs email client is a choice you face when reading business email on your own domain. Webmail opens in a browser, while an email client is an app such as Outlook, Apple Mail, or Thunderbird. Both can access the same mailbox. The best option depends on where you work and how you want to manage messages.

What is webmail?

Webmail lets you sign in to your email account through a browser. Your hosting provider may give you a webmail link or a portal, such as Roundcube.

You generally don’t need to install or configure anything. Open the link, enter your email address and password, and read or send messages. That makes webmail a practical starting point, especially on a borrowed computer or a new device.

Your mailbox stays on the email provider’s server. The browser is simply the window you use to access it. You can usually sign in from different devices with an internet connection.

The trade-off is that browser-based webmail may not notify you reliably when new messages arrive. You might need to keep a tab open, allow browser notifications, or remember to check manually. If you close the browser and move on, the inbox may not call your attention.

What is an email client?

An email client is a program or app installed on your computer or phone. Outlook, Apple Mail, and Thunderbird are familiar examples.

Once the account is set up, the app connects to your provider’s mail server. It can collect new messages, send replies, and display notifications. Many clients also keep a local copy of messages, so you can read previously downloaded email when offline.

The setup takes more effort. You may need to enter your incoming and outgoing server names, username, password, and security settings. Your host supplies these details. A typo or mismatched setting can prevent sending or receiving.

For background on how mail apps connect, see Microsoft’s explanation of IMAP and POP and Apple’s Mail settings guidance.

Webmail or an app: which is easier?

If you want to start reading email without setting up software, try webmail. It’s usually the simplest way to confirm that your address and password work.

An app may suit you better if you spend much of your day in one program, want notifications, or need to read older messages without an internet connection. Keep in mind that offline access only includes messages already saved on your device. You’ll need an internet connection to receive new mail or send queued messages.

There’s no need to treat this as a permanent decision. You can use webmail and an email app at the same time. Switching between them is safe and reversible. Just choose the right connection type if you want messages and folders to stay consistent across devices.

Choose IMAP for multiple devices

When setting up an email client, you may be asked to choose between IMAP and POP3.

IMAP (Internet Message Access Protocol) keeps messages on the mail server and synchronizes your mailbox across devices. If you read a message on your phone, it can show as read on your computer, too. Folders and other changes can stay in sync.

If you check business email on a phone and a computer, IMAP is usually the sensible choice. It helps avoid the “I thought I replied to that” moment caused by different devices showing different inboxes.

POP3 (Post Office Protocol version 3) typically downloads messages to one device. Depending on its settings, the app may remove downloaded messages from the server. That can make those messages unavailable through webmail or another device.

POP3 can work for a deliberate, single-device setup. But it generally isn’t the best fit when you want the same inbox on several devices. For more details, read Thunderbird’s guide to IMAP and POP.

Setting up an email app

Your hosting provider gives you the account details needed for setup. These may include incoming and outgoing server names, your username, and required security settings.

The incoming server handles messages you receive. The outgoing server uses SMTP (Simple Mail Transfer Protocol) to send your messages. Enter the information exactly as your provider gives it to you.

Here’s a helpful setup routine:

  1. Ask your host for the current email setup instructions.
  2. Choose IMAP if you want to use the account on multiple devices.
  3. Enter the server names, username, and other required details.
  4. Match the security options to your provider’s instructions.
  5. Send a test message, then check your inbox and sent folder.

Don’t guess at server names or security settings. Different hosting companies can use different configurations. If automatic setup fails, your provider can confirm the correct details.

What to check when email stops working

If your app suddenly stops sending or receiving, start by signing in to webmail. If webmail works, your mailbox is likely reachable, and the issue may be in the app’s settings or connection.

Check the app’s incoming and outgoing server names, username, password, and security settings against your provider’s instructions. Also confirm that the app is online and not holding messages in an Outbox.

If webmail also fails, check that you’re using the right address and password. Look in your spam or junk folder for messages that seem missing. Check for a full-mailbox warning, too. Delete or archive older messages when appropriate, and save important items before clearing anything.

If mail still doesn’t arrive, contact your hosting provider. They may be able to check the mail queue or server logs for delivery information. These details can help distinguish a mailbox problem from an app problem.

Keep your business email protected

Use a strong, unique password for your email account. Turn on two-factor authentication if your provider offers it. This adds another verification step when you sign in.

Never send passwords in plain-text email. An inbox can be forwarded, accessed on several devices, or exposed if an account is compromised. Share account details only through a secure method recommended by your provider.

Also back up messages or attachments you can’t afford to lose. Synchronization is useful, but it is not the same as a separate backup. Keep important records somewhere secure and accessible to your business.

A practical place to start

For a beginner, webmail is often the easiest first step. Sign in and confirm that your mailbox works. When you’re ready for notifications or offline reading, set up an email client using your host’s instructions.

If the app has trouble, test webmail before changing settings. When webmail works and the app doesn’t, that’s a useful clue: the problem is likely in the app configuration.

The CharlesWorks Corner handles email services for clients, including help with account setup and troubleshooting. Visit cwcorner.com to learn more. Start with the access method that feels comfortable, and change it later if your work habits change.

FacebooktwitterredditpinterestlinkedinmailFacebooktwitterredditpinterestlinkedinmail

The CW Corner – Those “We Watched You On Adult Sites” Emails Are Scams

Just thought I would post this informational piece reassuring you that those “We Watched You On Adult Sites” sextortion emails are scams!

The Email That Shocks People

I have seen these emails for many years.

They usually start with a nasty claim.

The sender says they hacked your computer.

Then they say they watched you visit adult websites.

Next, they claim they recorded you through your camera.

After that, they demand money, usually in cryptocurrency.

Finally, they threaten to send the “video” to your contacts.

That message scares people fast.

It uses shame, fear, confusion, and urgency.

That is exactly why scammers send it.

They do not need to hack everyone.

They only need to scare enough people.

The Big Secret About These Emails

Most of these emails are complete garbage.

The scammer does not have a video.

The scammer did not watch you.

The scammer did not hack your camera.

The scammer probably does not know you.

The scammer usually only has your email address.

Sometimes they also have an old password.

That old password may scare people even more.

However, that password often came from an old breach.

It may have nothing to do with your current email account.

That detail gives the scam more punch.

The scammer wants you to think, “Oh no, they know me.”

That is the hook.

Why They Mention Adult Websites

The adult website claim does a lot of work.

First, it creates embarrassment.

Second, it makes people hesitate to ask for help.

Third, it makes people panic.

Fourth, it makes people act alone.

That is exactly what the scammer wants.

Scammers love silence.

They want you scared, ashamed, and isolated.

They do not want you calling your web person.

They do not want you asking your spouse.

They do not want you asking your office manager.

They want you thinking in panic mode.

Panic makes people click.

Panic makes people pay.

Panic makes smart people ignore common sense.

The Psychology Behind The Scam

These scams work because they hit deep human fears.

Most people fear public embarrassment.

Most people fear losing trust.

Most people fear family conflict.

Most people fear business damage.

Most people fear being judged.

The scammer pushes all those buttons at once.

That makes the message feel powerful.

However, the message only has power if you believe it.

Once you understand the trick, it loses its teeth.

It becomes spam with a costume on.

An ugly costume, yes.

But still spam.

They Use Urgency To Shut Down Thinking

Most of these emails include a deadline.

They may say you have 24 hours.

They may say you have 48 hours.

They may claim a timer started when you opened the email.

That is nonsense.

They want you to move fast.

They know calm people ask questions.

They know calm people check facts.

They know calm people call support.

So they try to steal your calm.

They try to rush you.

That rushed feeling matters.

Whenever a message screams “act now,” slow down.

That rule saves people from many scams.

They Use Technical Jargon To Sound Real

The emails often include computer words.

They may mention malware.

They may mention spyware.

They may mention remote access.

They may mention operating systems.

They may mention your router.

They may mention your camera.

They may mention tracking pixels.

They may mention your browser history.

Most of that talk means nothing.

The scammer throws technical words like confetti.

They hope one word sounds scary enough.

They do not need accuracy.

They need fear.

A real technician can usually spot the nonsense quickly.

But regular users may feel overwhelmed.

That is part of the trap.

They Want Cryptocurrency For A Reason

These scammers usually demand Bitcoin or another cryptocurrency.

They do this because crypto payments move differently.

Banks can sometimes reverse or trace certain payments.

Credit card companies may help fraud victims.

However, crypto payments usually do not work that way.

Once you send the money, it often disappears.

That is why scammers love it.

They also know many people find crypto confusing.

Confusion helps the scammer.

The harder the payment process feels, the more serious it may seem.

That is another trick.

A complicated payment does not prove a real threat.

It only proves the scammer wants hard-to-recover money.

Your Email Address On The Dark Web

People often panic when they hear “dark web.”

That phrase sounds terrifying.

However, an email address on a leaked list means very little.

Your email address may appear in many places.

A store may leak it.

A service provider may leak it.

A social website may leak it.

A newsletter company may leak it.

An old vendor may leak it.

That does not mean your mailbox was hacked.

It means your address joined spammer lists.

That can increase junk mail.

It can also increase targeted scaremail.

Still, the address alone gives them no magic power.

They cannot control your account because they know your address.

They need your password too.

They may also need a second security step.

Old Passwords Make The Scam Feel Real

Some scam emails include a password.

That scares people more than anything else.

I understand why.

Seeing a real password in a threat feels personal.

However, that password often came from an old breach.

Maybe you used it years ago.

Maybe you used it on another website.

Maybe that website stored passwords badly.

Then criminals dumped the stolen data online.

Later, another scammer grabbed that list.

Now they send scary emails using old passwords.

That does not prove they logged into your current email.

It proves they found old leaked data.

Still, you should never ignore that clue.

Change any account that still uses that password.

Never reuse that password again.

Why Smart People Fall For It

Smart people fall for scams every day.

That does not make them foolish.

It makes them human.

Scammers do not attack intelligence first.

They attack emotions first.

They attack fear.

They attack shame.

They attack urgency.

They attack trust.

They attack exhaustion.

They attack busy mornings.

They attack stressful afternoons.

They attack people during real life.

A business owner may read the email between customers.

A parent may read it while handling family stress.

An employee may read it before a meeting.

That timing helps scammers.

The scammer only needs one bad moment.

The Scammer Plays A Numbers Game

These criminals send huge numbers of messages.

They do not need most people to pay.

They only need a small number.

Suppose they send 100,000 emails.

Suppose only 20 people pay.

That can still make the scam profitable.

That is why these scams keep coming.

They work often enough.

They cost almost nothing to send.

They also reach people around the world instantly.

That ugly math keeps the scam alive.

They Copy And Reuse The Same Scripts

I have seen these messages many times.

They change a few words.

They change the payment wallet.

They change the deadline.

They change the claimed method.

But the story stays mostly the same.

They say they hacked you.

They say they watched you.

They say they recorded you.

They say they will expose you.

They say you must pay quickly.

That script has circulated for years.

The scammer may sound personal.

But most messages are mass-produced.

They read like form letters with threats added.

Sometimes They Spoof Your Own Address

Some versions look like they came from your own email address.

That really scares people.

They think, “They must control my account.”

Not necessarily.

Email spoofing can fake the visible sender address.

It works like writing a fake return address on an envelope.

The message may look like it came from you.

But the mail server records often tell another story.

That is why headers matter.

A proper mail check can show whether the account sent it.

Most users never see those details.

So the fake sender line does its job.

It creates fear.

What Real Account Compromise Looks Like

A real hacked mailbox usually leaves signs.

You may see strange messages in Sent Items.

You may find deleted messages you never deleted.

You may see forwarding rules you never created.

You may find filters moving mail secretly.

You may receive password reset notices.

You may see login alerts from strange locations.

Your contacts may receive spam from your account.

Your mailbox may suddenly lock you out.

Those signs deserve fast attention.

A scary sextortion email alone does not prove compromise.

It proves someone sent you a scary email.

That is different.

What To Do When You Receive One

Do not reply.

Do not pay.

Do not click links.

Do not open attachments.

Do not scan strange quick response codes.

Do not call phone numbers inside the message.

Do not negotiate.

Do not explain yourself.

Do not threaten the scammer.

Do not send any personal information.

Mark the message as spam or junk.

Then delete it.

If you feel unsure, ask a trusted technical person.

A second set of eyes helps.

Scammers hate second opinions.

When You Should Change Passwords

Change your email password if you feel unsure.

That step can bring peace of mind.

Also change it if the email shows an old password.

Change it if you reused that password anywhere.

Change it if your account shows strange activity.

Change it if you cannot remember when you last changed it.

Use a strong password.

Use a unique password.

Do not reuse passwords across accounts.

A reused password turns one breach into many problems.

That risk causes real trouble.

Why Password Reuse Hurts People

Many people use the same password everywhere.

I understand why.

Nobody wants to remember dozens of passwords.

However, password reuse creates a big risk.

One weak website can expose your password.

Then criminals try that password on email.

They try it on banking websites.

They try it on shopping accounts.

They try it on social media.

They try it on web hosting accounts.

This attack has a name.

People call it credential stuffing.

The scammer stuffs known passwords into other login pages.

If you reused the password, they may get in.

That is why unique passwords matter.

Use A Password Manager If Possible

A password manager can help a lot.

It stores strong passwords for you.

It also creates different passwords for each site.

That means one breach does not unlock everything.

Some people prefer written password books.

That can still beat password reuse.

The main goal stays simple.

Use different passwords for important accounts.

Email matters most.

Your email account often unlocks everything else.

Password reset links usually go there.

Protect email like the front door.

Turn On Two-Step Login When Available

Two-step login adds another layer.

People also call it multi-factor authentication.

That means a password alone does not open the account.

The account also needs a code or approval.

This extra step blocks many attacks.

It does not stop every scam.

But it helps greatly.

Use it on email when available.

Use it on banking accounts.

Use it on domain registrar accounts.

Use it on web hosting accounts.

Use it on social media.

Use it anywhere that matters.

Businesses Need Extra Caution

Business email carries extra risk.

A hacked business mailbox can cause serious damage.

Scammers may read invoices.

They may watch customer conversations.

They may change payment instructions.

They may impersonate employees.

They may trick customers.

They may steal files.

They may reset passwords for other services.

So businesses should treat mailbox security seriously.

That does not mean every scary email proves a hack.

It means we should check calmly.

Good checks beat panic every time.

What I Check For Customers

When a customer calls me about these emails, I look for real signs.

I check recent logins when possible.

I check sent mail.

I check forwarding settings.

I check autoresponders.

I check mailbox rules.

I check suspicious password reset messages.

I check whether contacts received spam.

I also ask what the email actually said.

Many times, the message matches the same old scam script.

At that point, I can usually reassure the customer.

Then we change passwords if needed.

That gives both safety and peace of mind.

Why The Messages Sound So Disgusting

The disgusting wording serves a purpose.

The scammer wants an emotional reaction.

Gross language causes shock.

Shock shortens thinking.

The more disgusting the email feels, the less likely people share it.

That helps the scammer.

The victim may feel embarrassed even discussing it.

But nobody should feel embarrassed.

The scammer wrote the garbage.

The victim only received it.

That difference matters.

Receiving filth does not make someone guilty.

It makes them a target.

The Threat To Send It To Contacts

This threat appears in many versions.

The scammer may claim they copied your contacts.

They may claim they will email everyone.

They may mention family, friends, or coworkers.

That threat works because relationships matter.

People naturally want to protect loved ones.

They also want to protect reputations.

The scammer knows that.

So they threaten social damage.

Most of the time, they have nothing.

They only have words.

They hope your imagination does the rest.

The Fake Timer Trick

Some messages claim they know when you opened the email.

Some claim a timer started at that moment.

Some claim they installed tracking software.

Most of this is nonsense.

Regular marketing emails can use tracking pixels.

That only shows whether someone opened a message.

It does not prove hacking.

It does not prove camera access.

It does not prove device control.

The scammer uses simple ideas to create fear.

Again, they need panic.

They do not need truth.

Why They Mention Malware

Malware sounds scary.

So scammers mention it often.

They may claim they installed a “Trojan.”

They may claim they control your screen.

They may claim they copied your files.

They may claim your antivirus missed it.

Sometimes malware infections do happen in real life.

But these emails usually provide no real proof.

They do not show a file.

They do not show a screenshot.

They do not show real details.

They only make broad claims.

Broad claims require broad doubt.

Ask For Proof Without Replying

Here is the funny part.

Real attackers usually prove access quickly.

They may show a real screenshot.

They may list files.

They may send logs.

They may show recent private data.

These sextortion scammers usually show none of that.

They just make claims.

However, do not reply and ask for proof.

That only confirms your address works.

It may invite more messages.

Instead, ask your technical support person.

Let them review the message safely.

Why Paying Makes Things Worse

Paying does not buy safety.

Paying marks you as profitable.

The scammer may demand more.

Other scammers may target you later.

They may share your address with more criminals.

They may say the first payment failed.

They may invent another fee.

They may keep threatening you.

Scammers do not honor agreements.

Their whole business runs on lies.

So paying rarely ends the problem.

It can make it grow.

What To Tell Employees

Employees need simple rules.

Do not panic.

Do not reply.

Do not pay.

Do not click.

Report the message.

Save it for review if needed.

Then let the right person inspect it.

That process protects the business.

It also protects the employee from embarrassment.

Make sure staff know these scams exist.

People handle threats better when they expect them.

Surprise helps scammers.

Training removes surprise.

What To Tell Family Members

Family members need reassurance first.

These messages can feel deeply upsetting.

Start by saying, “This is a common scam.”

Then explain the basic trick.

Tell them the scammer likely has no video.

Tell them not to answer.

Tell them not to send money.

Tell them you can help check the account.

That calm response matters.

Fear shrinks when people feel supported.

Nobody should face these emails alone.

Why Older Adults Get Targeted

Scammers often target older adults.

But they also target everyone else.

Older adults may have more savings.

They may feel less confident with technology.

They may also respect official-sounding messages.

However, younger people fall for scams too.

These criminals do not care about age.

They care about fear and money.

Still, older adults deserve extra patience.

Nobody should shame someone for asking.

Asking for help means the scammer lost.

Why Business Owners Get Targeted

Business owners publish contact information everywhere.

They list email addresses on websites.

They appear in directories.

They register domains.

They join networking groups.

They advertise services.

That public visibility helps customers.

It also helps scammers find targets.

So business owners often receive more junk.

That does not mean they did anything wrong.

It means they operate in public.

A public email address attracts spam.

That is just the ugly side of doing business online.

The Role Of Data Breaches

Data breaches feed these scams.

A breach may expose names.

It may expose email addresses.

It may expose phone numbers.

It may expose mailing addresses.

It may expose old passwords.

It may expose customer records.

Scammers combine those pieces.

Then they create messages that feel personal.

A message with your name feels stronger.

A message with your old password feels stronger.

A message after a known breach feels stronger.

But stronger does not mean true.

It only means more convincing.

What “Dark Web” Really Means Here

The dark web sounds mysterious.

Sometimes criminals do sell stolen data there.

However, many leaked lists also circulate elsewhere.

Scammers may buy or download those lists.

Then they blast messages to thousands of people.

So “your email is on the dark web” often means this.

Your address exists in stolen or shared spammer data.

That is unpleasant.

But it does not automatically mean disaster.

It means you should use better password habits.

It also means you should expect more phishing.

The Difference Between Spam And A Hack

Spam means someone sent you unwanted mail.

A hack means someone gained access.

Those are very different things.

A spammer can email anyone.

They do not need your password.

They do not need your computer.

They only need your address.

A hacker needs access.

They need credentials, malware, or another weakness.

Do not confuse receiving a threat with being hacked.

That mistake causes needless panic.

It also helps the scammer.

Why Checking Headers Helps

Email headers show the path a message took.

They can reveal sending servers.

They can show authentication results.

They can show whether mail passed security checks.

Headers look confusing.

I do not expect most users to read them.

But support people can use them.

Headers help separate spoofing from real account use.

They also help spot forged sender addresses.

That is why I like seeing the original email.

Screenshots help sometimes.

Original headers help much more.

Never Trust The Display Name Alone

Email programs often show friendly names.

That display name can say almost anything.

It may say your name.

It may say your company name.

It may say your bank.

It may say Microsoft.

It may say your own email address.

That does not prove anything.

Look at the actual address.

Even then, remember spoofing exists.

The display name gives scammers a costume.

Do not trust the costume.

Check the source.

Phone Scams Use Similar Psychology

Email scams and phone scams use the same tricks.

A caller may claim to be from a bank.

They may claim fraud already happened.

They may claim police action will follow.

They may claim your computer has viruses.

They may claim your account will close.

They push fear and urgency.

Then they demand action.

They may tell you not to hang up.

They may tell you not to call anyone.

That is a giant warning sign.

Real help does not fear verification.

Scammers do.

The Bank Scam Pattern

A fake bank caller may sound professional.

They may know some real information.

They may spoof the bank phone number.

They may say your account faces danger.

Then they ask for codes, passwords, or transfers.

That pattern resembles sextortion scams.

Both scams create fear.

Both scams demand fast action.

Both scams isolate the victim.

Both scams punish calm thinking.

That is why the same safety rule works.

Stop.

Breathe.

Verify independently.

Use a known phone number.

Do not use the number they provide.

Why Shame Keeps Scams Alive

Shame gives scammers cover.

People feel embarrassed.

So they hide the message.

Then they make decisions alone.

That is dangerous.

Nobody should feel ashamed for receiving a scam.

The criminal chose the topic.

The criminal chose the words.

The criminal created the threat.

The recipient did nothing wrong.

Talking about these emails breaks the scammer’s power.

That is why I keep writing about them.

People need plain warnings before panic strikes.

How To Respond As A Business

A business should have a simple reporting process.

Staff should know where to send suspicious emails.

They should know not to click.

They should know not to reply.

They should know not to forward dangerous attachments casually.

They should know to ask for help.

The process should feel safe.

If employees fear blame, they may hide mistakes.

That helps scammers.

A good business culture rewards quick reporting.

Fast reporting protects everyone.

What I Would Tell A Customer

I would say this plainly.

“You received a common scam email.”

“The sender probably did not hack you.”

“They likely got your address from a leaked list.”

“Do not pay them.”

“Do not answer them.”

“We can change your password as a precaution.”

“We can also check your account for suspicious activity.”

That message calms people.

It also gives them action steps.

Fear needs a plan.

A plan restores control.

What Counts As A Real Emergency

Some signs deserve immediate action.

You cannot log into your mailbox.

Customers report spam from your address.

You see strange sent messages.

You find forwarding rules you did not create.

You receive many password reset alerts.

You see successful logins from strange locations.

Money movement instructions changed unexpectedly.

Your website admin account shows strange logins.

Those signs need quick work.

Change passwords.

Check recovery addresses.

Review mailbox rules.

Contact support.

Do not wait.

Why Scammers Keep Using This Exact Scam

They keep using it because it works.

They do not need creativity.

They need results.

Fear works.

Shame works.

Urgency works.

Technical confusion works.

Cryptocurrency confusion works.

Old breached passwords work.

So they keep recycling the same idea.

That does not mean the threat is real.

It means the scam still makes money.

Scams survive when people pay.

Education cuts their income.

Teach People Before They Get Hit

The best time to explain this scam comes before someone receives it.

A calm person learns better.

A frightened person struggles to process details.

So share examples.

Explain the pattern.

Explain the fake threats.

Explain the payment demand.

Explain the no-reply rule.

Explain password safety.

Then people recognize the scam later.

Recognition changes everything.

The message still looks ugly.

But it no longer feels mysterious.

A Simple Rule For Scary Messages

Here is one rule I like.

The scarier the message sounds, the slower you should move.

Scammers want speed.

You should choose delay.

Scammers want secrecy.

You should ask someone trusted.

Scammers want payment.

You should verify first.

Scammers want panic.

You should breathe.

That rule works for email.

It works for phone calls.

It works for text messages.

It works for fake invoices.

It works for many online threats.

What Not To Do

Do not send money.

Do not send gift cards.

Do not send cryptocurrency.

Do not send passwords.

Do not send verification codes.

Do not install remote access software.

Do not let a stranger control your computer.

Do not click links in the threat.

Do not open attachments.

Do not continue a conversation with the scammer.

Every one of those actions helps them.

The safest response usually feels boring.

Ignore, report, delete, and secure your accounts.

Boring beats broke.

Why Reporting Still Matters

Reporting helps mail systems learn.

Mark the message as spam or junk.

That can improve filtering.

Businesses may also save samples for review.

Support teams can inspect patterns.

They can block sending sources.

They can update filters.

They can warn other users.

Reporting does not always stop every message.

But it helps.

Deleting alone removes your copy.

Reporting may help protect others.

The Human Side Of This

These emails upset real people.

I have seen customers feel embarrassed.

I have seen people feel afraid.

I have seen people worry about family damage.

I have seen business owners fear reputation harm.

That reaction makes sense.

The scammer designed the email to hurt.

So we should respond with patience.

We should not laugh at the victim.

We can laugh at the scam.

But we should support the person.

Calm support beats shame.

My View After 28 Years In This Business

I have been in this business for over 28 years.

I have seen nearly every scam angle.

I have received endless phishing emails.

I have received scam phone calls.

I have seen fake invoices.

I have seen fake domain renewals.

I have seen fake bank alerts.

I have seen fake tech support warnings.

I have seen fake password threats.

I have seen fake sextortion emails.

The wording changes.

The trick stays the same.

They want fear to outrun judgment.

That is the whole game.

Final Advice

Do not let these emails control you.

They look nasty.

They sound personal.

They feel urgent.

But they usually come from bulk scam operations.

Treat them like criminal junk mail.

Do not reply.

Do not pay.

Do not click.

Change passwords when needed.

Use unique passwords.

Turn on two-step login where possible.

Ask a trusted support person when unsure.

Most importantly, do not let shame silence you.

That silence helps the scammer.

A calm conversation usually destroys the scam.


You can see more at https://CharlesWorks.com/resources.

FacebooktwitterredditpinterestlinkedinmailFacebooktwitterredditpinterestlinkedinmail

The CW Corner – Quick Tips: Protect Your Inbox from Incoming Phishing Attacks in 2025

Phishing DevilPhishing attacks have become more sophisticated than ever in 2025. Cybercriminals now use AI to craft convincing emails that mimic your trusted contacts perfectly. They’re targeting small businesses more aggressively because they know you might not have enterprise-level security budgets.

But here’s the good news: protecting your inbox doesn’t require expensive solutions or a computer science degree. You just need to know what to look for and implement a few key safeguards. Think about what’s connected to your email accounts – your banking, your customer data, your business operations. That’s why phishing avoidance should be your top priority this year.

Let’s dive into practical steps you can take today to bulletproof your inbox against these increasingly clever attacks.

Set Up Email Authentication to Block Impersonators

Email authentication is your first line of defense against domain spoofing. When someone tries to send emails pretending to be from your business, these protocols will catch them.

SPF (Sender Policy Framework) tells email servers which IP addresses are allowed to send emails from your domain. Think of it as a guest list for your domain – only approved senders get through.

DKIM (DomainKeys Identified Mail) adds a digital signature to your outgoing emails. It’s like a tamper-proof seal that proves the message really came from you and wasn’t altered in transit.

DMARC (Domain-based Message Authentication, Reporting, and Conformance) combines SPF and DKIM, then tells other email servers what to do with emails that fail these checks. You can set it to quarantine suspicious emails or reject them entirely.

Setting up these protocols requires adding DNS records to your domain. If that sounds intimidating, most hosting providers or IT consultants can handle this quickly. The investment pays off immediately – you’ll see fewer spoofed emails reaching your contacts and customers.

Recognize the New Generation of Phishing Emails

Today’s phishing emails are getting scary good at mimicking legitimate communications. AI helps scammers create perfect grammar, use your company’s writing style, and even reference recent events or conversations.

Watch for these red flags that still give away phishing attempts:

Suspicious sender addresses often use lookalike domains. Instead of “fedex.com,” you might see “fedx-support.com” or “fedex-delivery.net.” Always check the actual sender address, not just the display name.

Urgent language designed to bypass your critical thinking. Phrases like “immediate action required,” “account will be closed,” or “verify within 24 hours” should trigger your skepticism.

Generic greetings like “Dear Customer” instead of your actual name. Legitimate businesses usually personalize their communications, especially for account-related messages.

Mismatched links where the displayed text says one thing but the actual URL leads somewhere else. Hover over links before clicking to see where they really go.

Unexpected attachments requiring immediate download or execution. Be especially wary of .zip files, .exe files, or documents with embedded macros from unknown senders.

Implement Smart Behavioral Practices

Your daily email habits matter more than any security software. Small changes in how you handle emails can prevent most successful phishing attacks.

Never click links in emails unless you absolutely trust the sender. When in doubt, open a new browser window and navigate to the company’s website directly. This simple practice stops most credential theft attempts cold.

Verify suspicious requests through alternative channels. If your “boss” emails asking for urgent wire transfers or sensitive information, pick up the phone and confirm. Scammers count on you following email instructions without verification.

Keep your software updated. Email clients, browsers, and operating systems regularly patch security vulnerabilities that phishers exploit. Enable automatic updates whenever possible.

Use different passwords for different accounts. When one account gets compromised, you don’t want attackers accessing everything else. Password managers make this easier by generating and storing unique passwords for each service.

Deploy Multi-Factor Authentication Strategically

Multi-factor authentication (MFA) blocks most phishing attacks even when criminals steal your password. But not all MFA is created equal in 2025.

Avoid SMS-based authentication when possible. Scammers can intercept text messages or use social engineering to redirect your phone number. It’s better than nothing, but other options provide stronger protection.

App-based authentication using Google Authenticator or Microsoft Authenticator offers better security. These generate time-based codes that work even without internet connectivity.

Hardware security keys like YubiKey provide the strongest protection against phishing. They use cryptographic proof that can’t be phished, even by sophisticated attacks. For businesses handling sensitive data, this investment pays for itself quickly.

Choose the Right Email Security Tools

Modern email security goes beyond basic spam filtering. AI-powered solutions can detect subtle patterns that humans might miss.

Advanced threat protection services analyze email content, sender behavior, and link destinations in real-time. They catch zero-day phishing attempts that haven’t been reported yet.

Email sandboxing opens suspicious attachments in isolated environments to check for malware before they reach your inbox. This protects against document-based attacks that bypass traditional antivirus.

User reporting tools make it easy for your team to flag suspicious emails. Many security platforms learn from these reports, improving protection for everyone.

Link rewriting services intercept clicks on suspicious URLs and scan them before allowing access. This provides a safety net when users click without thinking.

Train Your Team Without Boring Them

Security awareness training works best when it’s relevant and engaging. Skip the generic presentations and focus on real scenarios your business might face.

Run phishing simulations that mimic actual threats targeting your industry. Banking clients might see fake loan notifications, while retail businesses could see shipping updates. Make the training relevant to daily operations.

Create a no-blame reporting culture. Team members should feel comfortable reporting suspicious emails without fear of embarrassment. Praise people for being cautious – it’s exactly the behavior you want.

Share recent examples of phishing attempts targeting similar businesses. Real-world cases are more memorable than theoretical scenarios.

Keep sessions short and focused. Fifteen-minute monthly updates work better than annual marathon training sessions. People retain information better in small, digestible pieces.

Protect Your Business Email Specifically

Business email faces unique threats that personal email doesn’t encounter. Attackers research your company structure, recent news, and business relationships to craft targeted attacks.

Business Email Compromise (BEC) attacks target financial processes. Scammers impersonate executives or vendors to trick employees into wire transfers or credential sharing. Always verify payment requests through secondary channels.

Supply chain phishing uses compromised vendor accounts to attack customers. Even trusted partners can become unwitting attack vectors. Maintain healthy skepticism even with familiar senders.

CEO fraud targets employees with fake urgent requests from leadership. Attackers study your organizational chart and communication patterns to make requests seem legitimate.

Keep Your Defenses Current

Phishing tactics evolve constantly, so your protection strategies must evolve too. What worked last year might not catch this year’s threats.

Monitor your email authentication reports. DMARC generates reports showing who’s trying to send emails from your domain. Review these monthly to catch impersonation attempts early.

Update your security awareness training quarterly with new threat examples. Cybercriminals adapt their tactics based on what works, so your team needs to stay current.

Test your backup and recovery procedures. Even with perfect prevention, some attacks might succeed. Regular testing ensures you can recover quickly without paying ransoms or losing critical data.

Review and update your incident response plan. Everyone should know who to contact and what steps to take when phishing attacks succeed. Quick response can minimize damage significantly.

Take Action Today

Phishing avoidance isn’t something you can set up once and forget. It requires ongoing attention and regular updates. But the effort protects your business reputation, customer data, and financial security.

Start with email authentication – SPF, DKIM, and DMARC records provide immediate protection against domain spoofing. Then implement multi-factor authentication on critical accounts. These two steps alone will block most common phishing attacks.

Train your team to recognize and report suspicious emails. Create processes for verifying unexpected requests through alternative communication channels. The combination of technology and smart human behavior creates a robust defense against even sophisticated attacks.

Remember, cybercriminals are running businesses too. They target victims who look like easy marks and move on when defenses are strong. Make your business a hard target, and attackers will focus their efforts elsewhere.

For additional technical help with email security implementation, check out our email security resources for step-by-step guidance on protecting your business communications.

FacebooktwitterredditpinterestlinkedinmailFacebooktwitterredditpinterestlinkedinmail

The CW Corner – SPF, DKIM, DMARC Explained in Under 3 Minutes (Why Your Business Email Needs All Three)


Two minute explanation of spf, dkim and dmarcThink your business emails are secure? Think again. Every day, cybercriminals send millions of fake emails pretending to be from legitimate businesses. Without proper email authentication, your company name could be next.

Here’s the scary truth: anyone can send an email that appears to come from your domain. Your customers won’t know the difference until it’s too late. That’s where SPF, DKIM, and DMARC come in.

These three protocols work like a security team for your email. Each one handles a different job, and you need all three to properly protect your business reputation.

What Is SPF (Sender Policy Framework)?

SPF acts like a bouncer at an exclusive club. It tells the world exactly which mail servers are allowed to send emails on behalf of your domain.

When you set up SPF, you’re essentially creating a list that says “These servers, and only these servers, can send emails from mydomain.com.” Any email claiming to be from your domain but sent from an unauthorized server gets flagged as suspicious.

Here’s how it works in practice. Let’s say someone tries to send a fake email from your domain using their personal Gmail account. The receiving email server checks your SPF record and sees that Gmail isn’t on your approved list. Red flag raised.

But SPF has one major weakness: email forwarding breaks it completely. When someone forwards your legitimate email to another address, the forwarding server becomes the new sender. Since that server isn’t on your SPF list, the email fails authentication even though it’s genuine.

That’s why SPF alone isn’t enough. You need backup.

Understanding DKIM (DomainKeys Identified Mail)

DKIM works like a tamper-proof seal on a package. Every email gets a unique digital signature that proves two things: the message came from an authorized server, and nobody changed the content during delivery.

Think of DKIM as invisible ink that only special equipment can read. Your mail server adds this signature using a private key that only you control. The receiving server uses a public key (stored in your DNS records) to verify the signature.

If someone intercepts your email and changes even one character, the signature breaks. The receiving server immediately knows something fishy happened.

Unlike SPF, DKIM survives email forwarding because the signature travels with the message. But DKIM has its own blind spot: it doesn’t check if the “From” address matches the domain that signed the email.

A scammer could send an email that appears to come from your domain in the “From” field while actually signing it with their own domain’s DKIM key. The signature would be valid, but the email would still be fake.

DMARC: The Missing Link

DMARC (Domain-based Message Authentication, Reporting & Conformance) is the quarterback that makes SPF and DKIM actually work together effectively.

DMARC connects the dots by checking something called “alignment.” It verifies that the domain in the “From” address matches the domain that passed SPF or DKIM authentication.

But DMARC’s real power lies in policy enforcement. You tell DMARC exactly what to do when an email fails authentication:

  • None: Just monitor and report (perfect for testing)
  • Quarantine: Send suspicious emails to spam folders
  • Reject: Block fake emails completely

DMARC also sends you detailed reports about who’s sending emails using your domain. These reports help you catch both legitimate configuration issues and malicious activity.

How the Three Work as a Team

Think of email authentication like airport security. You need multiple checkpoints to catch different types of threats.

When an email arrives, the receiving server performs this security screening:

  1. SPF Check: Is this email coming from an authorized server?
  2. DKIM Check: Is the digital signature valid and unaltered?
  3. DMARC Check: Do the domains align properly, and what should I do if they don’t?

DMARC requires that at least one of the other protocols (SPF or DKIM) passes AND shows proper alignment. If both fail, DMARC policies kick in to protect the recipient.

This layered approach covers all the bases. Even if SPF breaks due to forwarding, DKIM can still authenticate the email. If DKIM fails for some reason, SPF might still pass.

Why All Three Are Non-Negotiable

You might think “Can’t I just use one or two?” Unfortunately, no. Each protocol plugs holes that the others can’t handle.

Here’s what happens with incomplete protection:

SPF only: Scammers can still forge your domain in the “From” address while sending from their own authenticated servers. Customers see your name and trust the email.

DKIM only: Criminals can use your domain name in emails while signing with their own valid DKIM signature. The technical authentication passes, but the email is still fraudulent.

SPF + DKIM without DMARC: You have no enforcement mechanism. Email providers might ignore your SPF and DKIM records because there’s no policy telling them what to do with failures.

The harsh reality? Without all three protocols properly configured, up to 76% of your legitimate business emails could end up in spam folders or get rejected outright.

The Business Impact Is Real

Major email providers aren’t playing games anymore. Starting in February 2024, Google and Yahoo made SPF, DKIM, and DMARC mandatory for anyone sending over 5,000 emails per day.

But compliance isn’t the only concern. Business Email Compromise (BEC) scams cost U.S. victims $2.9 billion in 2024 alone. When criminals can easily impersonate your business, your customers become targets.

Consider what’s at stake when someone spoofs your domain:

  • Customer trust: People stop opening emails from your business
  • Brand reputation: Your company name gets associated with scams
  • Financial liability: Customers might hold you responsible for losses
  • Email deliverability: Legitimate emails get blocked or filtered

One major breach can take years to recover from. Prevention costs far less than damage control.

Getting Started: Your Next Steps

Don’t let the technical details intimidate you. Most hosting providers and email services can help you implement these protocols correctly.

Start by checking your current status. Tools like MXToolbox or DMARC Analyzer can show you what records already exist for your domain.

If you’re sending business emails without proper authentication, you’re essentially driving without insurance. The question isn’t whether something will go wrong: it’s when.

For comprehensive email security guidance tailored to your business needs, our email security services can help you implement all three protocols correctly.

The investment in proper email authentication pays dividends in protected reputation, improved deliverability, and peace of mind. Your customers: and your bottom line: will thank you for taking email security seriously.

Don’t wait for a crisis to take action. Email authentication isn’t just about preventing attacks; it’s about ensuring your legitimate business communications actually reach their intended recipients.

FacebooktwitterredditpinterestlinkedinmailFacebooktwitterredditpinterestlinkedinmail

The CW Corner – Is Your Email Really Private? Here’s the Truth About Business Email Security in 2025

Here’s the uncomfortable truth: your business emails probably aren’t as private as you think. If you’re using Gmail, Yahoo, or Outlook for sensitive communications, you’re essentially trading your privacy for convenience. Most people assume their emails are protected, but the reality is far more concerning.

Think about what’s connected to your email accounts. Banking notifications, client contracts, internal discussions, vendor communications, all flowing through systems that treat your messages as data to be analyzed and monetized.

Why Your “Private” Email Isn’t Actually Private

Most popular email services scan your inbox content, track your behavior, and monetize your data. This practice is buried in lengthy terms of service that few people read. Gmail, for instance, lacks end-to-end encryption and actively analyzes user data for targeted advertising.

Here’s what actually happens to your emails:

  • Content gets scanned for advertising insights
  • Metadata gets collected and stored indefinitely
  • Behavioral patterns get tracked across services
  • Your data becomes a product to be sold

The global Email Encryption market jumped from $11.9 billion in 2024 to a projected $36.2 billion by 2030. That’s not coincidence, it’s people waking up to privacy reality.

What Real Email Privacy Actually Looks Like

True email privacy requires specific technical safeguards that most providers simply don’t offer. Here’s what genuinely private email includes:

Zero-access encryption means even your email provider can’t read your messages. Your emails get encrypted directly on your device before transmission. Only the intended recipient can decrypt them.

No data mining ensures your communications can’t be sold or analyzed for advertising. Your messages remain yours alone.

Secure signup processes keep your account creation details private. No sharing with third parties or cross-platform tracking.

Disposable addresses let you create temporary email addresses for specific purposes. This reduces your digital footprint and protects your primary inbox from spam.

The Growing Threat Landscape Targeting Your Business

Email security in 2025 is deteriorating rapidly. Cyber criminals send an estimated 3.4 billion malicious emails daily. That’s not a typo: billion with a ‘B’. And 87% of security professionals report their organizations encountered AI-driven cyber attacks in the last year.

Business Email Compromise (BEC) attacks represent the biggest threat to your bottom line. These attacks accounted for 73% of all reported cyber incidents in 2024. Even small companies face serious risk: businesses with fewer than 1,000 employees have a 70% weekly probability of experiencing at least one BEC attack.

The financial damage is staggering. BEC attacks cost an average of $4.89 million per incident. The average wire transfer request in a BEC attack was $24,586 at the start of 2025. Among organizations working with Managed Service Providers, one in five lost money through BEC attacks over the previous 12 months.

Specific Threats Targeting Your Inbox Right Now

Phishing remains the top concern for IT leaders, with 47% ranking it as their primary worry. Approximately 66% of phishing attempts target organizational resources using credential theft and fake billing documents. The remaining 34% go after personal information, particularly financial data.

Microsoft 365 users face heightened risk. A concerning 79% of M365 users experienced cyber incidents in 2025. In healthcare specifically, 52% of breaches now occur on Microsoft 365: up from 43% in 2024.

Pretexting attacks nearly doubled in frequency last year. These sophisticated impersonation tactics fool employees into believing they’re communicating with trusted executives or partners. Attackers research their targets extensively before striking.

Small businesses get hit hardest because they often lack dedicated IT security staff. For every 323 emails a small business receives, one contains malware or phishing attempts.

For more specific guidance on email security measures, check out our detailed guide at The CW Corner Email Security.

What Email Security Protocols Actually Protect

Proper email security establishes three fundamental protections that work together:

Confidentiality ensures only intended recipients can read your email content. This involves encryption during transmission and storage.

Integrity guarantees your message arrives exactly as you sent it. No tampering or modification occurs during delivery.

Authenticity proves emails actually come from their claimed sender. This prevents spoofing and impersonation attacks.

Organizations implementing comprehensive email security protocols experience 70% fewer successful email-based attacks compared to those with minimal protections. The investment pays for itself quickly when you consider the average cost of a single breach.

Taking Action: What You Can Do Today

Don’t wait for a security incident to force your hand. Here are immediate steps you can take:

Evaluate your current email provider honestly. If you’re using free services for business communications, you’re accepting significant privacy and security risks.

Implement multi-factor authentication on all email accounts immediately. This single step prevents most credential-based attacks.

Train your team to recognize phishing attempts and BEC tactics. 95% of security leaders expect to encounter email security problems this year: preparation matters.

Consider encrypted email services for sensitive communications. The cost is minimal compared to potential breach expenses.

Establish clear protocols for financial requests and vendor communications. Verify all wire transfer requests through separate communication channels.

The Bottom Line on Email Privacy and Security

In 2025, assuming your emails are private or secure without taking specific action is dangerous. The old trade of convenience for privacy is no longer acceptable when cyber threats evolve at unprecedented speed.

Privacy-focused email services with end-to-end encryption, combined with proper security awareness training and technical controls, aren’t luxuries: they’re business necessities. Whether you’re a solo entrepreneur or managing a team, your email security directly impacts your financial security.

The question isn’t whether you need to worry about email privacy and security. The question is whether you’re willing to take action before becoming another statistic. Start with one improvement today, then build from there. Your future self will thank you for taking email security seriously now rather than learning its importance the hard way.

For more security guidance and web development insights, visit us at The CharlesWorks Corner. Don’t risk potential losses when practical solutions exist.

FacebooktwitterredditpinterestlinkedinmailFacebooktwitterredditpinterestlinkedinmail
The CW Corner – AI-Powered Phishing Emails Are Getting Smarter: 5 Steps to Protect Your Business Inbox in 2025

The CW Corner – AI-Powered Phishing Emails Are Getting Smarter: 5 Steps to Protect Your Business Inbox in 2025

Your business inbox just became a battleground. AI-generated phishing has surged past ransomware as the number one email threat in 2025. We’re seeing a staggering 1,265% increase in phishing attacks powered by artificial intelligence since late 2024.

Gone are the days of obviously fake “Nigerian prince” emails riddled with spelling errors. Today’s attackers harvest your LinkedIn profile, study your GitHub commits, and analyze your communication patterns. They’re crafting emails so personalized and grammatically perfect that even tech-savvy professionals are falling for them.

Think about what’s connected to your email accounts: banking, vendor relationships, customer data, employee records. One successful phishing attack can devastate your business. But don’t panic. Here’s exactly how to armor your inbox against these evolving threats.

The New Reality of AI Phishing

Modern phishing attacks aren’t random spray-and-pray campaigns. Attackers use generative AI to create messages tailored specifically to you, your role, and your current projects. They might reference that new client you mentioned on social media or mimic your boss’s exact writing style.

These attacks cost as little as $50 to deploy but can result in devastating financial losses and data breaches. The traditional email filters you’ve relied on? They’re struggling to keep up with content that looks and sounds completely legitimate.

image_1

Step 1: Deploy AI-Powered Email Filtering Systems

Your current email security isn’t enough. Period. You need modern systems that use machine learning to spot AI-generated content patterns that human reviewers would miss.

These advanced filters analyze subtle characteristics that distinguish artificial text from human writing. They catch syntax anomalies, stylistic inconsistencies, and language patterns that traditional signature-based detection completely overlooks.

Legacy email filters operate like security guards checking IDs at the door. AI-powered systems work more like behavioral analysts, studying how people actually communicate and flagging anything that doesn’t match established patterns.

Don’t wait for your current provider to “upgrade” their system. The gap between old and new technology is too significant. Investigate dedicated AI email security solutions designed specifically for these threats.

Step 2: Implement Behavioral Analysis and Anomaly Detection

Here’s what makes AI phishing so dangerous: attackers can perfectly copy writing style but struggle to replicate authentic behavioral patterns. That’s your advantage.

Deploy monitoring that continuously learns how your colleagues, vendors, and partners actually communicate. When someone claiming to be your accounting manager suddenly uses different sentence structures or timing patterns, the system flags it immediately.

Consider this scenario: your “CFO” emails requesting an urgent wire transfer. Traditional filters see legitimate credentials and approved content. Behavioral analysis notices this person never sends financial requests via email and always calls first.

These systems excel at catching spear-phishing attacks targeting specific individuals. Even perfectly crafted AI emails fail when they don’t match the unique communication fingerprints of real relationships.

image_2

Step 3: Integrate Context-Based Defense Systems

Content analysis alone isn’t sufficient anymore. You need security that understands context: the relationship between sender and recipient, timing expectations, and communication norms.

Context-based defenses combine AI and machine learning to verify whether messages align with established patterns. They question unusual requests from familiar vendors, unexpected urgent directives from executives, and communication that breaks established protocols.

For example, if your regular vendor suddenly emails requesting updated payment information, context-based systems flag this as suspicious. They know this vendor typically handles payment changes through phone calls and account managers.

This approach adds verification layers that generic content analysis cannot provide. It’s particularly effective against sophisticated attacks that use accurate information but inappropriate communication channels.

Think of it as having a security assistant who knows everyone’s habits and immediately notices when something feels “off” about a message.

Step 4: Evaluate and Upgrade Your Email Security Stack

When did you last audit your email security infrastructure? If it’s been more than six months, you’re probably vulnerable to modern AI-driven attacks.

Start by testing whether your current tools can detect polymorphic malware, changing attachment hashes, and redirecting URLs: common obfuscation techniques in AI-powered campaigns. Many organizations discover significant gaps during these evaluations.

Don’t rely on point solutions. Integrated security platforms that combine multiple defense mechanisms create layered protection. Think of it like home security: you want door locks, window sensors, motion detectors, and cameras all working together.

Your existing email security might handle traditional threats but struggle with AI-generated content. Consider platforms where AI-enhanced email protection coordinates with endpoint security and network monitoring.

Budget between $5 and $40 per user monthly for comprehensive AI-powered solutions. This investment is substantially lower than the potential cost of successful attacks: data breaches, regulatory fines, and reputation damage.

Step 5: Create an Integrated Security Ecosystem

Email security cannot operate in isolation. Your AI-powered defenses must coordinate with endpoint protection, network monitoring, and incident response protocols.

This holistic approach prevents attackers from circumventing email security only to succeed through alternative vectors. If phishing emails slip through but attempt to download malware, endpoint protection catches them. If they redirect to malicious websites, network monitoring blocks access.

Establish regular security awareness training for employees. No automated defense achieves 100% accuracy: human judgment remains your critical final layer of protection. Train staff to recognize AI phishing indicators and verify suspicious requests through separate communication channels.

Create clear escalation procedures. When employees spot potential AI phishing, they need immediate reporting channels and rapid response protocols. Quick action can prevent attacks from spreading throughout your organization.

image_3

Supporting Your Defense Strategy

Remember that attackers continuously evolve their tactics through artificial intelligence. Your defenses must evolve too. Schedule quarterly security assessments and stay informed about emerging AI phishing techniques.

Don’t risk potential losses from increasingly sophisticated attacks. The combination of AI-powered filtering, behavioral analysis, context-based defense, comprehensive security evaluation, and integrated protection creates a formidable barrier against even the most advanced phishing campaigns.

Your inbox doesn’t have to be a liability. With proper AI-enhanced security measures, it becomes a protected gateway that supports your business operations without exposing you to unnecessary risks.

Hopefully these steps help you stay ahead of attackers who are getting smarter every day. The investment in proper email security pays dividends in protected data, preserved reputation, and peace of mind.

Stay vigilant, stay protected, and remember: when in doubt about any email, verify through alternative communication channels before taking action.

FacebooktwitterredditpinterestlinkedinmailFacebooktwitterredditpinterestlinkedinmail