by Charles Oropallo | Nov 19, 2026 | Passwords, Security, Small Business, The CW Corner
 Hardware security keys are small devices that give your important accounts a strong, physical check at sign-in. You plug one into a computer or tap it against a compatible phone. Think of it as a small key that helps prove you are really you.
For most accounts, the security key is a second step after your password. Some services also let you use a key to sign in without entering a password. Either way, it can make fake login pages much less effective.
What is a hardware security key?
A hardware security key is a small device that connects through a Universal Serial Bus (USB) port or communicates wirelessly with a phone. During sign-in, you may need to touch its button or tap it against your device.
The key works with your browser and the service’s sign-in system. It helps confirm that you are signing in to the real website, not a convincing imitation.
Some keys include a fingerprint reader. Others ask you to touch a button. Either style can work well. Choose a method that feels comfortable and suits the accounts and devices you use.
You may also see keys described as supporting Web Authentication (WebAuthn) and Fast Identity Online (FIDO) standards. Those standards let websites and security keys work together for secure sign-ins. Check that the services you rely on support them.
Why does a key stop many phishing attempts?
A password or code can be copied. If a fake website tricks you into entering a password or a temporary code, the attacker may use it on the real account before it expires.
A hardware security key works differently. During sign-in, the browser and key use the website’s identity to check that the request is for the right service. A key registered for your real email provider will not answer a lookalike site pretending to be that provider.
Picture a key cut for one particular lock. A copied key shape may look convincing, but it will not turn the real lock. A security key uses a similar idea, with digital information instead of metal teeth.
This protection is why keys can resist phishing better than codes you type into a webpage. It does not make every account or device invulnerable. Use the key only on websites you opened yourself, and protect your devices, passwords, and account recovery options.
For another passwordless sign-in option, see Passkeys Explained: Signing In Without a Password. To compare common second-step methods, read Authenticator Apps vs. Text Codes: Which Two-Factor Sign-In Is Safer?.
What should you look for when buying one?
Start by checking that the key supports WebAuthn and FIDO standards. Well-known brands make these devices, but focus on compatibility rather than choosing based on a logo.
Consider how you will connect the key. A model with both a computer connector and a phone-friendly option can be useful if you sign in from both. Check your computer and phone ports before buying.
Buy two keys: one for regular use and one as a spare. Store the spare somewhere safe and separate from your everyday key. A backup does not help much if both keys live on the same key ring.
Some keys have a button you touch during sign-in. Others include a fingerprint reader. Either can be a practical choice. Follow the maker’s setup instructions, and keep the key protected from damage or loss.
Which accounts should you secure first?
Start with accounts that could unlock or disrupt many other parts of your life or business:
- Your email account. Password-reset links for many services arrive in your inbox. That makes email a kind of master key.
- Your domain registrar. Someone with access may be able to change where your website address points.
- Your web hosting account. Access could allow changes to your website or its hosting settings.
- Your bank and payment accounts. Protect accounts that handle business funds or personal savings.
- Your password manager. It may hold the sign-in details for many of your other accounts.
A password manager can help you use a different password for every service. Learn more in Password Managers: One Key for a Whole Ring of Locks.
If your email account is compromised, the damage can spread quickly through password resets. Our email account recovery walkthrough explains why that inbox deserves special attention.
How do you set up a key?
The exact wording varies between services, but the process is usually straightforward:
- Open the service’s official website or app yourself. Avoid starting from an unexpected email link.
- Sign in and open the account’s security or sign-in settings.
- Choose the option to add a security key, then follow the instructions.
- Give the key a name you will recognize, such as “Office key” or “Backup key.”
- While you are still signed in, add your spare key in the same session.
- Test that both keys work before closing the settings page.
Adding the spare right away matters. You may not remember to do it later, and recovering an account can be much harder if your only key disappears.
If the service offers recovery codes, print them and store them somewhere secure, away from your keys. Treat those codes like spare keys to the account. Do not leave them beside your computer or save them in an inbox that the account itself can unlock.
Can your phone act as a security key?
Modern phones can take part in secure sign-ins. Some can approve a login on another device, while many also store passkeys for accounts that support them.
Passkeys are related to security keys, but they are not exactly the same thing. A passkey is a digital sign-in credential stored on a phone, computer, or supported account service. A physical security key is a separate device you carry and connect when needed.
A phone that receives a text message is not the same protection as a physical security key. Text codes can be intercepted or stolen through phone-number scams. Learn about that risk in our article on SIM swap scams.
What are the trade-offs?
You need to have the key with you when signing in, unless you use another supported method. Some services limit how many keys you can register. Others do not support security keys at all.
Losing every registered key can lock you out. That is why you should set up a spare and save recovery codes before trouble starts. Check each service’s recovery process while you still have access.
A key also cannot protect an account if someone has already gained access another way, such as through an open sign-in session. Keep devices updated, watch for unexpected account alerts, and remove keys you no longer use.
A small-business security step worth planning
If employees or contractors can change your website, pay bills, or access customer information, consider issuing keys to those people. Keep a simple record of who holds each key and which accounts it protects.
When someone leaves, remove their key from the relevant accounts the same day. Treat it like a building key: record who has it, and collect or disable access when their work ends.
For a handful of accounts that could ruin your week if they were taken over, hardware security keys are worth considering. Start with your email, domain, hosting, banking, and password manager accounts. Add a spare, save recovery codes, and ask for help if setup gets confusing.


by Charles Oropallo | Nov 11, 2026 | Do-It-Yourself, Internet, Passwords, Security, Small Business, The CW Corner
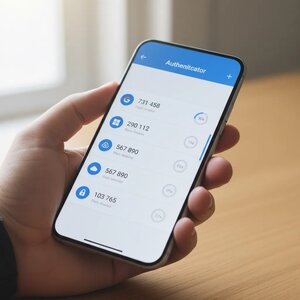
Authenticator apps vs. text codes is a practical security choice for your email, business website, and other important accounts. Both add a step beyond your password, but they protect that step differently. For most people, an authenticator app is safer than a code sent by text.
What is two-factor authentication?
Two-factor authentication (2FA) asks you to prove your identity in two different ways. Usually, you enter something you know, such as your password, and confirm something you have, such as your phone.
That extra check can help if someone steals or guesses your password. They may still need access to your phone or authenticator app before they can sign in.
Two-factor authentication is not a guarantee against every threat. It does make password-only access harder, which is a worthwhile improvement for important accounts.
How do text message codes work?
With short message service (SMS) verification, the website sends a temporary code to your phone number. You enter that code after your password to finish signing in.
It is familiar and usually easy to set up. But SMS depends on your phone number and mobile carrier, which creates some weaknesses.
- SIM swap scams: A scammer may trick your carrier into moving your number to a phone they control. This is called a subscriber identity module (SIM) swap. If successful, they may receive your login texts.
- Lost or unavailable phone: You may be unable to receive codes if your phone is lost, its battery is dead, or you have no service.
- Delayed or missing messages: Texts do not always arrive promptly. That can leave you waiting when you need access.
- Visible or accessible messages: A code might appear in a lock-screen notification. Depending on your settings and apps, messages may also be accessible in other places.
SMS codes are still better than using only a password in many situations. But they rely on a phone network and number that can be targeted or temporarily unavailable. The Cybersecurity and Infrastructure Security Agency (CISA) advises using text-based codes only as a last resort when stronger options are unavailable. See its multifactor authentication guidance.
How does an authenticator app work?
An authenticator app creates a temporary code on your phone or computer. During setup, the account and app share a secret, usually transferred by scanning a quick response (QR) code. The app uses that secret and the current time to create a six-digit code.
The code is generated locally, inside the app. Your phone does not need mobile service or an internet connection to display it. So, the code can still appear in airplane mode or where reception is poor.
You will generally need internet access to reach the website and complete sign-in. “Works offline” means the app can generate the code without a network connection. It does not mean you can sign in to an online service without internet access.
Unlike an SMS code, the authenticator code does not travel through your carrier’s text messaging system. A SIM swap alone does not give a scammer the secret stored in your authenticator app.
Which option is safer?
When you can choose between SMS and an authenticator app, an authenticator app is generally safer. Its code is not tied to your phone number, so a SIM swap will not automatically send your codes to someone else.
That does not make authenticator apps invulnerable. Someone who steals your password and tricks you into entering a current code on a fake sign-in page may still get access. Protect your device, check the website address, and do not share codes with anyone who contacts you unexpectedly.
Some accounts offer stronger sign-in methods, including passkeys. Passkeys can provide better protection against fake login pages. We explain how they work in Passkeys Explained: Signing In Without a Password.
How to set up an authenticator app
The steps vary a little by website, but the process is usually straightforward:
- Open the real website or app yourself. Avoid setup links in unexpected emails or text messages.
- Go to its security or sign-in settings. Look for an authenticator app, verification app, or two-step sign-in option.
- Choose the app option. The service should show a QR code and explain what to do next.
- Open your authenticator app and scan the code. Follow the service’s instructions, then enter the app’s current code to confirm setup.
- Save the recovery codes. Store them somewhere safe, such as a printed sheet in a secure place or a password manager you can access independently.
- Test your new sign-in. Sign out and sign in again while your existing method still works.
Do not photograph a recovery code casually or leave it beside your computer. Treat it like a spare key: anyone who gets it may be able to access your account.
Keep the old method available until you have tested the app and confirmed your recovery options. Then review the account’s settings. Some services keep SMS enabled as a fallback, even after you add an authenticator app.
What if you get a new phone?
Plan the move before you retire your old phone. Many authenticator apps have a way to transfer accounts, but the process varies by app.
Follow the app’s official transfer instructions while you can still use the old device. Add the authenticator to your new phone, test sign-in, and make sure your recovery codes are available. Only then remove the old device or erase it.
If your old phone is already gone, use the service’s recovery process. This is exactly why saving recovery codes during setup matters.
Keep the rest of your account secure
An authenticator app is software running on a device. The device could be lost, stolen, or compromised. Keep its operating system updated, use a secure screen lock, and review which notifications appear on your lock screen.
Your email recovery account matters, too. If someone can take over your email, they may be able to reset passwords elsewhere. Protect that inbox with a strong, unique password and two-factor sign-in. A password manager can help you keep unique passwords without memorizing every one.
A simple way to get started
You do not have to update every account today. Turn on two-factor authentication with whichever method a site offers first. Any extra sign-in check is generally better than relying on a password alone.
When you are ready, move your most important accounts to an authenticator app. Start with email, then consider banking, domain registration, website administration, and other accounts that could affect your business. Keep recovery details safe, and test each change before removing an older sign-in method.
For more on safer sign-ins, read Passkeys Explained: Signing In Without a Password and Password Managers: One Key for a Whole Ring of Locks.
by Charles Oropallo | Nov 9, 2026 | Do-It-Yourself, Passwords, Security, Small Business, The CW Corner
Password managers can make safer online habits much easier. Instead of trying to remember every login, you remember one strong master passphrase. The manager creates and stores different passwords for your other accounts. That can help protect your email, banking, business website, and everyday online services.
The trouble with reused passwords
Remembering passwords can feel like a chore. It is tempting to use one familiar password everywhere, then add a number when a website asks for a change. Unfortunately, that convenience can create a chain reaction.
If one website is breached, criminals may try the exposed password on other sites. They often test email, banking, shopping, and social accounts. If the same password works in several places, one stolen login may put many accounts at risk.
Weak passwords have a similar problem. A pet’s name, a favorite team, or a simple keyboard pattern may be easy to guess. Personal details can also be available through public profiles or other online sources.
The real challenge is not that you have many accounts. It is making sure one account’s password cannot unlock the rest. Unique passwords help break that chain.
What a password manager actually does
Think of a password manager as a locked digital key ring. It stores your logins in a protected vault and helps you use the right one when you visit a website or app.
Most managers can also generate passwords for you. These can be long, random, and different for each account. You do not need to memorize a jumble of letters and symbols. The manager remembers it for you.
You unlock the vault with a master password or passphrase. That is the one you need to know by heart. Depending on the product, the manager may also fill in login details through a browser extension or mobile app.
Some products synchronize your vault across devices. That means you can access it on your computer and phone, rather than relying on a single device. Check how a manager stores and synchronizes your information before choosing one.
How to choose a manager
Choose carefully, because the vault protects access to many accounts. There is no need to pick the first app you see in an advertisement. Look for a product with a trustworthy track record and clear information about its security and recovery options.
Consider these features:
- A reputation you can check. Read independent reviews and look for clear, current information about security practices.
- Cross-device access. Confirm it works on the computers and phones you actually use.
- Browser integration. A browser extension can make logins easier. Make sure it comes from the manager’s official website or app store.
- Synchronization details. Understand how your vault stays available across devices and what happens if you lose access.
- Recovery options. Learn whether the provider can help restore access, and what information that process requires.
A browser extension can also help you notice when a login page is unfamiliar. Still, pause before entering details, especially when you arrived through an unexpected email link. A password manager cannot make every phishing page safe.
The U.S. Cybersecurity and Infrastructure Security Agency recommends password managers as a way to create and manage unique passwords. You can read its guidance on strong passwords.
Make the master passphrase memorable and private
Your master passphrase protects the vault, so it deserves special attention. Make it long and difficult for someone else to guess. A few unrelated words can be easier to remember than a short, complicated string.
Do not reuse a password from another account. Do not use a familiar quotation or personal detail that someone could guess. And do not share the passphrase in email, messages, or with people who do not need access.
You might be tempted to write it on a sticky note. We understand the temptation, but a note beside your computer is not a great security plan. If you need a backup, follow the manager’s guidance and keep recovery information somewhere protected and separate from your everyday devices.
Turn on two-factor authentication, too
A strong master passphrase is important, but it should not be your only safeguard. Turn on two-factor authentication for the password manager if it is available. This requires another proof of identity, such as an approval from an authenticator app or security key.
Use two-factor authentication on your important email, banking, domain, and website accounts as well. Your email account deserves special attention because it may receive password-reset links for other services.
This extra step can help protect an account if someone learns your password. It is not a reason to relax about suspicious links or unexpected login requests. Verify those independently.
Switch over gradually
You do not need to update every account in one sitting. Begin with accounts that could unlock other accounts or cause serious problems if someone accessed them.
A practical order might be:
- Secure your email. Set a unique password and enable two-factor authentication.
- Update banking and payment accounts. Give each one its own generated password.
- Protect your business website and hosting logins. Include your domain registrar and other services that control your online presence.
- Work through the rest of your accounts. Update them when you sign in or have a few quiet minutes.
For each account, open the real website or app yourself. Sign in, change the old password, and save the new one in your manager. Avoid following password-change links from unexpected messages.
Some accounts may have unusual password rules. If a generated password is rejected, adjust the manager’s settings and try again. Do not solve the problem by reusing an old password everywhere.
As you move accounts, check for duplicate or outdated entries in the vault. Remove entries only when you are sure you no longer need them. A slow, orderly switch is much better than a rushed afternoon of login confusion.
What if you forget the master passphrase?
This is the part to understand before you begin. Depending on the manager’s design and your recovery settings, forgetting the master passphrase could mean losing access to the vault. Some providers may be unable to reset it or restore the information inside.
Read the provider’s recovery instructions while you still have access. If it offers recovery codes or another recovery method, learn how that works. Store any recovery information in a protected location, separate from the vault and the devices it protects.
Do not assume that support can recover everything. Strong protection can mean the provider cannot read your saved passwords. That privacy benefit may also limit what support can do if you lose the master passphrase.
Consider how you would recover access before filling the vault. Set up available recovery options, keep your devices updated, and make sure your recovery email account is secure. A little planning now can prevent a very frustrating surprise later.
Safer than sticky notes or password reuse
No tool removes every risk. A password manager still needs a strong master passphrase, secure devices, and sensible recovery planning. It is also wise to install updates and pay attention to account security alerts.
Even so, using a manager is generally safer than repeating one password across important accounts. It is also safer than leaving login details on a note beside your screen. The manager helps you use unique passwords without expecting you to memorize them all.
For a small-business owner, this can make website, email, and payment access easier to manage responsibly. For everyday users, it means fewer reused passwords and less guesswork at sign-in. Start with your most important accounts, then keep going at a comfortable pace.
For more practical security advice, see our posts on passwords and best practices for mitigating website hacks. You may also find our article about phishing attacks helpful. Hopefully this tip makes your online key ring easier to manage, and a lot less likely to be a sticky note.
by Charles Oropallo | Oct 24, 2026 | Do-It-Yourself, Passwords, Security, Small Business, Technical Help, The CW Corner, Web Hosting
 If you’ve wondered what is an SSL certificate, it’s a digital file that helps your browser confirm a website’s identity and protect information sent between the site and its visitors. It’s behind the familiar padlock and the
https:// at the start of a web address.
The name sounds technical, but the basic idea is straightforward. An SSL certificate helps create a private, trustworthy connection between a website and the person visiting it. Let’s look at what it does, what it doesn’t do, and what your business needs to check.
What does “SSL certificate” mean?
SSL stands for Secure Sockets Layer. It’s the older name for a technology that protected connections between websites and browsers.
Today, websites use TLS (Transport Layer Security), the newer technology that replaced SSL. People still commonly say “SSL certificate,” even when they mean a TLS certificate. The familiar name has stuck around.
An SSL certificate is installed on a website’s server. It connects the website’s domain name with a digital identity that browsers can check. When the connection is properly set up, information traveling between the visitor and website is encrypted.
Encryption scrambles information so it’s harder for other people to read while it travels across the internet. Think of it like placing a letter inside a sealed envelope rather than sending it on a postcard.
What do the padlock and HTTPS tell you?
HTTPS stands for Hypertext Transfer Protocol Secure. It means the usual web connection, HTTP (Hypertext Transfer Protocol), is protected using TLS.
When someone visits a website using HTTPS, the browser checks the certificate and helps establish an encrypted connection. If the checks succeed, the browser usually shows a padlock or another secure-connection indicator. The appearance varies by browser.
That padlock is useful, but don’t treat it as a full business endorsement. It does not prove that a company is honest, that a website has no malware, or that every service on the site is safe.
Scammers can also use HTTPS. The certificate indicates that the connection is encrypted and the certificate matches the website address. It does not guarantee that the website itself deserves your trust.
What happens when someone visits your site?
Here’s a simplified look at the process:
- A visitor opens your website using an HTTPS address.
- The website server sends its certificate to the visitor’s browser.
- The browser checks the certificate’s domain, validity dates, and trusted issuer.
- If the checks pass, the browser and server establish an encrypted connection.
- Information sent over that connection is protected while it travels.
The certificate is a bit like an identification card for your website. The browser checks whether it appears valid and belongs to the address the visitor requested.
A trusted certificate is generally issued by a certificate authority (CA). A CA is an organization trusted to check domain control and digitally sign certificates. Browsers recognize certain trusted issuers and use them to help verify certificates.
For a closer look at the process, see Cloudflare’s plain-language explanation of how SSL works.
Why does your small business need one?
An encrypted connection is important for more than online stores. Your website may have a contact form, appointment request, login page, newsletter signup, or other features where visitors enter information.
Without HTTPS, a browser may warn visitors that the connection is not secure. That can make people hesitate before contacting you. It can also create problems for site features that expect a secure connection.
For example, a local clinic might have an online appointment request form. A contractor might collect customer details through a quote form. HTTPS helps protect information as it travels between those visitors and the website.
Search engines also use HTTPS as a ranking signal, though an SSL certificate alone does not guarantee better search placement. It’s one part of maintaining a trustworthy, well-managed website.
What an SSL certificate does not do
It helps to understand the limits. A certificate protects the connection between a visitor’s browser and your website. It does not secure every part of your business or website by itself.
An SSL certificate does not:
- Prevent someone from sending a phishing email that links to your website.
- Fix weak passwords, outdated software, or vulnerable plugins.
- Guarantee that your website is free from harmful code.
- Replace backups, security updates, or good account practices.
- Ensure that information remains private after it reaches the website.
Think of it like a locked delivery van. It helps protect the trip, but it cannot guarantee what happens before loading or after delivery. Website security needs several safeguards working together.
For practical website security steps, read our guide to security tips for business owners.
Do you need an expensive certificate?
Many small-business websites can use a basic domain-validated (DV) certificate. This means the certificate issuer confirms that the requester controls the domain.
Other certificate types may involve additional checks about an organization. Those checks may suit particular business or compliance needs, but they do not automatically make the connection more strongly encrypted.
Before paying extra, ask what the certificate includes and why your website needs it. For a typical business website, the more important questions are whether the certificate is trusted, correctly installed, covers the right domain names, and renews reliably.
Some hosting providers include SSL certificates as part of their hosting service. Others help configure certificates from providers such as Let’s Encrypt. Ask your host what is included before buying another certificate.
Check that your certificate is working
You can do a few simple checks without reading technical server logs:
- Visit your website using
https://. Check both the main address and any commonly used version, such as the www address.
- Look for a browser warning. If you see one, don’t dismiss it. Contact your web host or developer and ask them to investigate.
- Check important pages and forms. Try your contact form, booking tools, and other features visitors rely on.
- Ask about renewal. Confirm that certificate renewal is monitored and handled before the certificate expires.
- Check for mixed content. This happens when a secure page tries to load some items, such as images or scripts, through an unsecure connection.
A site can have a valid certificate and still show a warning if it loads some page elements insecurely. Your developer or hosting provider can help locate and correct those items.
If a certificate expires or is installed incorrectly, visitors may see a warning instead of your website. Renewals can often be automated, but automation still needs monitoring. Ask who receives renewal alerts and who checks that the process succeeds.
A quick note for WordPress owners
If your WordPress website has an SSL certificate, the website address in WordPress should usually use HTTPS too. The site may also need a redirect that sends visitors from the old HTTP address to the secure one.
Changing those settings without checking first can sometimes create redirect loops or leave images and scripts loading incorrectly. If you’re unsure, ask your developer or hosting provider to review the setup before making changes.
Good hosting support should be able to confirm whether your certificate is active, which domain names it covers, and whether renewal is set up. At The CharlesWorks Corner, we help businesses with website development, hosting, SSL certificates, and ongoing website support.
Keep the little padlock in perspective
So, what is an SSL certificate? It’s an important part of securing the connection between your website and its visitors. It helps browsers confirm a website’s identity and encrypts information while it travels.
Make sure your website uses HTTPS across its pages, its certificate covers the addresses customers visit, and renewal is being monitored. Then pair that protection with updates, secure passwords, and reliable backups.
The padlock is a helpful sign, not a complete security plan. If you’re unsure whether your certificate is set up correctly, ask your web host or developer to check.
by Charles Oropallo | Jun 30, 2022 | Do-It-Yourself, Email, Internet, Passwords, Security, The CW Corner, Website Updates, WordPress
We at CharlesWorks are often asked by our web clients if their site is protected from malware and getting hacked. They also want to know if there site IS hacked, whether there be a charge to fix it.
The totally hack-proof website
The totally hack proof website has no access to it. So it’s not connected to the Internet. No one can view it. Such a website doesn’t sound like its of much use if no one can see it.
So, let’s agree that it is unrealistic to believe that a publicly accessible website can be totally hack-proof. Any website that is accessible via the public Internet is consistently subjected to attempts to break into it. Believe it or not, that’s the norm as opposed to the anomaly.
That being said, however, there ARE things you can do to mitigate website hacks. I have to stress the word mitigate here. Mitigation is defined as the action of reducing the severity, seriousness, or painfulness of something.
Site hacks are based on odds
My goal here is to simply remind you of what you most likely already know: that we can reduce the probability – the odds – of your site being hacked. We at CharlesWorks want that probability to be so low that it hopefully it doesn’t ever happen to you.
The major hacking causes
I have been operating CharlesWorks since 1998. In my experience, there appear to be two major reasons why sites get hacked:
-
- The access credentials/passwords have been compromised.
- The software that operates them wasn’t kept up to date.
Lets take a look at each of these below.
Compromised Access Credentials
Compromised passwords and bad actors gaining access to website login credentials is the major reason we see sites hacked. Think about this in terms of your car. You could have alarms on it. But if you make a copy of your car key and give it to someone, they can do whatever they like with the car. Whether its a drive along the beach or to rob a bank, your car is theirs to use with the key you gave them. Credentials – log in and passwords – work pretty much the same way.
CharlesWorks has many clients who want to be able to do things themselves. We are strong proponents of doing it yourself when it’s feasible and convenient. This is especially true for adding posts or page materials. It also makes sense when making other changes or modifications to your site. It is, after all, YOUR website.
However, many people fall prey to phishing schemes. Directly or indirectly, they usually end up tricked into giving out their website access credentials (as well as credentials to everything else they own). This is especially true if your email account is hacked and the hackers are able to access emails containing your website’s (and other) login credentials.
This problem is exacerbated if you have shared your website’s administrative or other access with others. Think of your emails containing various authorizations or login information as a potential weak link in a chain. If you have shared that information with others you have now created more weak links. This increases the odds of a potential compromise.
One of the best ways to mitigate these situations is to change your site’s access passwords so they are different than those possibly stored in your emails. And, to hope that anyone you may have shared your website access with has done the same.
Obviously, should site access be gained in such a manner, it would be your burden to have the site restored. I’ll expound upon this a little more at the end of this article.
Out of Date Security/Software Updates
Malware and virus protection on home computers operates a little differently than the same types of protection on servers. Website servers operate in the publicly accessible Internet. This results in many more entry points for potential issues. There are a number of very standard server protections available (which we utilize here at CharlesWorks).
After bad actors getting (or guessing) your passwords, the next major reason sites get hacked surrounds unapplied security updates and other software update issues. At CharlesWorks we mitigate such issues by running anti-malware software on our servers. Also, WordPress sites hosted on our servers are kept up to date automatically via automatic updating of the WordPress core as well as automatic updating of the the website’s plugins and themes.
There are literally thousands of individual pieces of software that must work in unison to operate most websites. These are developed by many more thousands of developers around the world. Unfortunately, no company can guarantee that a website will never get hacked. They can only mitigate security compromises and hope against the worst.
Restoring your Website
Regardless of which of the two situations above may have led to your website’s issues, your website will most likely need to be restored. That’s because after a bad actor or a hack back doors into the site will most likely have been installed for the bad actors to gain access again.
Many Internet companies claim to have automatic backups. In most of those, those backups are accessible to the user in their account. If the account is hacked, how safe do you suppose that is?
Some Internet companies delete and account upon a website being hacked. In those cases I have seen many left with no website or backup as a result.
What I believe is most important regarding this topic is the manner in which our WordPress sites are backed up every day for 30 days. Our backups are made to separate servers – external to those your the site operates on. For security reasons, the site administrators do not have access to these backups. So even with a site administrator’s compromised passwords there is no access to the backups. With these backups we can usually restore an average site in about 10-30 minutes if it needs restoring. And we can go back as far back as 30 days. We would only bill our web client for the 10-30 minutes (again – for an average website) which results in only a minor charge to restore it. Note that some websites are extremely large and require much more time to restore but these are very rare).
In my experience running CharlesWorks since 1998, we’ve built and handled more than 5,000 websites. At this point in time, I do not recall the last time a website we built and totally maintained was hacked (unfortunately I recall several instances of sites maintained by others that failed to ensure the site was updated and/or had their passwords compromised).
Sites getting hacked for out of date software happens far less frequently (if at all) when security updates are kept up to date and bad actors are kept out.
I hope this helps you understand a little more about this topic.
by Charles Oropallo | Feb 5, 2020 | Do-It-Yourself, Email, Internet, Monadnock Shopper News, Passwords, Security, Shopper News, The CW Corner, Website Development
I’ve written several articles about specific scams that are occurring on a regular basis on the Internet. They seem to subside for a short time – a very short time – and then a wave of them happens again.
One of the worst – as far as I am concerned – are the ones where the email recipient is being told they must verify their email. These have some common traits with most Internet scams:
1) A sense of urgency – they want you to take care of this immediately
2) A time limit – they give you within 24 hours to act
3) A threat – they tell you your email will be locked.
The first thing you have to understand is that nearly everyone gets these on occasion. I have received them myself in which they are made to look like they are from CharlesWorks. So when our clients get these they tend to become very worried very quickly.
I can’t stress enough that most legitimate companies will not send out messages like these. To fall prey to these can be a real nightmare. With access to one’s email these days the bad guys can wreak havoc in one’s life. The worst cases are called identity theft!
Don’t be the unfortunate one who falls prey to these scammers. If you have been “notified” of something serious – call your provider up and speak with a representative. Just like at my company – it’s a lot easier for us to allay your fears than to have to try to clean up the mess that can happen with compromised accounts.





 European Union General Data Protection Regulation Compliant