by Charles Oropallo | Nov 12, 2026 | Do-It-Yourself, Internet, Security, Small Business, The CW Corner
 Public Wi-Fi safety matters whenever you connect at a coffee shop, airport, hotel, or other shared place. These networks are convenient, but you do not control who set them up or who else is connected. That calls for sensible caution, not panic.
The familiar warning that everyone nearby can automatically read everything you do is too broad. Modern websites and apps often encrypt their connections. Still, the network itself can create risks, and a convincing fake hotspot can fool you into connecting.
Here’s what to watch for, and how to make safer choices without giving up your coffee-shop table.
What can someone on public Wi-Fi see?
When you use an open or poorly secured network, other people may be able to observe some network activity. The risk is greater when a website or service sends information without encryption.
HTTPS (Hypertext Transfer Protocol Secure) encrypts the connection between your browser and the website you visit. That helps keep the contents of your connection private while they travel across the network. It is common on websites and in apps today.
But encryption is not a reason to stop paying attention. A network operator may still see some connection details, such as which online services your device contacts. And HTTPS cannot protect information you type into a fake website or sign-in page.
For a quick reminder about secure website connections, see our earlier article on SSL (Secure Sockets Layer). We’ll keep the details simple here: check the address and connection, and don’t ignore browser warnings.
Watch for fake look-alike hotspots
One realistic risk is a fake hotspot designed to look like the venue’s real network. It may use a similar name, a slightly different spelling, or a name suggesting “free Wi-Fi.” A stronger signal does not prove that a network is genuine.
Imagine sitting in an airport and seeing two networks with nearly identical names. You might choose the first one, connect, and see a sign-in page that looks familiar. If the network is controlled by someone else, that page could be designed to collect information.
Before connecting, ask staff for the exact network name and any instructions. Use the venue’s official signage as a helpful reference, but verify if anything looks unusual. Be wary of unexpected requests for passwords, payment details, or extra downloads just to get online.
A lock symbol beside a network name does not confirm that the network belongs to the business. It only indicates that a password or other protection is involved. Confirm the name with staff instead of guessing.
The Cybersecurity and Infrastructure Security Agency (CISA) describes fake “evil twin” hotspots and advises confirming a public network’s name before using it. Read its wireless network safety guidance.
Use a personal hotspot for sensitive tasks
When practical, use your phone’s cellular connection or personal hotspot for sensitive work. That can be a better choice for banking, payment tasks, business administration, account recovery, or handling private client information.
A personal hotspot uses your phone’s mobile data connection to provide internet access to your other device. It avoids the coffee shop’s shared Wi-Fi network, although it does not replace other good security habits. Use a strong hotspot password, and switch the hotspot off when you are finished.
If cellular service is weak or unavailable, pause and consider whether the task can wait. Reading a news story is different from changing the password for your business email. A little patience can be a worthwhile security measure.
Check the website before signing in
If you do use public Wi-Fi, check that important websites use HTTPS and that the web address is the one you intended to visit. A lock icon can indicate an encrypted connection, but it does not prove the website itself is genuine.
Look closely at the address before entering a password or payment information. A fake page can use a name that resembles a real business. If your browser shows a certificate or security warning, stop. Don’t click through just to make the warning go away.
When possible, avoid signing in to sensitive accounts on a shared network. If you must access one, use the official app or type the website address yourself. Do not rely on a link from an unexpected message or a pop-up from the Wi-Fi network.
Public Wi-Fi may also ask you to accept terms on a sign-in page, often called a captive portal. A basic access page can be normal. But be cautious if it asks for your email password, banking credentials, a one-time sign-in code, or an unexpected software installation. When in doubt, disconnect and ask venue staff.
For more help with spotting fraudulent messages and links, see our existing article about phishing. The key point here is simple: don’t hand over account details just because a page appeared after you connected.
Turn off automatic connections and file sharing
Your device may automatically join networks it has used before. That can be handy at home, but it can also lead your device to connect without you noticing.
Turn off automatic joining for public networks, or remove networks you no longer need. Then choose a network manually when you arrive. If a familiar network name appears in an unfamiliar place, verify it before connecting.
Also turn off file sharing and network discovery when using public Wi-Fi. These settings can make your computer visible to other devices nearby. CISA recommends disabling file sharing on public networks. You can enable it again when you return to a trusted network, if you need it.
Keep your phone, computer, browser, and apps updated. Updates fix known problems and help protect the device you carry between home, work, and public spaces. A screen lock also matters if someone can physically reach your device.
What does a VPN do?
A VPN (virtual private network) creates an encrypted connection between your device and a VPN service. Think of it as a protected tunnel through the shared network. It can make it harder for other people on that Wi-Fi network to observe your traffic.
A reputable VPN can be useful when you regularly use public Wi-Fi, especially for work. But it is not an invisibility cloak. The VPN service becomes part of your connection, and you still need HTTPS for the connection between the VPN service and the website.
A VPN also cannot make a fake sign-in page trustworthy. It will not protect you if you enter your password into a look-alike website or install a harmful app. Choose a VPN carefully, keep its app updated, and treat requests to install certificates or unfamiliar software as a reason to pause.
If you connect to public Wi-Fi often for business, ask your IT provider or support contact whether a VPN is appropriate for your work.
Keep your sign-in habits strong
Public Wi-Fi safety works best alongside the account protections you use everywhere else. Two-factor authentication (2FA) adds another sign-in check beyond your password. It can help if someone learns that password, though it cannot make a fake login page safe.
We recently covered authenticator apps and text codes. That article explains how those sign-in options differ. Use the protections available on your important accounts, especially email and business services.
A practical routine before you connect
Before joining a coffee-shop, airport, or hotel network, take a moment to:
- Ask staff to confirm the exact network name.
- Turn off automatic joining and file sharing.
- Use your phone’s hotspot for sensitive tasks when practical.
- Check the web address and HTTPS before signing in.
- Stop if you see a browser warning or an unusual portal request.
- Use a reputable VPN when appropriate, while continuing to check websites.
Public Wi-Fi is not automatically dangerous, and you do not need to treat every café like a spy movie. Just remember that a shared network is outside your control. Verify the hotspot, protect your device, and save sensitive work for a safer connection when you can.


by Charles Oropallo | Nov 11, 2026 | Do-It-Yourself, Internet, Passwords, Security, Small Business, The CW Corner
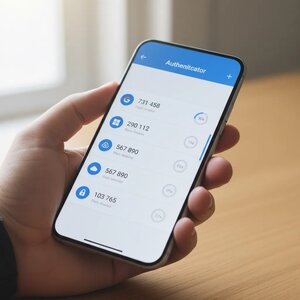
Authenticator apps vs. text codes is a practical security choice for your email, business website, and other important accounts. Both add a step beyond your password, but they protect that step differently. For most people, an authenticator app is safer than a code sent by text.
What is two-factor authentication?
Two-factor authentication (2FA) asks you to prove your identity in two different ways. Usually, you enter something you know, such as your password, and confirm something you have, such as your phone.
That extra check can help if someone steals or guesses your password. They may still need access to your phone or authenticator app before they can sign in.
Two-factor authentication is not a guarantee against every threat. It does make password-only access harder, which is a worthwhile improvement for important accounts.
How do text message codes work?
With short message service (SMS) verification, the website sends a temporary code to your phone number. You enter that code after your password to finish signing in.
It is familiar and usually easy to set up. But SMS depends on your phone number and mobile carrier, which creates some weaknesses.
- SIM swap scams: A scammer may trick your carrier into moving your number to a phone they control. This is called a subscriber identity module (SIM) swap. If successful, they may receive your login texts.
- Lost or unavailable phone: You may be unable to receive codes if your phone is lost, its battery is dead, or you have no service.
- Delayed or missing messages: Texts do not always arrive promptly. That can leave you waiting when you need access.
- Visible or accessible messages: A code might appear in a lock-screen notification. Depending on your settings and apps, messages may also be accessible in other places.
SMS codes are still better than using only a password in many situations. But they rely on a phone network and number that can be targeted or temporarily unavailable. The Cybersecurity and Infrastructure Security Agency (CISA) advises using text-based codes only as a last resort when stronger options are unavailable. See its multifactor authentication guidance.
How does an authenticator app work?
An authenticator app creates a temporary code on your phone or computer. During setup, the account and app share a secret, usually transferred by scanning a quick response (QR) code. The app uses that secret and the current time to create a six-digit code.
The code is generated locally, inside the app. Your phone does not need mobile service or an internet connection to display it. So, the code can still appear in airplane mode or where reception is poor.
You will generally need internet access to reach the website and complete sign-in. “Works offline” means the app can generate the code without a network connection. It does not mean you can sign in to an online service without internet access.
Unlike an SMS code, the authenticator code does not travel through your carrier’s text messaging system. A SIM swap alone does not give a scammer the secret stored in your authenticator app.
Which option is safer?
When you can choose between SMS and an authenticator app, an authenticator app is generally safer. Its code is not tied to your phone number, so a SIM swap will not automatically send your codes to someone else.
That does not make authenticator apps invulnerable. Someone who steals your password and tricks you into entering a current code on a fake sign-in page may still get access. Protect your device, check the website address, and do not share codes with anyone who contacts you unexpectedly.
Some accounts offer stronger sign-in methods, including passkeys. Passkeys can provide better protection against fake login pages. We explain how they work in Passkeys Explained: Signing In Without a Password.
How to set up an authenticator app
The steps vary a little by website, but the process is usually straightforward:
- Open the real website or app yourself. Avoid setup links in unexpected emails or text messages.
- Go to its security or sign-in settings. Look for an authenticator app, verification app, or two-step sign-in option.
- Choose the app option. The service should show a QR code and explain what to do next.
- Open your authenticator app and scan the code. Follow the service’s instructions, then enter the app’s current code to confirm setup.
- Save the recovery codes. Store them somewhere safe, such as a printed sheet in a secure place or a password manager you can access independently.
- Test your new sign-in. Sign out and sign in again while your existing method still works.
Do not photograph a recovery code casually or leave it beside your computer. Treat it like a spare key: anyone who gets it may be able to access your account.
Keep the old method available until you have tested the app and confirmed your recovery options. Then review the account’s settings. Some services keep SMS enabled as a fallback, even after you add an authenticator app.
What if you get a new phone?
Plan the move before you retire your old phone. Many authenticator apps have a way to transfer accounts, but the process varies by app.
Follow the app’s official transfer instructions while you can still use the old device. Add the authenticator to your new phone, test sign-in, and make sure your recovery codes are available. Only then remove the old device or erase it.
If your old phone is already gone, use the service’s recovery process. This is exactly why saving recovery codes during setup matters.
Keep the rest of your account secure
An authenticator app is software running on a device. The device could be lost, stolen, or compromised. Keep its operating system updated, use a secure screen lock, and review which notifications appear on your lock screen.
Your email recovery account matters, too. If someone can take over your email, they may be able to reset passwords elsewhere. Protect that inbox with a strong, unique password and two-factor sign-in. A password manager can help you keep unique passwords without memorizing every one.
A simple way to get started
You do not have to update every account today. Turn on two-factor authentication with whichever method a site offers first. Any extra sign-in check is generally better than relying on a password alone.
When you are ready, move your most important accounts to an authenticator app. Start with email, then consider banking, domain registration, website administration, and other accounts that could affect your business. Keep recovery details safe, and test each change before removing an older sign-in method.
For more on safer sign-ins, read Passkeys Explained: Signing In Without a Password and Password Managers: One Key for a Whole Ring of Locks.
by Charles Oropallo | Nov 10, 2026 | Do-It-Yourself, Internet, Security, Small Business, The CW Corner
 Yesterday, we explained how password managers help you avoid reused passwords and protect your accounts. Today, let’s look at passkeys, another way to make signing in simpler and safer.
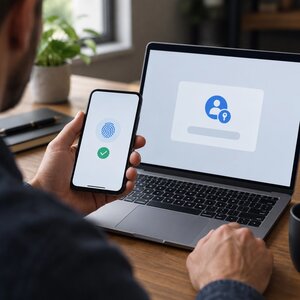
A passkey lets you sign in without typing a password. You approve the login using your fingerprint, face, or device personal identification number (PIN). For many small-business owners, that can mean fewer passwords to remember and less risk from fake login pages.
Passkeys may sound technical, but using one is usually straightforward. Here’s what happens and what you should know before trying one.
What is a passkey?
A passkey is a digital credential that your device or password manager keeps for a specific website or app. You unlock it with the same method you use to unlock your device, such as a fingerprint, face scan, or PIN.
The security behind a passkey uses a pair of digital keys. One stays with your device or passkey provider. The website keeps the matching public key, which can confirm your sign-in but cannot sign you in by itself.
In everyday terms, think of the public key as a lock and the private key as the key that opens it. The website can check that your passkey fits, but it never receives the private key. There is no password sitting on the website’s server for a thief to steal.
Your fingerprint or face data also stays on your device. The website receives confirmation that you approved the sign-in, not your biometric information.
How does signing in work?
When a website supports passkeys, you may see an option to create one or sign in with one. The exact wording varies. You might see “Passkey,” “Sign in with your fingerprint,” or “Sign in with your face.”
The usual steps are simple:
- Visit the real website or open its app.
- Choose the passkey sign-in option, or select the passkey saved for that account.
- Approve the request using your fingerprint, face, or device PIN.
Your device then completes the secure exchange with the website. You do not have to type or remember a password for that sign-in.
Why do passkeys help resist phishing?
Phishing is when someone tries to trick you into giving away information, often through a fake email, text, or website. A lookalike sign-in page may fool someone into typing a password. A passkey is designed to work only with the genuine website it belongs to.
For example, suppose a message directs you to a fake business email login page. Your passkey for the real email service will not provide the fake page with a usable login credential. The passkey checks the website’s identity as part of the sign-in process.
That is a major difference from a password, which you can accidentally type into the wrong page. Still, passkeys do not make every device or account risk-free. Keep your devices updated, secure your accounts, and treat unexpected login prompts carefully.
For more help spotting suspicious messages and links, see our post on rampant phishing.
Where are passkeys stored?
Passkeys may be stored in the built-in accounts and services you already use. Apple, Google, and Windows offer ways to manage passkeys within their ecosystems. Some password managers can store passkeys, too.
A passkey may be synchronized across your devices through the account or manager that stores it. For instance, a passkey saved through a provider may become available on another phone or computer signed in to the same provider.
Other passkeys are saved only on one device. These are often called device-bound passkeys. They do not sync elsewhere, so losing that device can make access more difficult unless you have another sign-in or recovery option.
Before creating one, notice which account or service will store it. You may need access to that account when setting up a replacement device.
What happens when you get a new phone or computer?
If your passkey syncs through an account, setting up the same account on a new device may make the passkey available there. Follow the provider’s instructions and complete any identity checks it requires.
If your passkey exists only on your old device, you may need to use the website’s recovery process or another sign-in method. Some sites let you add more than one passkey, which can help avoid relying on a single device.
You may also be able to sign in on a computer using a nearby phone. Choose an option such as “use a passkey from another device.” The computer may show a quick response (QR) code for your phone to scan. Approve the sign-in on your phone, and it can confirm your identity without moving the passkey onto the computer.
A QR code is not a backup passkey. It is simply a way for your phone to approve a sign-in on a nearby device.
Are passkeys the same as two-factor authentication?
A passkey generally replaces the familiar password-plus-code sign-in. You have the device holding or accessing the passkey, then prove it is you using a fingerprint, face, or PIN. Together, these steps make up the sign-in.
However, websites handle passkeys differently. Some may still ask for a password, an additional code, or another check in certain situations. Follow the instructions shown by the service, and do not assume every passkey login works exactly the same way.
If you want to understand the technology behind passkeys, the FIDO Alliance’s passkeys guide offers more detail. FIDO means Fast IDentity Online, the organization behind standards used for passkey sign-ins.
What are the limits?
Passkeys are useful, but they are not a perfect fit for every situation.
- Shared computers can be awkward. A passkey on your personal phone may be more convenient than saving a credential on a computer used by several people.
- Recovery depends on the service. Check what happens if your phone is lost, your passkey provider account is unavailable, or you change platforms.
- Email recovery matters. Many accounts use your email address to help restore access. Keep that inbox secure and make sure its recovery options are current.
- Some sites still require passwords. A service may offer passkeys for some sign-ins while keeping passwords for other steps or recovery.
For a small business, consider who controls the accounts used for email, banking, domain registration, and website administration. Make sure those accounts have sensible recovery arrangements, not just a sign-in method that works today.
How to start using passkeys
You do not need to switch every account at once. Start with an important account that offers passkeys and has a recovery process you understand.
Your email account is a practical place to begin because it can be used to recover access to other services. Open the official website or app yourself, then look under security or sign-in settings. Search for “passkey,” “passkeys,” or an option to sign in with your fingerprint or face.
Create the passkey, then test it while your existing sign-in method still works. Sign out and try signing in again. Check that your other devices and recovery options are ready, too.
Do not delete your password or remove another sign-in method until the passkey works reliably. A little overlap while you test is much less frustrating than getting locked out.
Passkeys can make everyday sign-ins easier while making phishing attempts harder to pull off. Start with one important account, learn how its recovery works, and add more when you feel comfortable.
For a related look at password managers, read Password Managers: One Key for a Whole Ring of Locks. Used together where appropriate, these tools can help you take better care of your online accounts.
by Charles Oropallo | Nov 5, 2026 | Email, Internet, The CW Corner
 A helpful out of office message lets customers know when you’ll return and where they can get help meanwhile. It can protect your time away while giving people a clear next step.
The trick is keeping it useful, brief, and safe. You don’t need to explain where you’re going or share your plans. A few thoughtful details can help customers feel looked after, even when you’re not checking email.
What should your out of office message say?
Include the information someone needs to decide what to do next. That usually means:
- When you’ll be away: Give the first and last dates you’ll be unavailable.
- When you expect to return: Use a clear date, not just “soon.”
- What to expect: Say whether you’ll be away from email or checking it occasionally.
- Who can help: Name an approved colleague or team contact for urgent requests.
- What happens next: Let people know when you’ll follow up.
For example, a customer writing about a time-sensitive appointment needs more than a vague “I’m away.” They need to know whether to wait, call your office, or contact someone else.
Before naming a substitute, ask their permission. Confirm they’re available, know what they can handle, and are comfortable having their contact details shared. A helpful message should not create an unexpected pile of work for a colleague.
Set expectations about replies
Be honest about how often you’ll check email. If you plan to disconnect, say so. If you might check occasionally, explain that replies could take longer than usual.
Avoid promising that you’ll reply as soon as you return. Your inbox may have other plans for your first morning back. “I’ll respond as soon as I can after I return” is considerate without promising an unrealistic turnaround.
Automatic replies also don’t necessarily go out with every message a person sends. Their frequency depends on your email service and settings. Gmail, for example, generally replies the first time someone contacts you. The same sender may receive another reply after several days or after you edit the message.
So, don’t rely on repeated automatic replies to remind someone about an urgent issue. Give them a clear alternate contact in the original response.
What not to include
A vacation reply should reassure people about your availability, not announce your plans to the world. Avoid details such as your destination, travel dates beyond your absence, where you’re staying, or when your home will be empty.
You also don’t need to list personal reasons for being away. “I’m out of the office” is enough. Keep sensitive business details, private client information, and internal schedules out of a reply that may reach people you don’t know.
Be cautious about offering a personal phone number. Share one only if you genuinely want calls and have permission to use it for work. An alternate business email or main office number is often more appropriate.
Finally, skip jokes that might confuse customers. A light tone is fine, but people should still understand when you’ll return and how to reach help. Keep the message clear enough to work for a new customer, not just a friend who knows your sense of humor.
A simple template to adapt
Use this as a starting point. Replace the bracketed details, then read it once as if you were a customer.
Subject: Out of office until [return date]
Thanks for your message. I’m out of the office from [start date] through [end date] and expect to return on [return date]. I [won’t be checking email / will check email occasionally, so replies may be delayed].
For urgent help with [type of request], please contact [name or team] at [email address or business phone]. Otherwise, I’ll respond as soon as I can after I return.
Best,
[Your name]
Keep the alternate contact description specific. “Contact my colleague” makes the customer guess. “For scheduling help, contact Morgan at [business email]” gives them a practical next step.
If you don’t have someone covering your inbox, say so plainly. You might direct customers to a business phone line, a shared support address, or an online appointment form. Don’t list a route that nobody is monitoring.
How to set up your vacation reply
The labels differ among email services, but the basic process is similar:
- Open your email settings. Look for “Vacation responder,” “Automatic replies,” or “Out of office.”
- Set a start and end time. Check the time zone and confirm the end date matches your return plan.
- Add a clear subject and message. Use your template, then verify every date and contact detail.
- Choose who receives the reply. Some services let you limit replies to your contacts or organization.
- Save the settings. If the service offers a scheduled end date, use it.
- Test the setup. Send a message from another account and confirm the reply reads correctly.
For Gmail, Google’s vacation responder instructions explain how to switch it on, enter dates, write your message, and save changes. Gmail also displays a notice in your inbox while the responder is active.
For Outlook, Microsoft’s automatic reply instructions cover different versions of Outlook. Available settings can vary by account type. If you don’t see the same options, check your provider’s guidance rather than assuming the feature is missing.
When choosing whether to reply to people outside your organization, consider your audience. A broad setting might send replies to newsletters or unwanted messages, too. If your service offers a contacts-only option, decide whether that suits your business.
Don’t forget to turn it off
A scheduled end date is helpful, but make checking the autoresponder part of your return routine. Open the setting on your first day back and confirm it has stopped. If you return earlier or your plans change, update or disable it right away.
Then review any customer requests that came in while you were away. Your automatic reply told people what to expect; a timely follow-up helps complete the promise.
It’s also worth checking your message before each new vacation. An old return date or the wrong substitute contact can confuse customers. Calendar reminders are useful. Sticky notes on your monitor are less reliable, especially if you work away from that desk.
If you use an alias or shared business address, check which inbox controls its automatic replies. The setting may belong to a particular mailbox rather than every address customers use. Our guide to email forwarding explains why separate email features can behave differently. This is a quick reminder to check the right account, not a substitute for testing your autoresponder.
Keep the reply helpful and low-risk
A good vacation message is simple: give your dates, explain your availability, and point urgent requests to someone who can help. Leave travel plans and private details out of it.
Test the reply before you leave, and check that it switches off when you return. If customers tell you they never received your email, our guide explains why business emails can land in spam. A little preparation now can make your time away easier for you and your customers.
by Charles Oropallo | Nov 4, 2026 | Internet, Small Business, The CW Corner
 If you have wondered what is SEO, it means search engine optimization. It’s the work of making your website easier for search engines to understand and easier for people to find.
You do not need to be a web professional to understand the basics. Good SEO starts with useful information, clear organization, and a website that works well for visitors.
How do search engines find websites?
Search engines use automated programs to discover pages across the web. Those programs follow links, visit pages, and gather information about what each page contains.
Next, a search engine may store and organize information about a page. This process is called indexing. A page must generally be indexed before it can appear in search results.
When someone searches, the search engine looks for pages that seem relevant to the words and the person’s needs. Google explains this process in its guide to how Search works.
Think of a search engine like a huge library. It tries to find the most useful books for each question, even though it cannot read every page exactly like a person.
Why do some websites appear higher?
Search engines try to show helpful, relevant results. They consider many signals, including the words on a page, how clearly it answers a question, and how other pages refer to it.
Location can matter, too. Someone searching for a nearby dentist may see local businesses before websites serving an entire country.
There is no single switch that guarantees a top position. Search engines use many signals, and their systems change over time. A competitor may also have more relevant information or a stronger local presence.
Google’s SEO Starter Guide makes an important point: there are no secret tricks that guarantee first place. SEO helps search engines understand your site and helps visitors decide whether it answers their needs.
SEO and paid ads are different
SEO generally focuses on unpaid search results. Your website may appear because a search engine believes a page is relevant to someone’s query.
Paid search ads are placements businesses pay to run. They are usually marked as advertisements, and their visibility depends on campaign settings, competition, and relevance.
Paying for an advertisement does not buy a higher position in unpaid results. The two approaches can work alongside each other, but they serve different purposes.
An advertisement may help promote a timely offer. Useful website content and a complete local business listing can support ongoing visibility. Choose based on your goals and budget, not pressure from someone promising guaranteed rankings.
Practical SEO steps you can take
You can improve some important parts of your website without learning complicated technical skills. Start with the following steps.
1. Give each page a clear title
A page title should tell people what the page is about. It may appear as the clickable heading in search results and in a browser tab.
For example, “Services” tells visitors very little. “Heating Repair and Maintenance in Peterborough, New Hampshire” describes the page more clearly.
Make titles accurate and natural. Avoid repeating the same phrase over and over. Search engines and people both appreciate clarity.
2. Write useful information for real people
Ask what a potential customer needs to know before contacting you. Explain your services, service area, hours, and how people can get started.
A local electrician might describe the kinds of work they handle and the towns they serve. A health professional might explain appointment options and what new patients should expect.
Answer common questions in plain language. Keep pages organized with meaningful headings and short paragraphs. You do not need to publish a blog every week if your existing pages already explain your services well.
3. Keep your local listings accurate
If you serve a local area, claim and maintain your Google Business Profile. Check that your business name, contact details, hours, and service information are current.
Also review listings on relevant directories and local organization websites. Make sure your basic business details match across them. An outdated phone number can frustrate customers, even if your website looks excellent.
For more practical local guidance, see our article on local SEO tips for small businesses.
4. Make sure your website works on phones
Many people search while using a phone. Your pages should be easy to read without pinching and zooming. Menus, buttons, and contact details should be easy to find and use.
Try visiting your website on your own phone. Can you quickly understand what you offer? Can you tap your phone number or complete a form without frustration?
If the site is difficult to use, visitors may leave and look elsewhere. Ask your developer or hosting provider for help if basic pages do not display properly.
5. Use clear links and a simple structure
Organize your website so people can move between related pages. A visitor should be able to get from your homepage to services, contact information, and other useful details without hunting.
Descriptive links help, too. “See our repair services” tells readers more than “click here.” Clear organization makes your site easier for both visitors and search engines to understand.
6. Give it time, and be wary of promises
SEO is ongoing work, not an instant switch. Search engines need to discover and understand your pages. Results can also depend on your competition, location, and the information people are seeking.
Check your website periodically. Update outdated details, improve confusing pages, and listen to customer questions. Small, steady improvements are more sensible than chasing every new SEO trick.
Be cautious if someone promises a guaranteed first-place ranking or claims they have a secret connection to a search engine. Our article about SEO scams explains why pressure tactics deserve a careful look.
A secure, reliable website helps visitors, too
SEO is only one part of a useful website. Visitors also need to feel comfortable contacting you and using your pages.
A secure connection, reliable hosting, and regular maintenance support a better overall experience. If you are unsure what the browser’s padlock means, read what an SSL certificate does.
These basics do not guarantee better rankings. They do help make your website more dependable for people who find it.
Start with the basics
So, what is SEO? It is a practical way to help search engines understand your website and help people find useful information.
Start with clear page titles, helpful content, accurate local listings, and a site that works well on phones. Be patient, make improvements as you go, and avoid anyone selling guaranteed rankings.
You do not have to do everything at once. A clear, helpful website is a strong place to begin.
by Charles Oropallo | Nov 3, 2026 | Do-It-Yourself, Internet, Small Business, The CW Corner
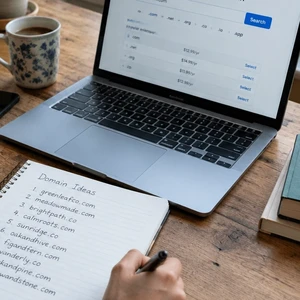 Choosing a domain name is easier when you think beyond what is available today. Your domain may appear on business cards, invoices, social profiles, and email addresses. It should be easy for people to remember and flexible enough to grow with your plans.
Before registering a name, take time to check how it sounds, what it might be confused with, and whether someone else already has a claim to it. A little research now can save you from a frustrating rebrand later.
Start with a name people can remember
A good domain name should be easy to say, hear, spell, and type. Imagine telling someone your web address over the phone. Would they know how to spell it without asking you to repeat it?
Short names are often easier to recall, but clarity matters more than squeezing every character out. A name that is short but confusing may send customers to the wrong place.
Try saying your favorite options aloud. Then ask someone else to write each one down after hearing it. If they regularly misspell the name, simplify it before registering.
Hyphens and numbers can make a domain harder to share. People may wonder whether a number is written as a digit or spelled out. Hyphens are easy to forget, especially when someone hears your address rather than seeing it.
Double letters can also cause mistakes. For example, people may not know whether a name contains one letter or two. These patterns are not always dealbreakers, but test them with real people before committing.
A quick test: say the name once, then ask someone to type it. If you need a long explanation, keep brainstorming.
Check for lookalikes and awkward meanings
A domain does not appear with spaces between its words. Read your shortlist in lowercase and look for combinations that could be misread. A harmless phrase with spaces can look less clear when everything runs together.
Also search for close variations. Check common misspellings, singular and plural forms, and names that sound similar when spoken. A neighboring business with a similar name could confuse customers, even if its website looks unrelated.
Search the exact name in a search engine and on social platforms. Look for businesses, products, or public discussions using the same wording. Check relevant maps, directories, and marketplaces too.
Think about what happens when someone mistypes your address. If a close variation leads to a competitor or an unrelated site, consider whether you can register that variation too. You do not need to buy every possible spelling. Focus on likely mistakes that could cause real confusion.
Check trademarks and existing businesses
Domain availability does not mean a name is legally available for your business. Registering a web address does not automatically give you trademark rights.
Search for the exact name and similar names used by businesses in related fields. In the United States, you can start with the United States Patent and Trademark Office trademark search. Search your state’s business-name records as well, and check for businesses using the name online.
Pay attention to names that look or sound alike, not just exact matches. A similar name may still confuse customers, particularly if both businesses offer related products or services.
If you plan to operate in other countries, check the relevant trademark resources there. The World Intellectual Property Organization also provides international trademark search information.
These searches are useful first steps, not a legal clearance opinion. If your preferred name appears close to an existing brand, ask a qualified trademark professional before investing in it. It is much easier to adjust a shortlist than to rebuild a brand.
See whether the matching social handles are available
Look for your preferred name on the social platforms your customers use. A matching handle can make your business easier to find and remember.
You do not need an account on every platform. But if your business relies on a particular network, check its handle before registering the domain. A name may look consistent on your website and social profiles, or it may require awkward additions.
If your exact handle is taken, consider a clear alternative. You might add a simple location or business descriptor, if that still sounds natural. Avoid a string of extra punctuation or numbers that makes the name harder to remember.
Check the name in more than one place. A platform’s search can reveal active accounts, while a direct profile search may show whether the exact handle is already in use. Availability can change, so reserve the accounts you genuinely plan to use.
Choose the extension that fits
The extension is the ending after the dot, such as .com or .org. A .com address is familiar to many people and can be a practical choice for businesses serving a broad audience.
Other endings may fit too. A .org extension is commonly associated with organizations, while .net is another established option. Newer extensions can offer a memorable match, but some visitors may still instinctively type .com.
Country-code extensions can make sense when your business serves a particular country. Before choosing one, check any local registration rules and whether the extension fits your plans.
Compare the regular renewal price, not just the introductory offer. Also consider how easy the extension is to say, whether customers will trust it, and whether it could be mistaken for another address.
Choose the extension you are comfortable sharing aloud and printing on your materials. A clever ending is not helpful if customers keep typing the wrong one.
Check a domain’s history before buying it
A domain that has been registered before may carry a past you cannot see from its current page. It could have been used for a business, a personal site, spam, or something else entirely.
Before buying a previously used domain, enter it into the Internet Archive’s Wayback Machine. Review available snapshots from different periods. Look for what the site represented and whether its content or purpose changed substantially.
Search the name in a search engine too. Try versions with and without “www,” and look for old references, complaints, or unrelated business listings. If you are buying from another owner, ask about the domain’s past use and confirm that the seller can transfer it to you.
The Wayback Machine is helpful, but incomplete. A missing page does not prove that the domain was never used. Treat what you find as useful clues, not a complete history.
Protect your domain after registration
Choosing a name is only the beginning. Make sure the domain is registered to you or your business, with contact details you can access. Keep your registrar account secure and use a monitored email address for renewal notices.
Turn on automatic renewal if it suits your situation, and keep your payment details current. Add a reminder to check the renewal date as well. An expired domain can interrupt your website and email, and recovering it may be difficult. Read more in our guide to what happens when your domain expires.
Enable a domain lock when your registrar offers one. This helps prevent unauthorized transfers, but it does not replace a strong password or account security. See why your domain lock matters.
Consider registration-data privacy if your registrar provides it. Privacy services can help limit the personal details displayed in public registration records, although they do not make you anonymous. Learn more in our guide to WHOIS and what the internet can see about your domain.
Make a confident choice
Before you register, say your shortlist aloud, check likely spelling mistakes, search for similar businesses, and review trademark records. Compare social handles and extensions, and look into a domain’s history if it has had a previous owner.
A strong domain does not need to be clever. It needs to be clear, memorable, and right for the people you want to reach. Take the time to check your choice now, and you can move forward with more confidence.





 European Union General Data Protection Regulation Compliant