by Charles Oropallo | Nov 19, 2026 | Passwords, Security, Small Business, The CW Corner
 Hardware security keys are small devices that give your important accounts a strong, physical check at sign-in. You plug one into a computer or tap it against a compatible phone. Think of it as a small key that helps prove you are really you.
For most accounts, the security key is a second step after your password. Some services also let you use a key to sign in without entering a password. Either way, it can make fake login pages much less effective.
What is a hardware security key?
A hardware security key is a small device that connects through a Universal Serial Bus (USB) port or communicates wirelessly with a phone. During sign-in, you may need to touch its button or tap it against your device.
The key works with your browser and the service’s sign-in system. It helps confirm that you are signing in to the real website, not a convincing imitation.
Some keys include a fingerprint reader. Others ask you to touch a button. Either style can work well. Choose a method that feels comfortable and suits the accounts and devices you use.
You may also see keys described as supporting Web Authentication (WebAuthn) and Fast Identity Online (FIDO) standards. Those standards let websites and security keys work together for secure sign-ins. Check that the services you rely on support them.
Why does a key stop many phishing attempts?
A password or code can be copied. If a fake website tricks you into entering a password or a temporary code, the attacker may use it on the real account before it expires.
A hardware security key works differently. During sign-in, the browser and key use the website’s identity to check that the request is for the right service. A key registered for your real email provider will not answer a lookalike site pretending to be that provider.
Picture a key cut for one particular lock. A copied key shape may look convincing, but it will not turn the real lock. A security key uses a similar idea, with digital information instead of metal teeth.
This protection is why keys can resist phishing better than codes you type into a webpage. It does not make every account or device invulnerable. Use the key only on websites you opened yourself, and protect your devices, passwords, and account recovery options.
For another passwordless sign-in option, see Passkeys Explained: Signing In Without a Password. To compare common second-step methods, read Authenticator Apps vs. Text Codes: Which Two-Factor Sign-In Is Safer?.
What should you look for when buying one?
Start by checking that the key supports WebAuthn and FIDO standards. Well-known brands make these devices, but focus on compatibility rather than choosing based on a logo.
Consider how you will connect the key. A model with both a computer connector and a phone-friendly option can be useful if you sign in from both. Check your computer and phone ports before buying.
Buy two keys: one for regular use and one as a spare. Store the spare somewhere safe and separate from your everyday key. A backup does not help much if both keys live on the same key ring.
Some keys have a button you touch during sign-in. Others include a fingerprint reader. Either can be a practical choice. Follow the maker’s setup instructions, and keep the key protected from damage or loss.
Which accounts should you secure first?
Start with accounts that could unlock or disrupt many other parts of your life or business:
- Your email account. Password-reset links for many services arrive in your inbox. That makes email a kind of master key.
- Your domain registrar. Someone with access may be able to change where your website address points.
- Your web hosting account. Access could allow changes to your website or its hosting settings.
- Your bank and payment accounts. Protect accounts that handle business funds or personal savings.
- Your password manager. It may hold the sign-in details for many of your other accounts.
A password manager can help you use a different password for every service. Learn more in Password Managers: One Key for a Whole Ring of Locks.
If your email account is compromised, the damage can spread quickly through password resets. Our email account recovery walkthrough explains why that inbox deserves special attention.
How do you set up a key?
The exact wording varies between services, but the process is usually straightforward:
- Open the service’s official website or app yourself. Avoid starting from an unexpected email link.
- Sign in and open the account’s security or sign-in settings.
- Choose the option to add a security key, then follow the instructions.
- Give the key a name you will recognize, such as “Office key” or “Backup key.”
- While you are still signed in, add your spare key in the same session.
- Test that both keys work before closing the settings page.
Adding the spare right away matters. You may not remember to do it later, and recovering an account can be much harder if your only key disappears.
If the service offers recovery codes, print them and store them somewhere secure, away from your keys. Treat those codes like spare keys to the account. Do not leave them beside your computer or save them in an inbox that the account itself can unlock.
Can your phone act as a security key?
Modern phones can take part in secure sign-ins. Some can approve a login on another device, while many also store passkeys for accounts that support them.
Passkeys are related to security keys, but they are not exactly the same thing. A passkey is a digital sign-in credential stored on a phone, computer, or supported account service. A physical security key is a separate device you carry and connect when needed.
A phone that receives a text message is not the same protection as a physical security key. Text codes can be intercepted or stolen through phone-number scams. Learn about that risk in our article on SIM swap scams.
What are the trade-offs?
You need to have the key with you when signing in, unless you use another supported method. Some services limit how many keys you can register. Others do not support security keys at all.
Losing every registered key can lock you out. That is why you should set up a spare and save recovery codes before trouble starts. Check each service’s recovery process while you still have access.
A key also cannot protect an account if someone has already gained access another way, such as through an open sign-in session. Keep devices updated, watch for unexpected account alerts, and remove keys you no longer use.
A small-business security step worth planning
If employees or contractors can change your website, pay bills, or access customer information, consider issuing keys to those people. Keep a simple record of who holds each key and which accounts it protects.
When someone leaves, remove their key from the relevant accounts the same day. Treat it like a building key: record who has it, and collect or disable access when their work ends.
For a handful of accounts that could ruin your week if they were taken over, hardware security keys are worth considering. Start with your email, domain, hosting, banking, and password manager accounts. Add a spare, save recovery codes, and ask for help if setup gets confusing.


by Charles Oropallo | Nov 17, 2026 | Security, Technical Help, The CW Corner, Website Development
A website hacked warning can turn an ordinary workday into a stressful one. Take a breath: a hacked site is a fixable problem, not the end of your business. Don’t delete the site or wipe everything in a panic. First, preserve what you have, then work through recovery in order.
How you might discover a hack
Sometimes Google shows a warning beside your website in search results. Your hosting provider might email you about suspicious activity. Or a customer might say your site sent them somewhere unexpected.
Other clues can be less obvious: unfamiliar administrator accounts or files, pages you never wrote appearing in search results, or a site that suddenly feels slow. Some hacks are silent. You may hear about the problem from someone else before noticing anything yourself.
Google’s guide, How do I know if my site was hacked?, explains that harmful changes can be hidden from site owners. So, a normal-looking homepage is not proof that every page is clean.
Step 1: Take a snapshot before changing anything
Before you start cleanup, ask your host or developer to save a full copy of the website files and a separate copy of the database. The database holds your posts, pages, settings, and other site information.
Write down the exact date and time of the snapshot. Keep this copy separate from the live site, and label it clearly as a snapshot of the site as found. Do not treat it as a clean backup.
Why bother keeping a copy of a compromised site? It can help show what changed and when. It may also help a technician identify how someone got in. A backup created after the break-in can carry the problem forward, so don’t restore it as if it were known-good.
For more on what backups contain, read What Website Backups Actually Cover (and What They Don’t).
Step 2: Close the way in
Once the snapshot is safely kept, change the passwords connected to site access. This includes your hosting control panel, WordPress administrator accounts, file transfer accounts, and database.
File Transfer Protocol (FTP) and Secure File Transfer Protocol (SFTP) are methods for accessing website files. If you use either, change its password too. Coordinate the database password change with your host or developer, since the website may need updated settings to connect afterward.
Sign out active sessions where you can. Review the list of WordPress administrators and hosting file transfer accounts. Remove any account you do not recognize, but record its details first.
Make password changes from a clean, trusted device. If an account or computer may also be compromised, ask a qualified technician for help before entering new credentials.
Step 3: Find the entry point honestly
Cleanup is not complete if the way in remains open. Common causes include outdated WordPress software, plugins, or themes; weak or reused passwords; and stolen logins from a phishing page or infected computer.
A compromised account on shared hosting can also create problems for neighboring sites. Your provider can help investigate whether the hosting environment is involved.
Look for evidence with your host or developer. That may include unfamiliar accounts, unexpected files, unusual site changes, or activity in available logs. A log is a record of events on your website or server.
Don’t settle for removing the strange page you can see. The visible symptom may be only one sign of a deeper problem. Our older article, Best Practices for Mitigating Website Hacks, covers ways to reduce the risk of another incident.
Step 4: Choose between a clean restore and cleanup
The right recovery method depends on what happened and what backups are available. If you have a verified, known-good backup from before the intrusion, restoring it may be the clearest route.
But first, close the entry point. Restoring an old copy without fixing the cause can simply reopen the same hole. Check that the backup is trustworthy and does not include the attacker’s changes.
If no suitable backup exists, a qualified professional may need to clean the site in place. This means inspecting and repairing the files and database that make up the current site. Malware can hide in places a basic scan misses, and injected content may live in the database, not just website files.
Google’s Security issues report guidance also recommends fixing the issue throughout the site, not just on example pages. If the work is beyond your comfort level, get help. Guessing at unfamiliar code can make recovery harder.
Step 5: Request removal of Google warnings
After the site has been cleaned or safely restored, check Google Search Console’s Security issues report. It may identify examples of affected pages and explain what Google detected.
Fix all the listed issues, then request a review through the report. Describe what you found and what you changed. Google needs to review the site before removing its warning.
A website that looks normal to you may still have a warning in Google results or browsers. The warning will not necessarily disappear just because the site appears fine now. Google’s review process can take time, so check the report for updates.
If you need an introduction, see our guide to Google Search Console.
Step 6: Tell customers plainly
If customers may have seen redirects, suspicious pages, or a browser warning, send a short, honest note. Silence can leave people confused and make them wonder whether you know about the problem.
For example:
We recently discovered unauthorized changes to our website. We have secured the site and are investigating how the changes occurred. If you visited during this period and entered information, please contact us using the details below. We’ll share relevant updates as we learn more.
Adjust this wording to match what you know. Don’t claim customer information was exposed unless that has been established. Don’t blame an unnamed “third party” as a way to dodge responsibility. Be clear about what happened, what you did, and what customers should do.
Step 7: Report the incident where it matters
Tell your hosting provider about the intrusion. Share relevant details and ask whether they see activity affecting your account or hosting environment. Depending on what happened, you may also need to contact your payment provider, insurer, or other relevant reporting channels.
If customer data or payment details might have been exposed, this becomes a different conversation. Notification and legal duties can depend on the information, location, and circumstances involved. Get qualified legal advice rather than guessing about what you must do.
Step 8: Reduce the chance of a repeat
Once recovery is underway, keep future care practical and manageable. Keep WordPress, plugins, and themes updated. Use unique, strong passwords and two-factor authentication (2FA) for administrator access.
Remove plugins and themes you no longer use. Keep regular backups in a separate location, and test a restore before an emergency. For more prevention guidance, see our article on mitigating website hacks.
The business cost of a hack
A hack can cost more than cleanup time. Customers may hesitate to visit or submit a form. Search warnings can interrupt new enquiries, and your staff may spend valuable hours answering questions instead of serving customers.
That is why the awkward customer email is often cheaper than silence. A clear update gives people a reason to trust your next message. A site you cannot restore to a known-good state can also cost far more than a sensible backup routine.
Recovery is easier when you know who to call, where your backups live, and what they include. Ask your host or developer those questions before a crisis, not while one is unfolding.
Work through the steps, and ask for help
A website hack is upsetting, but you do not have to solve everything at once. Preserve a snapshot, close the way in, investigate the cause, and choose a careful cleanup or restore.
Write down what you do and when. Get help early rather than guessing, especially if you cannot confirm the site is clean. A calm, documented recovery is a much better plan than a rushed wipe.
by Charles Oropallo | Nov 16, 2026 | Email, Security, Small Business, Technical Help, The CW Corner
 Calm, careful steps can help you regain control and protect the accounts connected to your email.
A hacked email account can first show itself in an ordinary, unsettling way. A friend asks why you sent them a strange link. Contacts receive replies you never wrote. Your sent folder contains unfamiliar messages, or your password suddenly stops working. Maybe your provider sends a security warning, or mail you expected never arrives.
Take it seriously, but take it one step at a time. Your mailbox is a master key: password-reset links for many other accounts land there. Here’s what to do, in order.
First, pause. Don’t reply to the thief.
Don’t panic, and don’t email your account asking who is there. You may only give the intruder another chance to read your response. Don’t click links or open attachments in suspicious messages, either.
If you can, use a device you trust for the recovery steps. If the device seems infected or behaves strangely, use another trusted device.
Step 1: Get back into your account
Go directly to your email provider’s official website or app. Don’t use a sign-in link from an unexpected message.
If you’re locked out, type the provider’s official account-recovery address into your browser yourself. Follow its instructions, and be ready to wait while it verifies that the account belongs to you. That wait can be frustrating, but it’s safer than trusting a stranger who offers a shortcut.
Step 2: Change the password
Once you regain access, change the email password first. Choose a password you haven’t used elsewhere.
Then change it anywhere else you reused it. Reusing one password is what can turn one break-in into several: if someone learns it from one account, they can try it on others.
Start with accounts that can reach money, sensitive information, or more account-recovery options. A password manager can help you create and keep unique passwords.
Step 3: Check the settings that are easy to miss
A password change doesn’t necessarily remove quiet changes made inside your mailbox. Go through the security and mail settings carefully. Remove or correct anything you don’t recognize.
Check for:
- A new recovery email address or phone number.
- A forwarding rule or filter that copies, hides, or moves incoming mail.
- A filter that deletes replies or security alerts.
- An app password or unfamiliar connected third-party app.
- A changed email signature or automatic reply.
- A delegate or shared-access setting you didn’t add.
- A new folder that files replies out of sight.
Forwarding rules and filters are especially easy to overlook. They can keep copying or hiding messages even after you change your password. That could let someone watch for password-reset emails, or keep you from seeing replies.
If you find something suspicious, remove it and note what it was. Review the settings again after making changes to confirm they haven’t returned.
Step 4: Sign out other sessions
Use your provider’s security settings to sign out of every session and device. This matters because changing your password may not close every session that was already open.
Then check recent sign-in or security activity. Look for places, times, devices, or browsers you don’t recognize. If anything seems unfamiliar, record it and use the provider’s security or abuse-report channel.
Step 5: Check which accounts the mailbox could unlock
Your email account may help someone reset access to other services. Check the accounts connected to it, including:
- Bank and credit card accounts.
- Payment processors.
- Your domain registrar and website hosting control panel.
- Social media accounts and cloud storage.
- Supplier, customer, or other business portals.
Change passwords for those accounts, too. Start with money and domains. If someone controls your domain or hosting account, they may be able to disrupt your website or use your business identity.
Step 6: Warn people and contact your bank
Your name is now a trusted sender in your contacts’ inboxes. Let people know through a separate, trusted channel, such as a phone call or a different email account.
You can keep your warning plain:
My email account was compromised. Please don’t open recent links or attachments from me. I will never send a link asking for your password or payment.
Tell your bank the same day. If money moved or a card was used, contact your card issuer that day, too. Use the number on your card or the institution’s official website.
Step 7: Report the incident and keep notes
Report the problem through your email provider’s own security or abuse channel. If personal identity details were exposed, use the Federal Trade Commission’s IdentityTheft.gov recovery steps.
Keep a short record of dates, unfamiliar changes, account contacts, and the fixes you made. Those notes can help if you need to explain what happened or follow up later.
Step 8: Make the next break-in harder
Once your account is clean, take a little time to strengthen the setup:
- Turn on two-factor sign-in with an authenticator app rather than texted codes. For setup context, see our guide to authenticator apps and text codes. The Cybersecurity and Infrastructure Security Agency’s guidance also encourages businesses to require multifactor authentication.
- Remove recovery email addresses and phone numbers that no longer belong to you.
- Use a password manager so each account has a unique password.
- Type a website address yourself instead of trusting a sign-in link in a message.
- Check whether a breach-notification service can alert you if your email address appears in a known data breach.
A stolen password from an old website is often how someone gets into a current mailbox. If your recovery phone is involved in a phone-number takeover, read about Subscriber Identity Module (SIM) swap scams.
If you run a business, check these risks too
A message with your name or logo can feel trustworthy to customers. An intruder may exploit that trust by sending fake invoices or changing bank details in a payment request. Warn customers and suppliers if they may have received suspicious messages.
Your mailbox may also control access to your domain registrar and hosting account. Make sure those accounts are protected, and review their recovery settings.
For a business, recovery email addresses and phone numbers should not depend on one person’s personal phone alone. Plan who can regain access if that person is unavailable or loses the device.
Keep going, and ask for help if you need it
An afternoon spent recovering and securing your accounts now can spare you a very bad week later. Work through the steps in order, and don’t leave suspicious settings for “sometime later.”
If this feels over your head, ask for help rather than leaving the recovery half done. Hopefully, these steps will help you regain control with a little more confidence.
by Charles Oropallo | Nov 15, 2026 | Scams, Security, Small Business, Technical Help, The CW Corner
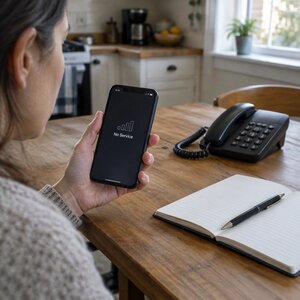 A SIM swap scam can turn your phone number into a key to your email, bank, and business accounts. If your phone suddenly loses service without explanation, don’t dismiss it as a glitch. It could be a warning that someone else now controls your number.
What is a SIM swap?
A subscriber identity module (SIM) card is the small chip that connects your phone number to a mobile phone. A swap happens when someone persuades your mobile carrier to move your number onto a SIM card they control.
Once the transfer takes effect, your phone may lose service. The scammer’s phone can start receiving calls and text messages intended for you. A transfer to another carrier, often called a port-out, can create a similar problem.
The SIM itself isn’t the important prize. Your phone number is. Many online accounts use it to send sign-in codes, password-reset codes, bank alerts, or calls from a fraud team. If a criminal controls your number, they may be able to receive those messages and answer those calls.
A stolen number does not automatically unlock every account. But it can give a scammer a useful route into accounts that rely on your phone for verification or recovery. That’s why a sudden loss of service deserves attention.
How does the scammer get your number?
Usually, the criminal does not hack your carrier’s network. They contact the carrier and try to convince a representative that they are you.
They may gather personal details from data breaches, social media, phishing messages, or other sources. Then they use those details to request a replacement SIM or move your number to another carrier. In some cases, an insider at a store may help.
The basic trick is impersonation, backed by patience. A caller may sound confident, know just enough about you, and keep trying until someone approves the change.
That’s also why you should be cautious if someone contacts you and asks for a carrier passcode or a one-time sign-in code. Hang up and contact the company using a number from your bill, card, or its official website. Don’t hand over account keys to an unexpected caller.
Warning signs to take seriously
These changes can have harmless causes, including local outages or a damaged phone. But if they appear suddenly and you haven’t changed your service, treat them as urgent.
- Your phone shows “No Service” or “SIM not provisioned” in a place with normally good coverage.
- Your phone suddenly allows emergency calls only.
- Your carrier sends a message about a SIM change or number transfer you did not request.
- Your number appears to have changed in an account, or you receive a welcome message from a new carrier.
- You are unexpectedly locked out of accounts or receive password-reset alerts you did not request.
The Federal Bureau of Investigation (FBI) has warned that criminals use these schemes to reach bank and social media accounts. See its alert on SIM swap schemes.
If your phone loses service for no clear reason, don’t wait around hoping it will sort itself out. A quick response can help limit what a thief can do.
What to do in the first hour
If you suspect a swap, borrow another phone or use a landline. Don’t rely on the affected phone to make calls or receive verification messages.
First, call your mobile carrier from that other phone. Use the number on your bill or the carrier’s official website. Explain that you suspect an unauthorized SIM change or number transfer. Ask the carrier to freeze the number, stop further changes, and restore the number to your SIM.
Ask what additional protections the carrier can put on your account. If the first person you reach cannot help, request the team that handles suspected account or number-transfer fraud. Keep notes about your calls and any case references.
Next, secure your email account. Email is often the master key because password-reset links for other accounts may arrive there. From a trusted device, change the email password if you can. Review recovery details, sign out of unfamiliar sessions, and check for forwarding settings you did not add.
Then contact your bank and card issuers. Tell them you may have lost control of your phone number. Ask them to review recent activity and flag anything unfamiliar. Follow their instructions if they recommend temporarily restricting access.
Finally, change passwords on financial and business accounts. Prioritize accounts that use your number for recovery, or that could affect your money, website, domain, or customer communications. A password manager can help you create unique passwords instead of reusing one. Our password managers guide explains how to get started.
For more recovery guidance, the Federal Trade Commission’s identity theft resource offers steps for people who discover misuse of their personal information.
Practical ways to reduce your risk
Call your carrier before anything goes wrong. Ask whether it offers a port-out PIN (personal identification number), number-transfer freeze, or account passcode. Ask how to enable available protections and whether a store visit can override them. Carrier options and procedures vary, so check directly with your provider.
Where important accounts allow it, move away from texted sign-in codes. Consider an authenticator app or security key instead. These options don’t rely on a text arriving through your phone number. Our guide to authenticator apps and text codes covers the sign-in choices. You can also read Passkeys Explained for another option some services support.
Keep a separate recovery email that does not depend on the same phone number. Make sure you can access it, and protect it with a strong, unique password.
Be careful about details you share online. A birthday, pet’s name, or mother’s maiden name may also be an answer to a security question. Think twice before posting personal facts that could help someone impersonate you.
A business number can put customers at risk, too
If the number on your website or business listing gets swapped, customers may reach the person controlling it instead of you. That can mean missed inquiries and confusion. The same number may also help someone reset business accounts connected to it.
Review which phone number is attached to your email, banking, domain registration, website administration, and other important services. Ask whether a single person’s personal mobile number should control all those accounts.
For a small business, a shared or separately managed business line may make more sense for some account recovery arrangements. Whatever number you choose, know who controls it and what protections your carrier can apply.
Make the carrier call this week’s small job
A SIM swap scam is rare, but it is not imaginary. If your number suddenly stops working, act promptly: contact your carrier, secure email, alert financial institutions, and then protect your other important accounts.
The preparation doesn’t need to become a major project. One call to your carrier, followed by an afternoon moving important accounts to better sign-in methods, can make a meaningful difference. Make that call this week, while your phone is still working.
by Charles Oropallo | Nov 12, 2026 | Do-It-Yourself, Internet, Security, Small Business, The CW Corner
 Public Wi-Fi safety matters whenever you connect at a coffee shop, airport, hotel, or other shared place. These networks are convenient, but you do not control who set them up or who else is connected. That calls for sensible caution, not panic.
The familiar warning that everyone nearby can automatically read everything you do is too broad. Modern websites and apps often encrypt their connections. Still, the network itself can create risks, and a convincing fake hotspot can fool you into connecting.
Here’s what to watch for, and how to make safer choices without giving up your coffee-shop table.
What can someone on public Wi-Fi see?
When you use an open or poorly secured network, other people may be able to observe some network activity. The risk is greater when a website or service sends information without encryption.
HTTPS (Hypertext Transfer Protocol Secure) encrypts the connection between your browser and the website you visit. That helps keep the contents of your connection private while they travel across the network. It is common on websites and in apps today.
But encryption is not a reason to stop paying attention. A network operator may still see some connection details, such as which online services your device contacts. And HTTPS cannot protect information you type into a fake website or sign-in page.
For a quick reminder about secure website connections, see our earlier article on SSL (Secure Sockets Layer). We’ll keep the details simple here: check the address and connection, and don’t ignore browser warnings.
Watch for fake look-alike hotspots
One realistic risk is a fake hotspot designed to look like the venue’s real network. It may use a similar name, a slightly different spelling, or a name suggesting “free Wi-Fi.” A stronger signal does not prove that a network is genuine.
Imagine sitting in an airport and seeing two networks with nearly identical names. You might choose the first one, connect, and see a sign-in page that looks familiar. If the network is controlled by someone else, that page could be designed to collect information.
Before connecting, ask staff for the exact network name and any instructions. Use the venue’s official signage as a helpful reference, but verify if anything looks unusual. Be wary of unexpected requests for passwords, payment details, or extra downloads just to get online.
A lock symbol beside a network name does not confirm that the network belongs to the business. It only indicates that a password or other protection is involved. Confirm the name with staff instead of guessing.
The Cybersecurity and Infrastructure Security Agency (CISA) describes fake “evil twin” hotspots and advises confirming a public network’s name before using it. Read its wireless network safety guidance.
Use a personal hotspot for sensitive tasks
When practical, use your phone’s cellular connection or personal hotspot for sensitive work. That can be a better choice for banking, payment tasks, business administration, account recovery, or handling private client information.
A personal hotspot uses your phone’s mobile data connection to provide internet access to your other device. It avoids the coffee shop’s shared Wi-Fi network, although it does not replace other good security habits. Use a strong hotspot password, and switch the hotspot off when you are finished.
If cellular service is weak or unavailable, pause and consider whether the task can wait. Reading a news story is different from changing the password for your business email. A little patience can be a worthwhile security measure.
Check the website before signing in
If you do use public Wi-Fi, check that important websites use HTTPS and that the web address is the one you intended to visit. A lock icon can indicate an encrypted connection, but it does not prove the website itself is genuine.
Look closely at the address before entering a password or payment information. A fake page can use a name that resembles a real business. If your browser shows a certificate or security warning, stop. Don’t click through just to make the warning go away.
When possible, avoid signing in to sensitive accounts on a shared network. If you must access one, use the official app or type the website address yourself. Do not rely on a link from an unexpected message or a pop-up from the Wi-Fi network.
Public Wi-Fi may also ask you to accept terms on a sign-in page, often called a captive portal. A basic access page can be normal. But be cautious if it asks for your email password, banking credentials, a one-time sign-in code, or an unexpected software installation. When in doubt, disconnect and ask venue staff.
For more help with spotting fraudulent messages and links, see our existing article about phishing. The key point here is simple: don’t hand over account details just because a page appeared after you connected.
Turn off automatic connections and file sharing
Your device may automatically join networks it has used before. That can be handy at home, but it can also lead your device to connect without you noticing.
Turn off automatic joining for public networks, or remove networks you no longer need. Then choose a network manually when you arrive. If a familiar network name appears in an unfamiliar place, verify it before connecting.
Also turn off file sharing and network discovery when using public Wi-Fi. These settings can make your computer visible to other devices nearby. CISA recommends disabling file sharing on public networks. You can enable it again when you return to a trusted network, if you need it.
Keep your phone, computer, browser, and apps updated. Updates fix known problems and help protect the device you carry between home, work, and public spaces. A screen lock also matters if someone can physically reach your device.
What does a VPN do?
A VPN (virtual private network) creates an encrypted connection between your device and a VPN service. Think of it as a protected tunnel through the shared network. It can make it harder for other people on that Wi-Fi network to observe your traffic.
A reputable VPN can be useful when you regularly use public Wi-Fi, especially for work. But it is not an invisibility cloak. The VPN service becomes part of your connection, and you still need HTTPS for the connection between the VPN service and the website.
A VPN also cannot make a fake sign-in page trustworthy. It will not protect you if you enter your password into a look-alike website or install a harmful app. Choose a VPN carefully, keep its app updated, and treat requests to install certificates or unfamiliar software as a reason to pause.
If you connect to public Wi-Fi often for business, ask your IT provider or support contact whether a VPN is appropriate for your work.
Keep your sign-in habits strong
Public Wi-Fi safety works best alongside the account protections you use everywhere else. Two-factor authentication (2FA) adds another sign-in check beyond your password. It can help if someone learns that password, though it cannot make a fake login page safe.
We recently covered authenticator apps and text codes. That article explains how those sign-in options differ. Use the protections available on your important accounts, especially email and business services.
A practical routine before you connect
Before joining a coffee-shop, airport, or hotel network, take a moment to:
- Ask staff to confirm the exact network name.
- Turn off automatic joining and file sharing.
- Use your phone’s hotspot for sensitive tasks when practical.
- Check the web address and HTTPS before signing in.
- Stop if you see a browser warning or an unusual portal request.
- Use a reputable VPN when appropriate, while continuing to check websites.
Public Wi-Fi is not automatically dangerous, and you do not need to treat every café like a spy movie. Just remember that a shared network is outside your control. Verify the hotspot, protect your device, and save sensitive work for a safer connection when you can.
by Charles Oropallo | Nov 11, 2026 | Do-It-Yourself, Internet, Passwords, Security, Small Business, The CW Corner
Authenticator apps vs. text codes is a practical security choice for your email, business website, and other important accounts. Both add a step beyond your password, but they protect that step differently. For most people, an authenticator app is safer than a code sent by text.
What is two-factor authentication?
Two-factor authentication (2FA) asks you to prove your identity in two different ways. Usually, you enter something you know, such as your password, and confirm something you have, such as your phone.
That extra check can help if someone steals or guesses your password. They may still need access to your phone or authenticator app before they can sign in.
Two-factor authentication is not a guarantee against every threat. It does make password-only access harder, which is a worthwhile improvement for important accounts.
How do text message codes work?
With short message service (SMS) verification, the website sends a temporary code to your phone number. You enter that code after your password to finish signing in.
It is familiar and usually easy to set up. But SMS depends on your phone number and mobile carrier, which creates some weaknesses.
- SIM swap scams: A scammer may trick your carrier into moving your number to a phone they control. This is called a subscriber identity module (SIM) swap. If successful, they may receive your login texts.
- Lost or unavailable phone: You may be unable to receive codes if your phone is lost, its battery is dead, or you have no service.
- Delayed or missing messages: Texts do not always arrive promptly. That can leave you waiting when you need access.
- Visible or accessible messages: A code might appear in a lock-screen notification. Depending on your settings and apps, messages may also be accessible in other places.
SMS codes are still better than using only a password in many situations. But they rely on a phone network and number that can be targeted or temporarily unavailable. The Cybersecurity and Infrastructure Security Agency (CISA) advises using text-based codes only as a last resort when stronger options are unavailable. See its multifactor authentication guidance.
How does an authenticator app work?
An authenticator app creates a temporary code on your phone or computer. During setup, the account and app share a secret, usually transferred by scanning a quick response (QR) code. The app uses that secret and the current time to create a six-digit code.
The code is generated locally, inside the app. Your phone does not need mobile service or an internet connection to display it. So, the code can still appear in airplane mode or where reception is poor.
You will generally need internet access to reach the website and complete sign-in. “Works offline” means the app can generate the code without a network connection. It does not mean you can sign in to an online service without internet access.
Unlike an SMS code, the authenticator code does not travel through your carrier’s text messaging system. A SIM swap alone does not give a scammer the secret stored in your authenticator app.
Which option is safer?
When you can choose between SMS and an authenticator app, an authenticator app is generally safer. Its code is not tied to your phone number, so a SIM swap will not automatically send your codes to someone else.
That does not make authenticator apps invulnerable. Someone who steals your password and tricks you into entering a current code on a fake sign-in page may still get access. Protect your device, check the website address, and do not share codes with anyone who contacts you unexpectedly.
Some accounts offer stronger sign-in methods, including passkeys. Passkeys can provide better protection against fake login pages. We explain how they work in Passkeys Explained: Signing In Without a Password.
How to set up an authenticator app
The steps vary a little by website, but the process is usually straightforward:
- Open the real website or app yourself. Avoid setup links in unexpected emails or text messages.
- Go to its security or sign-in settings. Look for an authenticator app, verification app, or two-step sign-in option.
- Choose the app option. The service should show a QR code and explain what to do next.
- Open your authenticator app and scan the code. Follow the service’s instructions, then enter the app’s current code to confirm setup.
- Save the recovery codes. Store them somewhere safe, such as a printed sheet in a secure place or a password manager you can access independently.
- Test your new sign-in. Sign out and sign in again while your existing method still works.
Do not photograph a recovery code casually or leave it beside your computer. Treat it like a spare key: anyone who gets it may be able to access your account.
Keep the old method available until you have tested the app and confirmed your recovery options. Then review the account’s settings. Some services keep SMS enabled as a fallback, even after you add an authenticator app.
What if you get a new phone?
Plan the move before you retire your old phone. Many authenticator apps have a way to transfer accounts, but the process varies by app.
Follow the app’s official transfer instructions while you can still use the old device. Add the authenticator to your new phone, test sign-in, and make sure your recovery codes are available. Only then remove the old device or erase it.
If your old phone is already gone, use the service’s recovery process. This is exactly why saving recovery codes during setup matters.
Keep the rest of your account secure
An authenticator app is software running on a device. The device could be lost, stolen, or compromised. Keep its operating system updated, use a secure screen lock, and review which notifications appear on your lock screen.
Your email recovery account matters, too. If someone can take over your email, they may be able to reset passwords elsewhere. Protect that inbox with a strong, unique password and two-factor sign-in. A password manager can help you keep unique passwords without memorizing every one.
A simple way to get started
You do not have to update every account today. Turn on two-factor authentication with whichever method a site offers first. Any extra sign-in check is generally better than relying on a password alone.
When you are ready, move your most important accounts to an authenticator app. Start with email, then consider banking, domain registration, website administration, and other accounts that could affect your business. Keep recovery details safe, and test each change before removing an older sign-in method.
For more on safer sign-ins, read Passkeys Explained: Signing In Without a Password and Password Managers: One Key for a Whole Ring of Locks.





 European Union General Data Protection Regulation Compliant