by Charles Oropallo | Oct 31, 2026 | Do-It-Yourself, Small Business, Technical Help, The CW Corner, Website Development, Website Updates
 A website maintenance routine should be simple, scheduled, and focused on the features your customers depend on. Backups matter, but they are only one part of caring for a website.
A few repeatable checks can help catch problems before a customer does. Think of your site like a storefront: you keep the doors working, remove clutter, and make sure the information inside is current.
You do not need to become a web professional to follow a basic routine. Set aside time regularly, keep notes, and ask for help when a change feels risky.
Start with a manageable schedule
For many small-business websites, a monthly check-in and a more thorough quarterly review provide a useful starting point. Adjust the schedule to match how often your site changes and how important its features are to daily business.
For example, an appointment-booking site may need more frequent checks than a brochure site with a few pages. Busy online stores should have a maintenance plan suited to their transactions and customer activity.
Add a recurring calendar reminder. Keep a checklist somewhere you can find it again. A routine is more useful when it survives a busy week.
Monthly check: update WordPress carefully
WordPress, themes, and plugins receive updates that can fix problems and improve compatibility. Sign in to your dashboard and review Dashboard > Updates.
Before updating, make sure you have a current, restorable copy of the site. If available, test changes on a staging copy first. A staging copy is a private version of your site where you can check changes without affecting visitors.
Then:
- Review the available WordPress, theme, and plugin updates.
- Check the update notes for important compatibility information.
- Update components carefully, especially when several changes are pending.
- Visit the live site and test the features customers use.
If your site has custom features or handles important business tasks, avoid clicking every update at once and walking away. Check the WordPress update guidance for additional help.
Install important security updates promptly, rather than waiting for your next calendar reminder. If an update causes an error or you are unsure about compatibility, pause and contact your developer or host.
Remove plugins and themes you no longer need
Unused software can clutter your dashboard and make maintenance harder. During your monthly review, look at your installed plugins and themes.
Ask what each item does and whether your site still needs it. A deactivated plugin is still installed, so remove it if you are certain it is unnecessary. Don’t delete anything simply because its name looks unfamiliar. It may support a feature your site relies on.
Before removal, check whether the item is active or connected to a page, form, or other function. If you are unsure, ask the person who manages your website.
Keeping only what you need makes the site easier to understand and maintain. Decluttering is useful; guessing is not.
Test your forms, not just your homepage
A homepage that loads correctly does not prove every important feature works. Test the forms customers rely on, such as contact, quote, appointment, or newsletter forms.
Submit a test with the required information. Confirm the success message appears, and check that the submission reaches the intended recipient or storage location. If the form includes a confirmation email, check that too.
Where practical, test on a phone as well as a computer. Look for problems such as fields that are hard to tap, unclear instructions, or buttons that do nothing.
If you collect payments or bookings, test those processes according to your provider’s safe testing instructions. Don’t make a real purchase just to see whether a button works.
Check that your backups can restore the site
A backup is only helpful if you can restore it. This check is different from confirming that a backup job ran.
Ask your host or developer how restoration is tested. The safest approach is usually to restore a copy in a staging environment, then check that it loads and works.
On that restored copy, confirm that key pages appear, you can sign in, and important forms behave as expected. For a store or booking site, ask your provider how to test those features without affecting real customer activity.
If you manage this yourself, make sure you understand the restoration steps before an emergency. The WordPress maintenance guide offers broader maintenance advice. Don’t wait until something breaks to discover the recovery process.
Review website users and access
Staff, contractors, and former team members may have accounts on your website. Review the user list regularly and check whether each person still needs access.
Remove accounts that are no longer needed, or reduce their permissions when full access is unnecessary. WordPress provides different user roles, so a person who only edits content may not need administrator privileges.
Use individual accounts rather than sharing one login across a team. That makes it easier to know who has access and to update permissions when responsibilities change.
If you find an account you cannot identify, don’t assume it is harmless. Ask your developer or host to review it with you.
Find broken links and missing pages
Links can stop working when pages move, services change, or old content gets removed. Review important navigation links and pages customers visit most.
Try links from your homepage, service pages, contact page, and footer. Check downloadable files, images, and links to outside websites as well. Look for error pages, missing files, or links that lead somewhere unexpected.
A broken link checker can help flag possible issues, but review the results before making changes. Some flagged links may be intentional, and automated tools can miss context.
Fix or replace links that matter to visitors. When a page has moved, a suitable redirect may help people reach its new location. If redirects are unfamiliar, ask a professional rather than experimenting on a live site.
Give content a quarterly review
Your website should reflect the business you run today, not the business you ran several seasons ago. Use a quarterly review to check service descriptions, staff information, hours, prices, images, and contact details.
Update copyright dates when appropriate, but don’t stop there. Review the actual content for old offers, outdated policies, retired services, and links to former staff or locations.
Ask yourself: would a new customer know what you do, who you serve, and how to contact you? If the answer is unclear, improve the wording.
You do not need to rewrite every page. A small, accurate correction is better than leaving stale information in place.
Use Site Health as a helpful clue
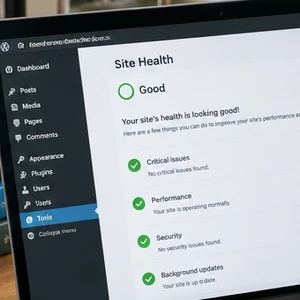
WordPress includes a Site Health screen under Tools. It reports certain technical issues and recommendations that may need attention.
Review the findings, but don’t treat every notice as an emergency. Some recommendations require technical knowledge or depend on how your site is built. The WordPress Site Health documentation explains what the screen shows.
Start with items marked critical, then discuss other concerns with your developer or host. Site Health is useful, but it does not replace testing your own pages, forms, and customer journeys.
Keep a short maintenance log
After each review, note what you checked, what you updated, and anything that needs follow-up. A simple document or spreadsheet is enough.
For example, record that you tested the contact form, removed an old staff account, or noticed a broken link awaiting review. These notes prevent repeat work and help a professional understand what has already happened.
A log also gives your routine a clear finish line. When the checklist is complete, you can get back to running your business.
You can hand maintenance to a professional
Doing the checks yourself can work well when your site is straightforward and you feel comfortable in the dashboard. If updates or troubleshooting feel stressful, handing maintenance to a professional is a reasonable choice.
The CharlesWorks Corner has served website and hosting clients since 1998 from New Hampshire. We believe support should feel personal, with access to real people who can explain the work clearly.
You can learn more about WordPress and website development or visit cwcorner.com to get in touch.
A website maintenance routine does not need to be complicated. Review updates, test the important features, remove what you no longer use, and keep your content current. Consistency beats a heroic cleanup after everything has been ignored.


by Charles Oropallo | Aug 20, 2025 | Security, Technical Help, The CW Corner, Website Development, Website Updates
 Let’s be honest, you didn’t start your business to become a cybersecurity expert. You’ve got products to sell, customers to serve, and a bottom line to protect. But here’s the thing: spending hours wrestling with complicated security tutorials isn’t the answer.
The good news? Website security doesn’t have to eat up your entire weekend. With these seven practical hacks, you can lock down your site without needing a computer science degree. These aren’t theoretical tips, they’re battle-tested strategies that take minutes to implement but provide months of protection.
Think of this as your security cheat sheet. No fluff, no technical jargon, just straight-forward steps that actually work.
1. Turn On Multi-Factor Authentication (MFA) Everywhere
Here’s your first quick win: enable multi-factor authentication on every account that touches your business. This means requiring two forms of identification, like your password plus a code sent to your phone, before anyone can access your systems.
Why does this matter? Even if hackers crack your password, they still can’t get in without that second verification step. It’s like having a deadbolt and a security chain on your front door.
Set this up on your website admin panel, email accounts, social media profiles, and any business applications you use. Most platforms make this incredibly easy, usually just a toggle switch in your security settings.
Don’t skip this step because it seems like a hassle. The extra 30 seconds during login is nothing compared to the weeks you’d spend recovering from a breach.
2. Get That SSL Certificate Installed (And Keep It Updated)
If your website URL doesn’t start with “https://”, you’re broadcasting to the world that your site isn’t secure. Visitors see those dreaded “Not Secure” warnings, search engines penalize your rankings, and hackers see an easy target.
An SSL certificate encrypts data between your website and visitors. It’s like putting your conversation in a locked briefcase instead of shouting it across a crowded room.
Most hosting providers offer SSL certificates for free or under $20 per year. If you’re not sure whether yours is installed correctly, just look at your address bar. You should see a little lock icon next to your domain name.
Pro tip: Set a calendar reminder to check your SSL certificate renewal date. An expired certificate means your site goes back to showing security warnings, not exactly the professional image you want.
3. Schedule Monthly 15-Minute Security Checkups
Here’s where most business owners go wrong: they set up security once and forget about it. That’s like installing smoke detectors and never checking the batteries.
Instead, block out 15 minutes each month for a quick security review. During this time, scan for suspicious login attempts, check for broken or modified pages, and verify your backups are working.
You don’t need fancy tools for this. Most content management systems have built-in activity logs that show recent changes and user logins. Look for anything unusual, logins from strange locations, files you didn’t create, or pages that suddenly load slowly.
Think of this as preventive maintenance for your digital storefront. Catching problems early means fixing them takes minutes instead of days.
4. Enable Automatic Updates (Yes, Really)
“But what if an update breaks my site?” This fear keeps many business owners running outdated, vulnerable software. Here’s the reality: the risk of a hacker exploiting an old security hole far outweighs the small chance an update causes problems.
Software updates aren’t just about new features, they’re about patching security vulnerabilities that hackers actively target. Running outdated software is like leaving your keys in an unlocked car.
Enable automatic updates for your website’s core software, plugins, and themes. If your platform doesn’t support automatic updates, set weekly calendar reminders to install them manually.
Still worried about updates breaking things? That’s what backups are for (more on that in tip #6). The peace of mind from staying current on security patches is worth the occasional minor glitch.
5. Implement a Real Password Policy
“Password123!” doesn’t count as secure, no matter how many exclamation points you add. Weak passwords are like having a “Welcome” mat for hackers.
Create a simple password policy for your team: minimum 12 characters, mix of letters/numbers/symbols, and no reusing passwords across accounts. Better yet, use a password manager to generate and store complex passwords automatically.
Think about what’s connected to your email accounts, your website admin panel, and your business applications. One compromised password can unlock everything. Don’t make it easy for the bad guys.
If remembering complex passwords feels overwhelming, password managers like Bitwarden or LastPass do the heavy lifting. They generate random passwords and fill them in automatically, security made simple.
6. Set Up Automatic Backups and Vulnerability Scanning
Imagine losing months of work because your website got hacked or your server crashed. Now imagine getting everything back with the click of a button. That’s the power of automatic backups.
Configure daily backups of your entire website: files, database, everything. Store these backups off-site, not on the same server as your website. Many hosting providers include this service, or you can use plugins that backup to cloud storage.
Pair this with vulnerability scanning. Services like Sucuri or Wordfence automatically check your site for malware, outdated software, and security holes. They send email alerts when they find problems, so you can fix issues before hackers exploit them.
The goal isn’t to never have problems: it’s to bounce back quickly when they happen. Automatic backups and scanning give you that resilience without ongoing effort.
7. Audit Your Plugins and Third-Party Tools
Your website is only as secure as its weakest link. That forgotten plugin you installed two years ago might be full of security holes, giving hackers a backdoor into your site.
Conduct a quarterly audit of every plugin, integration, and third-party tool connected to your website. Ask yourself: “Do I actually use this? Is it from a reputable developer? When was it last updated?”
Delete anything you don’t actively use. For the tools you keep, enable security notifications so you know about vulnerabilities immediately. Subscribe to security blogs or newsletters from your plugin developers.
This includes seemingly harmless additions like social media widgets, analytics tools, and contact forms. Each one represents a potential entry point. The fewer doors you have, the fewer you need to guard.
The Bottom Line: Security as a Business Habit
These seven hacks work because they create multiple layers of protection without requiring constant attention. You’re not trying to become a security expert: you’re building good habits that run on autopilot.
The key is treating security like any other business routine. You wouldn’t skip payroll or forget to pay rent. Website security deserves the same consistent attention.
Start with multi-factor authentication and SSL certificates: these give you the biggest security boost for the least effort. Then work through the other tips over the next few weeks.
Your future self will thank you when you’re running a secure, professional website instead of dealing with the aftermath of a security breach. And your customers will appreciate knowing their information is safe in your hands.
Need help implementing any of these security measures? Our team at The CharlesWorks Corner specializes in making website security simple and manageable for busy business owners. Don’t let security concerns keep you up at night when practical solutions are just a click away.
by Charles Oropallo | Jun 30, 2022 | Do-It-Yourself, Email, Internet, Passwords, Security, The CW Corner, Website Updates, WordPress
We at CharlesWorks are often asked by our web clients if their site is protected from malware and getting hacked. They also want to know if there site IS hacked, whether there be a charge to fix it.
The totally hack-proof website
The totally hack proof website has no access to it. So it’s not connected to the Internet. No one can view it. Such a website doesn’t sound like its of much use if no one can see it.
So, let’s agree that it is unrealistic to believe that a publicly accessible website can be totally hack-proof. Any website that is accessible via the public Internet is consistently subjected to attempts to break into it. Believe it or not, that’s the norm as opposed to the anomaly.
That being said, however, there ARE things you can do to mitigate website hacks. I have to stress the word mitigate here. Mitigation is defined as the action of reducing the severity, seriousness, or painfulness of something.
Site hacks are based on odds
My goal here is to simply remind you of what you most likely already know: that we can reduce the probability – the odds – of your site being hacked. We at CharlesWorks want that probability to be so low that it hopefully it doesn’t ever happen to you.
The major hacking causes
I have been operating CharlesWorks since 1998. In my experience, there appear to be two major reasons why sites get hacked:
-
- The access credentials/passwords have been compromised.
- The software that operates them wasn’t kept up to date.
Lets take a look at each of these below.
Compromised Access Credentials
Compromised passwords and bad actors gaining access to website login credentials is the major reason we see sites hacked. Think about this in terms of your car. You could have alarms on it. But if you make a copy of your car key and give it to someone, they can do whatever they like with the car. Whether its a drive along the beach or to rob a bank, your car is theirs to use with the key you gave them. Credentials – log in and passwords – work pretty much the same way.
CharlesWorks has many clients who want to be able to do things themselves. We are strong proponents of doing it yourself when it’s feasible and convenient. This is especially true for adding posts or page materials. It also makes sense when making other changes or modifications to your site. It is, after all, YOUR website.
However, many people fall prey to phishing schemes. Directly or indirectly, they usually end up tricked into giving out their website access credentials (as well as credentials to everything else they own). This is especially true if your email account is hacked and the hackers are able to access emails containing your website’s (and other) login credentials.
This problem is exacerbated if you have shared your website’s administrative or other access with others. Think of your emails containing various authorizations or login information as a potential weak link in a chain. If you have shared that information with others you have now created more weak links. This increases the odds of a potential compromise.
One of the best ways to mitigate these situations is to change your site’s access passwords so they are different than those possibly stored in your emails. And, to hope that anyone you may have shared your website access with has done the same.
Obviously, should site access be gained in such a manner, it would be your burden to have the site restored. I’ll expound upon this a little more at the end of this article.
Out of Date Security/Software Updates
Malware and virus protection on home computers operates a little differently than the same types of protection on servers. Website servers operate in the publicly accessible Internet. This results in many more entry points for potential issues. There are a number of very standard server protections available (which we utilize here at CharlesWorks).
After bad actors getting (or guessing) your passwords, the next major reason sites get hacked surrounds unapplied security updates and other software update issues. At CharlesWorks we mitigate such issues by running anti-malware software on our servers. Also, WordPress sites hosted on our servers are kept up to date automatically via automatic updating of the WordPress core as well as automatic updating of the the website’s plugins and themes.
There are literally thousands of individual pieces of software that must work in unison to operate most websites. These are developed by many more thousands of developers around the world. Unfortunately, no company can guarantee that a website will never get hacked. They can only mitigate security compromises and hope against the worst.
Restoring your Website
Regardless of which of the two situations above may have led to your website’s issues, your website will most likely need to be restored. That’s because after a bad actor or a hack back doors into the site will most likely have been installed for the bad actors to gain access again.
Many Internet companies claim to have automatic backups. In most of those, those backups are accessible to the user in their account. If the account is hacked, how safe do you suppose that is?
Some Internet companies delete and account upon a website being hacked. In those cases I have seen many left with no website or backup as a result.
What I believe is most important regarding this topic is the manner in which our WordPress sites are backed up every day for 30 days. Our backups are made to separate servers – external to those your the site operates on. For security reasons, the site administrators do not have access to these backups. So even with a site administrator’s compromised passwords there is no access to the backups. With these backups we can usually restore an average site in about 10-30 minutes if it needs restoring. And we can go back as far back as 30 days. We would only bill our web client for the 10-30 minutes (again – for an average website) which results in only a minor charge to restore it. Note that some websites are extremely large and require much more time to restore but these are very rare).
In my experience running CharlesWorks since 1998, we’ve built and handled more than 5,000 websites. At this point in time, I do not recall the last time a website we built and totally maintained was hacked (unfortunately I recall several instances of sites maintained by others that failed to ensure the site was updated and/or had their passwords compromised).
Sites getting hacked for out of date software happens far less frequently (if at all) when security updates are kept up to date and bad actors are kept out.
I hope this helps you understand a little more about this topic.
by Charles Oropallo | Jul 4, 2021 | Do-It-Yourself, Security, The CW Corner, Website Development, Website Updates
Here we are at the 4th of July of 2021 already! The loss of life suffered in 2020 was horrendous. Yet there are people who still do not think in terms of helping their fellow citizens – and themselves – by being vaccinated. The vaccine misinformation mills are in full production.
So think about this: Exactly who benefits when we don’t vaccinate? When more of us are ill and can’t work, the economy suffers. There is no way the government wants that. They want us to all work so they can collect taxes from our labor. Enemies of America benefit when we don’t vaccinate. Who benefits when we do? We all benefit. The economy will return to normal – as will our lives.
At CharlesWorks we all chose to be vaccinated. Each of us employed here cares about ourselves and our clients. So when you make an appointment with us in person you can at least rest assured we have taken steps indicating we care about you.
The CharlesWorks policy is that the COVID unvaccinated need not apply. That is one of the many ways we show we care about others.
Vaccination will help us return to normalcy. It is a small thing to do. It is the patriotic thing to do. It is the right thing to do.
by Charles Oropallo | Nov 12, 2020 | Do-It-Yourself, Technical Help, The CW Corner, Website Development, Website Updates, WordPress
Sometimes in a WordPress website an issue develops where when loading images into media library, only a blank thumbnail shows. It appears a space is created in the database for the picture but there is no content in it.
After testing compatibility of plugins, themes, php, etc., the problem persisted.
To resolve this, one can navigate here logged into WordPress as an administrator:
Go to Dashboard > Settings > Media
Make sure the correct default file path is showing there. When troubleshooting this issue on a site that was unable to upload media files, the file path was shown as:
/home/username/domains/thedomainname.com/private_html/wp-content/uploads
Note that the “username” and “thedomainname.com” in the above and below path examples will be the Linux username and the actual site domain name respectively that you are troubleshooting.
The fix
When this path was removed, the image file upload worked normally again and the problem appeared to be solved.
Possible Reasoning or Causes
In the DirectAdmin path structure, there are two places the website’s servable coding (like WordPress or HTML sites or Joomla, etc.) might be stored:
/home/username/domains/thedomainname.com/public_html
or
/home/username/domains/thedomainname.com/private_html
The “public_html” folder is where DirectAdmin normally places the website’s code (again, referring to all the files and programs that make up the actual WordPress or HTML or Joomla site’s coding, etc.).
The “private_html” folder is where DirectAdmin normally tries to place the website’s code when its content is encrypted. That’s why there is an option in DirectAdmin’s site control panel that allows one to “Use a symbolic link from private_html to public_html”. This option allows for using the same data in http and https.
The suspicion here is that a setting got changed or an update occurred causing the WordPress system to use the private_html setting when the site resides in public_html. Removing the file path from the settings forced WordPress to use where the system actually defaulted to – which cleared the problem.
We may never know how the setting actually got bunged up, but it is an easy fix once it is.
by Charles Oropallo | Aug 5, 2020 | Do-It-Yourself, Internet, Monadnock Shopper News, Shopper News, The CW Corner, Website Development, Website Updates, WordPress
Something many folks overlook is occasionally checking their website’s functionality. I recommend doing this every couple weeks, but at minimum once a month.
Most websites and the servers they are on are subjected to ongoing software updates. Unless you are paying an additional fee for maintenance checks, it’s normal for things to occasionally break due to updates.
Most website owners are not paying additional fees for such maintenance. This means you really need to take the time to check:
– that the site appears to work properly
– that your hours of operation are correct
– that any website forms are working
– that email addresses are correct
The site operation and forms are most susceptible to software updates. If you have a good web developer, the fixes will happen quickly and it will not cost you too much.
Website maintenance should be thought of like automotive maintenance. We get oil changes. We get inspections. We even make modifications and do repairs to keep our vehicle operating the way we want. And our older vehicles can cost more to upkeep – just like older websites. As websites age, more work needs to be done to keep them secure and working as originally intended.
So check your site every now and then to keep things working and have the correct information out there!





 European Union General Data Protection Regulation Compliant