by Charles Oropallo | Nov 20, 2026 | Small Business, Technical Help, The CW Corner, Website Development
 Hiring a web developeriring a web developer often happens when you are already in a hurry. A website may be down, a previous provider may have disappeared, or a needed change may be overdue.
That first conversation matters. The questions you ask can reveal how the developer works, who controls your website, and what happens when something goes wrong.
Price and timeline are worth discussing, but they only tell part of the story. Here are questions that can help you understand the working relationship before you commit.
Ask how the work gets done
“Who will actually work on my website?”
You may speak with one person during the sales call, then discover someone else is doing the work. That arrangement can be perfectly reasonable, but you should know about it first.
A good answer identifies the people or roles involved and explains how you will communicate with them. If the developer uses subcontractors, ask who manages the work and who is responsible for the result.
You are not asking to inspect an organization chart. You are making sure you know who has access to your site and who can answer your questions.
“What will you need from me, and when?”
A website project often needs your content, images, business details, and feedback. Delays can happen when the developer is waiting for something you did not know you needed to provide.
A helpful answer explains what materials are needed, when they are due, and how approvals will work. They should also be willing to help clarify what you need to prepare.
For example, a service page may require a description of your work, contact details, and a photo. Knowing that early makes the project easier for everyone.
“What would you change about my current site, and why?”
This question reveals whether the developer has looked closely at your website. A useful answer points to a specific issue and explains how it affects visitors or your business.
Perhaps a contact form is hard to find, or important information is difficult to read on a phone. A thoughtful developer should explain the concern without making you feel foolish about the site you already have.
Be cautious if every answer is simply, “You need a complete rebuild.” Ask what can be improved, what should stay, and why.
Ask who controls the important things
“Who owns the website files, domain, and hosting account?”
Your domain is your web address. Hosting is the service where your website lives. The website files and content are separate pieces, too.
Ask whose name and account details appear on the domain registration and hosting account. Ideally, your business controls these accounts, while the developer receives appropriate access to do their work.
A clear answer should also explain how you can sign in, recover access, and see renewal notices. For more background, read Do YOU own your website? and Who owns your domain?.
“Could I move the site to another host or developer?”
You may stay with the same developer for years. Still, you should understand your options if your needs change or the relationship ends.
A reassuring answer describes what can be transferred, what files or access you would receive, and whether any software or services require separate licences. Some website platforms have limits, so ask about those before signing up.
The answer should not make leaving sound like a punishment. If you want to understand the process, see what moving your website to a new host involves.
“Can I talk to two current clients?”
References can help you learn how the developer communicates after the contract is signed. Ask for clients whose projects resemble yours, if possible.
A good developer should explain whether references are available and respect their clients’ privacy. If you speak with someone, ask whether the work matched expectations and how problems or extra costs were handled.
Client references are not the only way to judge a provider. But a real conversation can tell you more than a polished sales page.
Ask what support and pricing really mean
“How do I reach you if the site is down at 8 a.m. on a Saturday?”
This question is not a demand for round-the-clock service. It asks how support works and what the developer considers urgent.
A useful answer explains the available contact methods, normal business hours, and how urgent problems are handled. Ask what counts as an emergency. A broken payment or appointment form may matter more than a minor spacing issue.
The developer should not promise instant help unless they can explain what that commitment includes. Clear expectations now are much better than guessing during an outage.
“What is included in the monthly or hourly rate?”
A monthly fee might cover hosting, updates, backups, support, or a set amount of maintenance. An hourly rate might apply only when you request changes.
Ask what is included, what costs extra, and whether third-party services have separate charges. Request examples, such as adding a staff photo or fixing a contact form.
A good answer separates routine service from additional work. It should also explain how you will approve extra costs before the work begins.
“How do you bill for small jobs?”
A small edit can take less time than a full hour. Ask whether the developer bills by the minute, in partial hours, or with a minimum charge.
A clear response explains the billing unit and how work is recorded. If there is a minimum fee, ask when it applies.
You do not need to haggle over every small change. You do need to understand how the invoice is calculated. The older developer checklist also discusses billing practices.
“Are backups and software updates part of the arrangement?”
Ask what gets backed up, where copies are kept, and who can access them. Find out whether backups include both the website files and its database.
Also ask who handles updates and what happens if an update causes a problem. A good answer describes the routine and explains how restoration works.
A backup is more useful when it can be restored. Learn more in what website backups cover, and what they do not. For ongoing care, see a website maintenance routine you will actually keep.
Notice how they answer
A red flag is not always proof of bad intent. It is a reason to pause and ask for a clearer explanation.
Be cautious if a developer:
- Refuses to put the domain or hosting account in your business’s name.
- Will not provide a written scope or quote.
- Has no phone number or clear way to reach a real person.
- Pressures you to sign a long contract before answering basic questions.
- Gives vague answers about who will do the work.
- Says, “We’ll handle all that,” but will not explain what that means.
- Offers a price far below other proposals without explaining what is included.
A very low price may leave out important work, support, or maintenance. Compare what each proposal actually covers, not just the total.
Make the conversation easier to compare
Before calling, write a one-page brief. Include what your business does, what you want the website to accomplish, what is currently frustrating, and any important features.
Talk to two or three developers and ask each the same questions. That makes it easier to compare their answers, not just their personalities or prices.
Then ask for the scope and price in writing. The scope should explain what the developer will do, what you need to provide, and what costs extra. Keep the written agreement somewhere you can find it later.
You can also begin with one small paid job before handing over the whole site. For instance, ask the developer to review a form or make a specific update. Notice how they communicate, explain the work, and handle billing.
If you are replacing someone, do not cancel the old arrangement immediately. First, make sure the new person has the needed files and domain access. Confirm that a backup exists and has been tested. Otherwise, you could lose access before the transition is ready.
Choose someone whose answers you can rely on
The goal is not to find the cheapest developer or the fastest promise. It is to find someone whose answers you can hold them to later.
Good questions do not make you difficult. They help both sides understand the work and avoid preventable surprises. A developer who welcomes these questions is usually the right kind.


by Charles Oropallo | Nov 17, 2026 | Security, Technical Help, The CW Corner, Website Development
A website hacked warning can turn an ordinary workday into a stressful one. Take a breath: a hacked site is a fixable problem, not the end of your business. Don’t delete the site or wipe everything in a panic. First, preserve what you have, then work through recovery in order.
How you might discover a hack
Sometimes Google shows a warning beside your website in search results. Your hosting provider might email you about suspicious activity. Or a customer might say your site sent them somewhere unexpected.
Other clues can be less obvious: unfamiliar administrator accounts or files, pages you never wrote appearing in search results, or a site that suddenly feels slow. Some hacks are silent. You may hear about the problem from someone else before noticing anything yourself.
Google’s guide, How do I know if my site was hacked?, explains that harmful changes can be hidden from site owners. So, a normal-looking homepage is not proof that every page is clean.
Step 1: Take a snapshot before changing anything
Before you start cleanup, ask your host or developer to save a full copy of the website files and a separate copy of the database. The database holds your posts, pages, settings, and other site information.
Write down the exact date and time of the snapshot. Keep this copy separate from the live site, and label it clearly as a snapshot of the site as found. Do not treat it as a clean backup.
Why bother keeping a copy of a compromised site? It can help show what changed and when. It may also help a technician identify how someone got in. A backup created after the break-in can carry the problem forward, so don’t restore it as if it were known-good.
For more on what backups contain, read What Website Backups Actually Cover (and What They Don’t).
Step 2: Close the way in
Once the snapshot is safely kept, change the passwords connected to site access. This includes your hosting control panel, WordPress administrator accounts, file transfer accounts, and database.
File Transfer Protocol (FTP) and Secure File Transfer Protocol (SFTP) are methods for accessing website files. If you use either, change its password too. Coordinate the database password change with your host or developer, since the website may need updated settings to connect afterward.
Sign out active sessions where you can. Review the list of WordPress administrators and hosting file transfer accounts. Remove any account you do not recognize, but record its details first.
Make password changes from a clean, trusted device. If an account or computer may also be compromised, ask a qualified technician for help before entering new credentials.
Step 3: Find the entry point honestly
Cleanup is not complete if the way in remains open. Common causes include outdated WordPress software, plugins, or themes; weak or reused passwords; and stolen logins from a phishing page or infected computer.
A compromised account on shared hosting can also create problems for neighboring sites. Your provider can help investigate whether the hosting environment is involved.
Look for evidence with your host or developer. That may include unfamiliar accounts, unexpected files, unusual site changes, or activity in available logs. A log is a record of events on your website or server.
Don’t settle for removing the strange page you can see. The visible symptom may be only one sign of a deeper problem. Our older article, Best Practices for Mitigating Website Hacks, covers ways to reduce the risk of another incident.
Step 4: Choose between a clean restore and cleanup
The right recovery method depends on what happened and what backups are available. If you have a verified, known-good backup from before the intrusion, restoring it may be the clearest route.
But first, close the entry point. Restoring an old copy without fixing the cause can simply reopen the same hole. Check that the backup is trustworthy and does not include the attacker’s changes.
If no suitable backup exists, a qualified professional may need to clean the site in place. This means inspecting and repairing the files and database that make up the current site. Malware can hide in places a basic scan misses, and injected content may live in the database, not just website files.
Google’s Security issues report guidance also recommends fixing the issue throughout the site, not just on example pages. If the work is beyond your comfort level, get help. Guessing at unfamiliar code can make recovery harder.
Step 5: Request removal of Google warnings
After the site has been cleaned or safely restored, check Google Search Console’s Security issues report. It may identify examples of affected pages and explain what Google detected.
Fix all the listed issues, then request a review through the report. Describe what you found and what you changed. Google needs to review the site before removing its warning.
A website that looks normal to you may still have a warning in Google results or browsers. The warning will not necessarily disappear just because the site appears fine now. Google’s review process can take time, so check the report for updates.
If you need an introduction, see our guide to Google Search Console.
Step 6: Tell customers plainly
If customers may have seen redirects, suspicious pages, or a browser warning, send a short, honest note. Silence can leave people confused and make them wonder whether you know about the problem.
For example:
We recently discovered unauthorized changes to our website. We have secured the site and are investigating how the changes occurred. If you visited during this period and entered information, please contact us using the details below. We’ll share relevant updates as we learn more.
Adjust this wording to match what you know. Don’t claim customer information was exposed unless that has been established. Don’t blame an unnamed “third party” as a way to dodge responsibility. Be clear about what happened, what you did, and what customers should do.
Step 7: Report the incident where it matters
Tell your hosting provider about the intrusion. Share relevant details and ask whether they see activity affecting your account or hosting environment. Depending on what happened, you may also need to contact your payment provider, insurer, or other relevant reporting channels.
If customer data or payment details might have been exposed, this becomes a different conversation. Notification and legal duties can depend on the information, location, and circumstances involved. Get qualified legal advice rather than guessing about what you must do.
Step 8: Reduce the chance of a repeat
Once recovery is underway, keep future care practical and manageable. Keep WordPress, plugins, and themes updated. Use unique, strong passwords and two-factor authentication (2FA) for administrator access.
Remove plugins and themes you no longer use. Keep regular backups in a separate location, and test a restore before an emergency. For more prevention guidance, see our article on mitigating website hacks.
The business cost of a hack
A hack can cost more than cleanup time. Customers may hesitate to visit or submit a form. Search warnings can interrupt new enquiries, and your staff may spend valuable hours answering questions instead of serving customers.
That is why the awkward customer email is often cheaper than silence. A clear update gives people a reason to trust your next message. A site you cannot restore to a known-good state can also cost far more than a sensible backup routine.
Recovery is easier when you know who to call, where your backups live, and what they include. Ask your host or developer those questions before a crisis, not while one is unfolding.
Work through the steps, and ask for help
A website hack is upsetting, but you do not have to solve everything at once. Preserve a snapshot, close the way in, investigate the cause, and choose a careful cleanup or restore.
Write down what you do and when. Get help early rather than guessing, especially if you cannot confirm the site is clean. A calm, documented recovery is a much better plan than a rushed wipe.
by Charles Oropallo | Oct 31, 2026 | Do-It-Yourself, Small Business, Technical Help, The CW Corner, Website Development, Website Updates
 A website maintenance routine should be simple, scheduled, and focused on the features your customers depend on. Backups matter, but they are only one part of caring for a website.
A few repeatable checks can help catch problems before a customer does. Think of your site like a storefront: you keep the doors working, remove clutter, and make sure the information inside is current.
You do not need to become a web professional to follow a basic routine. Set aside time regularly, keep notes, and ask for help when a change feels risky.
Start with a manageable schedule
For many small-business websites, a monthly check-in and a more thorough quarterly review provide a useful starting point. Adjust the schedule to match how often your site changes and how important its features are to daily business.
For example, an appointment-booking site may need more frequent checks than a brochure site with a few pages. Busy online stores should have a maintenance plan suited to their transactions and customer activity.
Add a recurring calendar reminder. Keep a checklist somewhere you can find it again. A routine is more useful when it survives a busy week.
Monthly check: update WordPress carefully
WordPress, themes, and plugins receive updates that can fix problems and improve compatibility. Sign in to your dashboard and review Dashboard > Updates.
Before updating, make sure you have a current, restorable copy of the site. If available, test changes on a staging copy first. A staging copy is a private version of your site where you can check changes without affecting visitors.
Then:
- Review the available WordPress, theme, and plugin updates.
- Check the update notes for important compatibility information.
- Update components carefully, especially when several changes are pending.
- Visit the live site and test the features customers use.
If your site has custom features or handles important business tasks, avoid clicking every update at once and walking away. Check the WordPress update guidance for additional help.
Install important security updates promptly, rather than waiting for your next calendar reminder. If an update causes an error or you are unsure about compatibility, pause and contact your developer or host.
Remove plugins and themes you no longer need
Unused software can clutter your dashboard and make maintenance harder. During your monthly review, look at your installed plugins and themes.
Ask what each item does and whether your site still needs it. A deactivated plugin is still installed, so remove it if you are certain it is unnecessary. Don’t delete anything simply because its name looks unfamiliar. It may support a feature your site relies on.
Before removal, check whether the item is active or connected to a page, form, or other function. If you are unsure, ask the person who manages your website.
Keeping only what you need makes the site easier to understand and maintain. Decluttering is useful; guessing is not.
Test your forms, not just your homepage
A homepage that loads correctly does not prove every important feature works. Test the forms customers rely on, such as contact, quote, appointment, or newsletter forms.
Submit a test with the required information. Confirm the success message appears, and check that the submission reaches the intended recipient or storage location. If the form includes a confirmation email, check that too.
Where practical, test on a phone as well as a computer. Look for problems such as fields that are hard to tap, unclear instructions, or buttons that do nothing.
If you collect payments or bookings, test those processes according to your provider’s safe testing instructions. Don’t make a real purchase just to see whether a button works.
Check that your backups can restore the site
A backup is only helpful if you can restore it. This check is different from confirming that a backup job ran.
Ask your host or developer how restoration is tested. The safest approach is usually to restore a copy in a staging environment, then check that it loads and works.
On that restored copy, confirm that key pages appear, you can sign in, and important forms behave as expected. For a store or booking site, ask your provider how to test those features without affecting real customer activity.
If you manage this yourself, make sure you understand the restoration steps before an emergency. The WordPress maintenance guide offers broader maintenance advice. Don’t wait until something breaks to discover the recovery process.
Review website users and access
Staff, contractors, and former team members may have accounts on your website. Review the user list regularly and check whether each person still needs access.
Remove accounts that are no longer needed, or reduce their permissions when full access is unnecessary. WordPress provides different user roles, so a person who only edits content may not need administrator privileges.
Use individual accounts rather than sharing one login across a team. That makes it easier to know who has access and to update permissions when responsibilities change.
If you find an account you cannot identify, don’t assume it is harmless. Ask your developer or host to review it with you.
Find broken links and missing pages
Links can stop working when pages move, services change, or old content gets removed. Review important navigation links and pages customers visit most.
Try links from your homepage, service pages, contact page, and footer. Check downloadable files, images, and links to outside websites as well. Look for error pages, missing files, or links that lead somewhere unexpected.
A broken link checker can help flag possible issues, but review the results before making changes. Some flagged links may be intentional, and automated tools can miss context.
Fix or replace links that matter to visitors. When a page has moved, a suitable redirect may help people reach its new location. If redirects are unfamiliar, ask a professional rather than experimenting on a live site.
Give content a quarterly review
Your website should reflect the business you run today, not the business you ran several seasons ago. Use a quarterly review to check service descriptions, staff information, hours, prices, images, and contact details.
Update copyright dates when appropriate, but don’t stop there. Review the actual content for old offers, outdated policies, retired services, and links to former staff or locations.
Ask yourself: would a new customer know what you do, who you serve, and how to contact you? If the answer is unclear, improve the wording.
You do not need to rewrite every page. A small, accurate correction is better than leaving stale information in place.
Use Site Health as a helpful clue
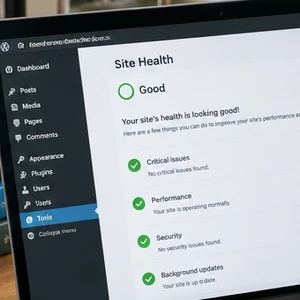
WordPress includes a Site Health screen under Tools. It reports certain technical issues and recommendations that may need attention.
Review the findings, but don’t treat every notice as an emergency. Some recommendations require technical knowledge or depend on how your site is built. The WordPress Site Health documentation explains what the screen shows.
Start with items marked critical, then discuss other concerns with your developer or host. Site Health is useful, but it does not replace testing your own pages, forms, and customer journeys.
Keep a short maintenance log
After each review, note what you checked, what you updated, and anything that needs follow-up. A simple document or spreadsheet is enough.
For example, record that you tested the contact form, removed an old staff account, or noticed a broken link awaiting review. These notes prevent repeat work and help a professional understand what has already happened.
A log also gives your routine a clear finish line. When the checklist is complete, you can get back to running your business.
You can hand maintenance to a professional
Doing the checks yourself can work well when your site is straightforward and you feel comfortable in the dashboard. If updates or troubleshooting feel stressful, handing maintenance to a professional is a reasonable choice.
The CharlesWorks Corner has served website and hosting clients since 1998 from New Hampshire. We believe support should feel personal, with access to real people who can explain the work clearly.
You can learn more about WordPress and website development or visit cwcorner.com to get in touch.
A website maintenance routine does not need to be complicated. Review updates, test the important features, remove what you no longer use, and keep your content current. Consistency beats a heroic cleanup after everything has been ignored.
by Charles Oropallo | Oct 22, 2026 | Technical Help, The CW Corner, Web Hosting, Website Development, WordPress
 PHP updates may seem like a behind-the-scenes detail, but they can affect your WordPress site’s security, speed, and compatibility. If your hosting company has asked you to change PHP versions, it helps to understand why before clicking anything. The good news: with a little preparation, you can make the change carefully.
First, what is PHP?
PHP, short for PHP: Hypertext Preprocessor, is programming software that runs on the web server. WordPress uses PHP to build pages, display posts, process forms, and connect with your database.
Think of WordPress as the blueprint for your site and PHP as the worker following those instructions. Your visitor requests a page, and PHP helps assemble the right content. The server then sends the finished page to the visitor’s browser.
Unlike a photo or document, PHP does its work behind the scenes. You generally won’t see it while browsing your website. But an older PHP version can affect how well the site runs.
Why do PHP versions get retired?
PHP is maintained in numbered versions, or branches. Each branch receives updates for a limited time. Those updates may fix bugs, improve performance, or address security problems.
Eventually, a branch reaches the end of its support period. The PHP project stops providing fixes for it, including security fixes. Hosting companies also need to maintain software that works with their current servers and support tools. So they retire old versions rather than maintain them indefinitely.
That doesn’t necessarily mean your website will stop working on the day support ends. It does mean the version is no longer receiving fixes from the PHP project. Your host may eventually remove it or require you to move to a supported version.
For current support dates, check the official PHP supported versions list. WordPress also publishes its server requirements, including its current PHP guidance. Requirements can change, so use those sources when planning an update.
What can happen if your site uses outdated PHP?
Security fixes stop. When a PHP branch is no longer maintained, new problems found in that branch may not receive PHP project fixes. Keeping the server software supported is an important part of maintaining a website.
Plugins and themes can fall behind. WordPress add-ons are built to work with particular software versions. Over time, plugin and theme developers may stop testing older PHP branches. That can lead to warnings, errors, or features that no longer work as expected.
Performance may suffer. Newer PHP versions can include improvements that help code run more efficiently. An older version may miss those improvements. Speed also depends on other factors, including hosting resources, site design, and plugins, so changing PHP alone isn’t a promise of a faster site.
Think of it like keeping a work computer on software that no longer receives updates. It may keep doing the job today, but it becomes harder to support and maintain.
How to check your current PHP version
You can usually check your version in the WordPress dashboard:
- Sign in to your WordPress site.
- Open Tools, then choose Site Health.
- Select the Info tab and open the Server section.
- Look for the PHP version listed there.
The wording or menu location may vary by WordPress version. Your hosting control panel may also show the version assigned to your website. If you can’t find it, ask your host. They can confirm both your current version and the supported versions available for your account.
Once you know what you’re running, compare it with the current information from PHP and WordPress. Don’t choose a version based on a guess or an old tutorial. Your site’s plugins, theme, and custom code need to support the version you select.
How to prepare for PHP updates safely
A careful update is much less stressful than a rushed one. Here’s a sensible process:
- Check your site’s components. Make a list of WordPress, your active theme, plugins, and any custom code. Check their documentation or contact their developers about compatibility with your planned PHP version.
- Update WordPress, themes, and plugins first. Install available updates on the existing PHP version, after checking what each update changes. Updated software is more likely to support current PHP versions. Remove plugins and themes you no longer use.
- Make a complete, restorable backup. Include both your website files and database. Confirm how to restore it, and keep a copy separate from the live site.
- Test on a staging copy. Staging is a private copy of your live website for testing changes. Switch the staging site to your intended PHP version first. If your host doesn’t provide staging, ask about safe testing options before changing the live site.
- Test the parts that matter. Check the homepage, several important pages, forms, login, and any booking or shopping features. Try the site on a phone, too. Review available error logs for PHP warnings or failures.
- Change the live site when you’re ready. Make a fresh backup first. Use your hosting panel to select the PHP version for the correct site or domain. Panel names and steps vary, so follow your host’s instructions.
- Check the live site again. Clear relevant caches if needed. Test key features and watch for errors after the switch. If you find a problem, contact your host or developer promptly.
If you want a more detailed walkthrough, see our earlier guide, Is Your PHP Update Breaking Your WordPress Site?
Worried an update will break your website?
That concern is understandable. Some older plugins, themes, or custom code may not work with a newer PHP version. The risk is higher when software has been abandoned or has not been tested against current versions.
You can reduce the chance of trouble by checking compatibility, testing on staging, and keeping a restorable backup. Plan the change for a quieter time, and know how to contact your hosting provider if you need help.
If staging reveals a problem, pause before changing the live site. Look for an update or replacement for the incompatible component.
A calm, planned change gives you a better chance of finding and fixing compatibility issues without surprising your visitors.
Keep the version current, and the process manageable
PHP isn’t a setting to change casually, but it shouldn’t be ignored either. Supported versions help your WordPress site stay compatible with maintained software and receive available fixes. Check your version, review your site’s components, and test before making a live change.
Not sure which version your site can use? Contact your hosting provider or web developer before switching. At The CharlesWorks Corner, we help clients with WordPress development, hosting, and ongoing website maintenance.
by Charles Oropallo | Aug 20, 2025 | Security, Technical Help, The CW Corner, Website Development, Website Updates
 Let’s be honest, you didn’t start your business to become a cybersecurity expert. You’ve got products to sell, customers to serve, and a bottom line to protect. But here’s the thing: spending hours wrestling with complicated security tutorials isn’t the answer.
The good news? Website security doesn’t have to eat up your entire weekend. With these seven practical hacks, you can lock down your site without needing a computer science degree. These aren’t theoretical tips, they’re battle-tested strategies that take minutes to implement but provide months of protection.
Think of this as your security cheat sheet. No fluff, no technical jargon, just straight-forward steps that actually work.
1. Turn On Multi-Factor Authentication (MFA) Everywhere
Here’s your first quick win: enable multi-factor authentication on every account that touches your business. This means requiring two forms of identification, like your password plus a code sent to your phone, before anyone can access your systems.
Why does this matter? Even if hackers crack your password, they still can’t get in without that second verification step. It’s like having a deadbolt and a security chain on your front door.
Set this up on your website admin panel, email accounts, social media profiles, and any business applications you use. Most platforms make this incredibly easy, usually just a toggle switch in your security settings.
Don’t skip this step because it seems like a hassle. The extra 30 seconds during login is nothing compared to the weeks you’d spend recovering from a breach.
2. Get That SSL Certificate Installed (And Keep It Updated)
If your website URL doesn’t start with “https://”, you’re broadcasting to the world that your site isn’t secure. Visitors see those dreaded “Not Secure” warnings, search engines penalize your rankings, and hackers see an easy target.
An SSL certificate encrypts data between your website and visitors. It’s like putting your conversation in a locked briefcase instead of shouting it across a crowded room.
Most hosting providers offer SSL certificates for free or under $20 per year. If you’re not sure whether yours is installed correctly, just look at your address bar. You should see a little lock icon next to your domain name.
Pro tip: Set a calendar reminder to check your SSL certificate renewal date. An expired certificate means your site goes back to showing security warnings, not exactly the professional image you want.
3. Schedule Monthly 15-Minute Security Checkups
Here’s where most business owners go wrong: they set up security once and forget about it. That’s like installing smoke detectors and never checking the batteries.
Instead, block out 15 minutes each month for a quick security review. During this time, scan for suspicious login attempts, check for broken or modified pages, and verify your backups are working.
You don’t need fancy tools for this. Most content management systems have built-in activity logs that show recent changes and user logins. Look for anything unusual, logins from strange locations, files you didn’t create, or pages that suddenly load slowly.
Think of this as preventive maintenance for your digital storefront. Catching problems early means fixing them takes minutes instead of days.
4. Enable Automatic Updates (Yes, Really)
“But what if an update breaks my site?” This fear keeps many business owners running outdated, vulnerable software. Here’s the reality: the risk of a hacker exploiting an old security hole far outweighs the small chance an update causes problems.
Software updates aren’t just about new features, they’re about patching security vulnerabilities that hackers actively target. Running outdated software is like leaving your keys in an unlocked car.
Enable automatic updates for your website’s core software, plugins, and themes. If your platform doesn’t support automatic updates, set weekly calendar reminders to install them manually.
Still worried about updates breaking things? That’s what backups are for (more on that in tip #6). The peace of mind from staying current on security patches is worth the occasional minor glitch.
5. Implement a Real Password Policy
“Password123!” doesn’t count as secure, no matter how many exclamation points you add. Weak passwords are like having a “Welcome” mat for hackers.
Create a simple password policy for your team: minimum 12 characters, mix of letters/numbers/symbols, and no reusing passwords across accounts. Better yet, use a password manager to generate and store complex passwords automatically.
Think about what’s connected to your email accounts, your website admin panel, and your business applications. One compromised password can unlock everything. Don’t make it easy for the bad guys.
If remembering complex passwords feels overwhelming, password managers like Bitwarden or LastPass do the heavy lifting. They generate random passwords and fill them in automatically, security made simple.
6. Set Up Automatic Backups and Vulnerability Scanning
Imagine losing months of work because your website got hacked or your server crashed. Now imagine getting everything back with the click of a button. That’s the power of automatic backups.
Configure daily backups of your entire website: files, database, everything. Store these backups off-site, not on the same server as your website. Many hosting providers include this service, or you can use plugins that backup to cloud storage.
Pair this with vulnerability scanning. Services like Sucuri or Wordfence automatically check your site for malware, outdated software, and security holes. They send email alerts when they find problems, so you can fix issues before hackers exploit them.
The goal isn’t to never have problems: it’s to bounce back quickly when they happen. Automatic backups and scanning give you that resilience without ongoing effort.
7. Audit Your Plugins and Third-Party Tools
Your website is only as secure as its weakest link. That forgotten plugin you installed two years ago might be full of security holes, giving hackers a backdoor into your site.
Conduct a quarterly audit of every plugin, integration, and third-party tool connected to your website. Ask yourself: “Do I actually use this? Is it from a reputable developer? When was it last updated?”
Delete anything you don’t actively use. For the tools you keep, enable security notifications so you know about vulnerabilities immediately. Subscribe to security blogs or newsletters from your plugin developers.
This includes seemingly harmless additions like social media widgets, analytics tools, and contact forms. Each one represents a potential entry point. The fewer doors you have, the fewer you need to guard.
The Bottom Line: Security as a Business Habit
These seven hacks work because they create multiple layers of protection without requiring constant attention. You’re not trying to become a security expert: you’re building good habits that run on autopilot.
The key is treating security like any other business routine. You wouldn’t skip payroll or forget to pay rent. Website security deserves the same consistent attention.
Start with multi-factor authentication and SSL certificates: these give you the biggest security boost for the least effort. Then work through the other tips over the next few weeks.
Your future self will thank you when you’re running a secure, professional website instead of dealing with the aftermath of a security breach. And your customers will appreciate knowing their information is safe in your hands.
Need help implementing any of these security measures? Our team at The CharlesWorks Corner specializes in making website security simple and manageable for busy business owners. Don’t let security concerns keep you up at night when practical solutions are just a click away.
by Charles Oropallo | Jul 23, 2025 | Do-It-Yourself, Security, The CW Corner, Website Development, WordPress
WordPress powers over 40% of all websites on the internet. That popularity makes it a prime target for hackers. Every day, thousands of WordPress sites get compromised because owners make simple security mistakes.
The good news? Most of these mistakes are easy to fix. You don’t need to be a security expert to protect your website. You just need to know what you’re doing wrong and how to fix it.
Let’s dive into the seven biggest WordPress security mistakes and their solutions.
Mistake #1: Ignoring Updates (The Silent Site Killer)
Here’s the harsh truth: 97% of WordPress security problems come from plugins. Yet only 30% of WordPress users have auto-updates enabled.
Think about it this way. When developers find a security hole, they release an update to fix it. The longer you wait to update, the more time hackers have to exploit that known weakness.
How to Fix It:
Enable automatic updates for WordPress core, plugins, and themes. Most hosting providers offer this feature in their control panels. If yours doesn’t, consider switching to a managed WordPress host.
Check your plugins weekly. Delete any you’re not using. Inactive plugins can still be exploited by hackers.
Set calendar reminders if auto-updates aren’t available. Manual updates beat no updates every time.
Pro Tip: Create a staging site to test updates before they go live. This prevents your main site from breaking during updates.
Mistake #2: Using Weak Passwords and Predictable Usernames
“admin” with password “password123” isn’t clever. It’s dangerous. 41% of WordPress users still use weak passwords or skip two-factor authentication entirely.
Hackers use bots that test thousands of password combinations per minute. A weak password like “ADMIN123” gets cracked in seconds.
How to Fix It:
Create strong passwords with at least 12 characters. Mix uppercase, lowercase, numbers, and special characters.
Never use “admin” as your username. Choose something unique that doesn’t relate to your business name.
Use a password manager like 1Password or Bitwarden. They generate complex passwords and store them securely.
Change default usernames immediately. If you already have an “admin” account, create a new administrator account with a different username, then delete the old one.
Quick Check: Can you guess your password by looking at your keyboard or personal information? If yes, change it now.
Mistake #3: Skipping Two-Factor Authentication (Your Security Backup Plan)
Passwords alone aren’t enough anymore. Even strong passwords can be compromised through data breaches or phishing attacks.
Two-Factor Authentication (2FA) adds a second layer of protection. Even if hackers get your password, they still need your phone or authentication app to get in.
How to Fix It:
Install a 2FA plugin like Wordfence or Google Authenticator for WordPress.
Set up 2FA for all user accounts, especially administrators and editors.
Use an authenticator app instead of SMS when possible. Apps like Google Authenticator or Authy are more secure than text messages.
Test your 2FA setup regularly. Make sure you can access backup codes if you lose your phone.
Remember: 2FA might seem inconvenient, but it’s much less inconvenient than rebuilding your hacked website.
Mistake #4: Forgetting to Back Up Your Website
“My hosting company handles backups.” Famous last words from website owners who lost everything.
Hosting backups might not include all your files. They might be stored on the same server that gets hacked. Or they might be overwritten before you realize you need them.
How to Fix It:
Set up automated daily backups that include your entire website and database.
Store backups in multiple locations. Use cloud services like Google Drive, Dropbox, or Amazon S3.
Test your backup restoration process monthly. A backup that doesn’t restore is useless.
Keep at least 30 days of backup history. Sometimes you don’t notice problems immediately.
Use plugins like UpdraftPlus or BackWPup for automated scheduling.
Reality Check: When did you last check if your backups actually work? If you can’t answer that, check today.
Mistake #5: Installing Themes and Plugins from Sketchy Sources
Free premium themes and plugins sound tempting. But they often come with hidden malware or backdoors that give hackers access to your site.
Even legitimate-looking themes can contain malicious code that steals user data or redirects visitors to scam sites.
How to Fix It:
Only download themes and plugins from the official WordPress repository or established developers.
Check ratings and reviews before installing anything. Look for recent updates and active support.
Research the developer. Do they have other plugins? A professional website? Good reviews?
Scan new themes and plugins with security tools before activation.
Delete unused plugins immediately. Don’t just deactivate them: remove them completely.
Warning Sign: If a “premium” theme or plugin is offered free on a random website, it’s probably infected with malware.
Mistake #6: Ignoring File Permissions (The Technical Blind Spot)
File permissions control who can access what on your server. Wrong permissions can let hackers read sensitive files or upload malicious code.
Most WordPress users never check their file permissions. They assume their hosting provider set them correctly. That’s a dangerous assumption.
How to Fix It:
Set correct file permissions: 755 for directories and 644 for files.
Never use 777 permissions unless absolutely necessary (and change them back immediately after).
Protect your wp-config.php file with 600 permissions.
Work with your hosting provider to audit permissions if you’re unsure.
Use security plugins that monitor and alert you about permission changes.
Technical Note: If file permissions sound too complex, ask your web developer or hosting support to check them for you.
Mistake #7: No Security Monitoring (Flying Blind)
Many WordPress owners only discover they’ve been hacked when visitors complain or Google flags their site. By then, the damage is done.
Hackers often work silently, stealing data or using your site to attack others. You need active monitoring to catch problems early.
How to Fix It:
Install security monitoring plugins like Wordfence, Sucuri, or iThemes Security.
Set up email alerts for suspicious login attempts, file changes, or malware detection.
Monitor your website traffic for unusual spikes or patterns.
Check your site regularly from different devices and browsers.
Use Google Search Console to monitor for security warnings.
Pro Tip: Set up uptime monitoring to alert you immediately if your site goes down. Services like UptimeRobot offer free basic monitoring.
Taking Action: Your Security Checklist
Security isn’t a one-time task. It’s an ongoing process. Here’s your priority order for fixing these mistakes:
- Enable automatic updates immediately – This fixes your biggest vulnerability right now
- Change weak passwords and usernames – Use a password manager to make this easy
- Set up 2FA on all accounts – Add that crucial second layer of protection
- Configure automated backups – Your safety net for when things go wrong
- Audit your plugins and themes – Remove anything suspicious or unused
- Check file permissions – Get help if this feels too technical
- Install security monitoring – Your early warning system
Don’t try to fix everything at once. Start with automatic updates and work down the list. Each step makes your site significantly more secure.
Remember: The best time to secure your WordPress site was yesterday. The second-best time is right now.
Need help implementing these security measures? Our team specializes in WordPress security and can audit your site for vulnerabilities. Contact us for a security consultation that could save your website from becoming another hacking statistic.





 European Union General Data Protection Regulation Compliant