by Charles Oropallo | Nov 14, 2026 | Do-It-Yourself, Small Business, Technical Help, The CW Corner, Web Hosting, WordPress
 Website backups sound reassuring, but “we have backups” answers a question nobody finished asking. What gets copied? Where does it live? And could it actually restore your site?
Those details are the fine print. Knowing them can help you understand what a backup protects, what it leaves out, and what to ask your host or developer.
What a typical WordPress backup contains
A typical WordPress backup has two parts: the database and the website files. You need both to restore a complete site. WordPress explains the two-part backup in its documentation.
The database: what your site says
The database holds much of your site’s changing information. That includes posts, pages, users, settings, plugin configuration, and comments.
Think of your site as a house. The database is what’s written on the walls: the words, arrangements, and instructions that make the place yours.
The files: what your site uses
The files include WordPress itself, themes, plugins, and uploaded images and documents. Depending on your setup, they may also include other site code and related files.
In the house analogy, the files are the furniture and pictures. They give your content its look and provide the tools that make features work.
Neither half alone gives you your whole site back. Files without the database may leave you with an empty framework. A database without the files may have words and settings, but not the right images, design, or working features.
Ask whether your backups include both parts, saved together as a usable set. The WordPress backup guide explains why files and database data need separate attention.
Where the backup lives matters
A backup copy stored on the same server as your website may disappear with that server. If the server fails or becomes inaccessible, both the site and its nearby copy could be affected.
An off-server copy is stored somewhere separate from the website’s own server. In plain terms, it’s another copy kept elsewhere, rather than a spare tucked beside the original.
Access matters, too. If the backup folder is available through the same account used to administer your site, an intruder with that access might delete or encrypt the copies. That makes the backups less useful when you need them most.
Ask who can reach the copies and how they’re protected. At The CharlesWorks Corner, our arrangement keeps copies on separate servers that site administrators cannot reach. That’s one example of an important detail to understand.
For more background on hosting settings, see what your hosting control panel actually does.
What website backups do not cover
A website backup is not a complete copy of your business or everything connected to your online presence. Here are a few things it may not include:
- Your domain registration. A restored website does not renew or recover the name customers use to find you. See what happens when your domain expires.
- Business email messages. If your mailbox lives outside your website hosting account, website backups may not include its messages.
- Third-party accounts and analytics history. Accounts with outside services, saved reports, or past tracking data may live elsewhere. A site copy may not restore them.
- Tracking setup. Website code or settings that connect a tracking service might be included, but the third-party account and its history are separate questions.
- Social profiles. Your business’s social media pages and their content are not part of a website backup.
- Search rankings, reviews, and reputation. A restore does not bring back lost visibility, customer reviews, or confidence.
- Time and trust. Backups cannot give back the hours spent fixing a partly broken site or the customer trust affected while it was unavailable.
There’s another subtle limitation: a backup cannot contain changes made after that copy was created. If a problem went unnoticed for a while, it may already exist in every copy still available.
And restoring a clean copy does not explain what caused the break. If the cause remains, the same problem may return. A restore can help recover the site, but the underlying issue still needs attention.
Our older note on nightly website backups discusses backup timing. This article focuses on what those copies cover.
Questions to ask your host or developer
Ask for clear answers to these questions. Write them down so you can find them later.
- What gets backed up? Does the copy include both the database and files, or only one?
- How often are copies made? Ask what schedule applies to your particular site.
- How long are copies kept? How far back can you reach?
- How does a restore work? Who performs it, and does it cost extra?
- Where do the copies physically live? Are they stored away from your website’s server?
A vague answer to any of these questions is worth chasing. “It’s backed up” may sound comforting, but you deserve to know what that means in practice.
Why the retention window matters
Retention means how long your provider keeps backup copies before removing or replacing them. That window determines how far back you may be able to go.
If a problem is discovered late, you may need a copy older than the window holds. In that case, every available copy could already include the unwanted change or the hidden problem.
Ask how many days your provider keeps copies, and whether you can access older ones. Don’t assume a particular window without checking.
Test a restore before you need one
A backup that has never been restored is a hope, not a plan. A completed backup job does not, by itself, prove that the copy can rebuild your site.
Ask your host or developer to restore a copy into a separate folder or staging site. A staging site is a private version used for testing, away from your live website.
Check that key pages, images, and features appear as expected. For a site with forms or other important functions, ask how those can be checked safely.
Do this once in a while, not during a crisis. A successful test gives you practical confidence and may reveal gaps while there’s time to address them.
Take a fresh copy before important changes
Some routine changes can create problems, even when they’re sensible. Make sure a fresh backup is available just before a plugin or theme update, adding a new form, giving someone administrator access, or making a major content edit.
You don’t need to turn every small adjustment into a technical production. Just build a quick backup check into the changes that could affect important parts of your site.
Our guide to a website maintenance routine you will actually keep can help you make that check part of regular care.
Keep a simple website inventory
Create a one-page inventory with the basics: where your site is hosted, who your domain registrar is, what backup arrangement is in place, and who to call for help.
Keep a copy offline and share it with one other trusted person. If something goes wrong, your business won’t depend on one person remembering every provider, login, or arrangement.
If you need help understanding your hosting or backup setup, ask your host or developer to walk you through it. There’s no need to know every technical detail. A clear answer about what’s covered is a very good place to start.


by Charles Oropallo | Oct 22, 2026 | Technical Help, The CW Corner, Web Hosting, Website Development, WordPress
 PHP updates may seem like a behind-the-scenes detail, but they can affect your WordPress site’s security, speed, and compatibility. If your hosting company has asked you to change PHP versions, it helps to understand why before clicking anything. The good news: with a little preparation, you can make the change carefully.
First, what is PHP?
PHP, short for PHP: Hypertext Preprocessor, is programming software that runs on the web server. WordPress uses PHP to build pages, display posts, process forms, and connect with your database.
Think of WordPress as the blueprint for your site and PHP as the worker following those instructions. Your visitor requests a page, and PHP helps assemble the right content. The server then sends the finished page to the visitor’s browser.
Unlike a photo or document, PHP does its work behind the scenes. You generally won’t see it while browsing your website. But an older PHP version can affect how well the site runs.
Why do PHP versions get retired?
PHP is maintained in numbered versions, or branches. Each branch receives updates for a limited time. Those updates may fix bugs, improve performance, or address security problems.
Eventually, a branch reaches the end of its support period. The PHP project stops providing fixes for it, including security fixes. Hosting companies also need to maintain software that works with their current servers and support tools. So they retire old versions rather than maintain them indefinitely.
That doesn’t necessarily mean your website will stop working on the day support ends. It does mean the version is no longer receiving fixes from the PHP project. Your host may eventually remove it or require you to move to a supported version.
For current support dates, check the official PHP supported versions list. WordPress also publishes its server requirements, including its current PHP guidance. Requirements can change, so use those sources when planning an update.
What can happen if your site uses outdated PHP?
Security fixes stop. When a PHP branch is no longer maintained, new problems found in that branch may not receive PHP project fixes. Keeping the server software supported is an important part of maintaining a website.
Plugins and themes can fall behind. WordPress add-ons are built to work with particular software versions. Over time, plugin and theme developers may stop testing older PHP branches. That can lead to warnings, errors, or features that no longer work as expected.
Performance may suffer. Newer PHP versions can include improvements that help code run more efficiently. An older version may miss those improvements. Speed also depends on other factors, including hosting resources, site design, and plugins, so changing PHP alone isn’t a promise of a faster site.
Think of it like keeping a work computer on software that no longer receives updates. It may keep doing the job today, but it becomes harder to support and maintain.
How to check your current PHP version
You can usually check your version in the WordPress dashboard:
- Sign in to your WordPress site.
- Open Tools, then choose Site Health.
- Select the Info tab and open the Server section.
- Look for the PHP version listed there.
The wording or menu location may vary by WordPress version. Your hosting control panel may also show the version assigned to your website. If you can’t find it, ask your host. They can confirm both your current version and the supported versions available for your account.
Once you know what you’re running, compare it with the current information from PHP and WordPress. Don’t choose a version based on a guess or an old tutorial. Your site’s plugins, theme, and custom code need to support the version you select.
How to prepare for PHP updates safely
A careful update is much less stressful than a rushed one. Here’s a sensible process:
- Check your site’s components. Make a list of WordPress, your active theme, plugins, and any custom code. Check their documentation or contact their developers about compatibility with your planned PHP version.
- Update WordPress, themes, and plugins first. Install available updates on the existing PHP version, after checking what each update changes. Updated software is more likely to support current PHP versions. Remove plugins and themes you no longer use.
- Make a complete, restorable backup. Include both your website files and database. Confirm how to restore it, and keep a copy separate from the live site.
- Test on a staging copy. Staging is a private copy of your live website for testing changes. Switch the staging site to your intended PHP version first. If your host doesn’t provide staging, ask about safe testing options before changing the live site.
- Test the parts that matter. Check the homepage, several important pages, forms, login, and any booking or shopping features. Try the site on a phone, too. Review available error logs for PHP warnings or failures.
- Change the live site when you’re ready. Make a fresh backup first. Use your hosting panel to select the PHP version for the correct site or domain. Panel names and steps vary, so follow your host’s instructions.
- Check the live site again. Clear relevant caches if needed. Test key features and watch for errors after the switch. If you find a problem, contact your host or developer promptly.
If you want a more detailed walkthrough, see our earlier guide, Is Your PHP Update Breaking Your WordPress Site?
Worried an update will break your website?
That concern is understandable. Some older plugins, themes, or custom code may not work with a newer PHP version. The risk is higher when software has been abandoned or has not been tested against current versions.
You can reduce the chance of trouble by checking compatibility, testing on staging, and keeping a restorable backup. Plan the change for a quieter time, and know how to contact your hosting provider if you need help.
If staging reveals a problem, pause before changing the live site. Look for an update or replacement for the incompatible component.
A calm, planned change gives you a better chance of finding and fixing compatibility issues without surprising your visitors.
Keep the version current, and the process manageable
PHP isn’t a setting to change casually, but it shouldn’t be ignored either. Supported versions help your WordPress site stay compatible with maintained software and receive available fixes. Check your version, review your site’s components, and test before making a live change.
Not sure which version your site can use? Contact your hosting provider or web developer before switching. At The CharlesWorks Corner, we help clients with WordPress development, hosting, and ongoing website maintenance.
by Charles Oropallo | Jul 23, 2025 | Do-It-Yourself, Security, The CW Corner, Website Development, WordPress
 WordPress powers over 40% of all websites on the internet. That popularity makes it a prime target for hackers. Every day, thousands of WordPress sites get compromised because owners make simple security mistakes.
The good news? Most of these mistakes are easy to fix. You don’t need to be a security expert to protect your website. You just need to know what you’re doing wrong and how to fix it.
Let’s dive into the seven biggest WordPress security mistakes and their solutions.
Mistake #1: Ignoring Updates (The Silent Site Killer)
Here’s the harsh truth: 97% of WordPress security problems come from plugins. Yet only 30% of WordPress users have auto-updates enabled.
Think about it this way. When developers find a security hole, they release an update to fix it. The longer you wait to update, the more time hackers have to exploit that known weakness.
How to Fix It:
Enable automatic updates for WordPress core, plugins, and themes. Most hosting providers offer this feature in their control panels. If yours doesn’t, consider switching to a managed WordPress host.
Check your plugins weekly. Delete any you’re not using. Inactive plugins can still be exploited by hackers.
Set calendar reminders if auto-updates aren’t available. Manual updates beat no updates every time.
Pro Tip: Create a staging site to test updates before they go live. This prevents your main site from breaking during updates.
Mistake #2: Using Weak Passwords and Predictable Usernames
“admin” with password “password123” isn’t clever. It’s dangerous. 41% of WordPress users still use weak passwords or skip two-factor authentication entirely.
Hackers use bots that test thousands of password combinations per minute. A weak password like “ADMIN123” gets cracked in seconds.
How to Fix It:
Create strong passwords with at least 12 characters. Mix uppercase, lowercase, numbers, and special characters.
Never use “admin” as your username. Choose something unique that doesn’t relate to your business name.
Use a password manager like 1Password or Bitwarden. They generate complex passwords and store them securely.
Change default usernames immediately. If you already have an “admin” account, create a new administrator account with a different username, then delete the old one.
Quick Check: Can you guess your password by looking at your keyboard or personal information? If yes, change it now.
Mistake #3: Skipping Two-Factor Authentication (Your Security Backup Plan)
Passwords alone aren’t enough anymore. Even strong passwords can be compromised through data breaches or phishing attacks.
Two-Factor Authentication (2FA) adds a second layer of protection. Even if hackers get your password, they still need your phone or authentication app to get in.
How to Fix It:
Install a 2FA plugin like Wordfence or Google Authenticator for WordPress.
Set up 2FA for all user accounts, especially administrators and editors.
Use an authenticator app instead of SMS when possible. Apps like Google Authenticator or Authy are more secure than text messages.
Test your 2FA setup regularly. Make sure you can access backup codes if you lose your phone.
Remember: 2FA might seem inconvenient, but it’s much less inconvenient than rebuilding your hacked website.
Mistake #4: Forgetting to Back Up Your Website
“My hosting company handles backups.” Famous last words from website owners who lost everything.
Hosting backups might not include all your files. They might be stored on the same server that gets hacked. Or they might be overwritten before you realize you need them.
How to Fix It:
Set up automated daily backups that include your entire website and database.
Store backups in multiple locations. Use cloud services like Google Drive, Dropbox, or Amazon S3.
Test your backup restoration process monthly. A backup that doesn’t restore is useless.
Keep at least 30 days of backup history. Sometimes you don’t notice problems immediately.
Use plugins like UpdraftPlus or BackWPup for automated scheduling.
Reality Check: When did you last check if your backups actually work? If you can’t answer that, check today.
Mistake #5: Installing Themes and Plugins from Sketchy Sources
Free premium themes and plugins sound tempting. But they often come with hidden malware or backdoors that give hackers access to your site.
Even legitimate-looking themes can contain malicious code that steals user data or redirects visitors to scam sites.
How to Fix It:
Only download themes and plugins from the official WordPress repository or established developers.
Check ratings and reviews before installing anything. Look for recent updates and active support.
Research the developer. Do they have other plugins? A professional website? Good reviews?
Scan new themes and plugins with security tools before activation.
Delete unused plugins immediately. Don’t just deactivate them: remove them completely.
Warning Sign: If a “premium” theme or plugin is offered free on a random website, it’s probably infected with malware.
Mistake #6: Ignoring File Permissions (The Technical Blind Spot)
File permissions control who can access what on your server. Wrong permissions can let hackers read sensitive files or upload malicious code.
Most WordPress users never check their file permissions. They assume their hosting provider set them correctly. That’s a dangerous assumption.
How to Fix It:
Set correct file permissions: 755 for directories and 644 for files.
Never use 777 permissions unless absolutely necessary (and change them back immediately after).
Protect your wp-config.php file with 600 permissions.
Work with your hosting provider to audit permissions if you’re unsure.
Use security plugins that monitor and alert you about permission changes.
Technical Note: If file permissions sound too complex, ask your web developer or hosting support to check them for you.
Mistake #7: No Security Monitoring (Flying Blind)
Many WordPress owners only discover they’ve been hacked when visitors complain or Google flags their site. By then, the damage is done.
Hackers often work silently, stealing data or using your site to attack others. You need active monitoring to catch problems early.
How to Fix It:
Install security monitoring plugins like Wordfence, Sucuri, or iThemes Security.
Set up email alerts for suspicious login attempts, file changes, or malware detection.
Monitor your website traffic for unusual spikes or patterns.
Check your site regularly from different devices and browsers.
Use Google Search Console to monitor for security warnings.
Pro Tip: Set up uptime monitoring to alert you immediately if your site goes down. Services like UptimeRobot offer free basic monitoring.
Taking Action: Your Security Checklist
Security isn’t a one-time task. It’s an ongoing process. Here’s your priority order for fixing these mistakes:
- Enable automatic updates immediately – This fixes your biggest vulnerability right now
- Change weak passwords and usernames – Use a password manager to make this easy
- Set up 2FA on all accounts – Add that crucial second layer of protection
- Configure automated backups – Your safety net for when things go wrong
- Audit your plugins and themes – Remove anything suspicious or unused
- Check file permissions – Get help if this feels too technical
- Install security monitoring – Your early warning system
Don’t try to fix everything at once. Start with automatic updates and work down the list. Each step makes your site significantly more secure.
Remember: The best time to secure your WordPress site was yesterday. The second-best time is right now.
Need help implementing these security measures? Our team specializes in WordPress security and can audit your site for vulnerabilities. Contact us for a security consultation that could save your website from becoming another hacking statistic.
by Charles Oropallo | Dec 16, 2024 | Do-It-Yourself, Technical Help, The CW Corner, Website Development, WordPress
SimplePractice: Incorporating its Widget into your WordPress Divi Website
This article is about adding the SimplePractice widget to your WordPress website that uses the Divi theme. I’ll explain what SimplePractice is and get into how to install its widget into your WordPress Divi website.
Simplifying Practice Management for Mental Health Professionals
 SimplePractice is a trusted all-in-one platform designed to make life easier for mental health professionals and other wellness practitioners. See https://SimplePractice.com for more details. It streamlines essential administrative tasks like scheduling, billing, documentation, and client communication, allowing practitioners to focus on what truly matters—their clients. With a user-friendly interface and powerful tools, it’s an ideal solution for solo practitioners and small group practices.
One of the standout features is its online scheduling tool, which lets clients book appointments through a secure, HIPAA-compliant client portal. This portal also allows clients to complete intake forms, sign documents, and even message their provider—all in one place. For therapists who offer virtual sessions, the telehealth integration enables seamless video appointments without the need for third-party apps.
SimplePractice also simplifies billing and insurance management. Providers can create invoices, process payments, and submit insurance claims directly through the system. Plus, its customizable progress notes and treatment plan templates make maintaining records both quick and efficient.
What makes SimplePractice shine is its simplicity. The platform is intuitive and easy to navigate, with minimal learning curves for both practitioners and their clients. The robust support team and extensive online resources ensure any questions are resolved quickly.
Whether it’s automating reminders, securely managing client data, or customizing a practice’s workflow, SimplePractice makes running a private practice straightforward and stress-free. It’s the tool busy professionals rely on to save time, stay organized, and provide exceptional care.
The SimplePractice appointment request widget can be incorporated into a development domain for your client’s pending Divi site and ultimately in the live site. Here’s how you can achieve this:
Step 1: Review the Widget Code
Once you have the widget code from the client, you need to verify its structure. Typically, it includes a <script> tag provided by SimplePractice. For example:
The data-sp-client-id is unique to your client’s SimplePractice account, so ensure that value matches.
Step 2: Add the Widget Code to the Divi Site
In Divi, you can embed custom code into the site using the Code Module or Theme Builder:
- Using the Divi Code Module:
- Open the page or section where you want to display the widget.
- Add a Code Module within the desired row or column.
- Paste the SimplePractice widget code into the module.
- Save the changes and preview to ensure the widget appears as expected.
- Using Divi Theme Builder (if the widget should appear site-wide):
- Navigate to Divi > Theme Builder in the WordPress dashboard.
- Create or edit a custom header, footer, or body section.
- Add a Code Module and paste the widget code.
- Assign the template to the desired pages or the entire site.
Step 3: Customize the Widget (Optional)
The Customizing Your Widget section in the SimplePractice documentation explains how you can:
- Change colors, fonts, and styles to match the Divi site’s design.
- Customize settings by modifying the
<script> code parameters.
If your client’s code already includes customization, verify if it aligns with the new site’s look. For further adjustments, update the styles within the widget script.
Step 4: Use the Development Domain
SimplePractice widgets do not rely on a specific domain to function, as long as the data-sp-client-id is correct. You can install and test the widget on the development domain without any issues. Once the site goes live on the actual domain, the widget should still work without changes.
However, after the site goes live, it’s good practice to:
- Confirm the widget works properly on the live domain.
- Recheck any customized URLs or redirects tied to the widget to ensure they match the live setup.
Step 5: Test the Integration
- Navigate to the development site.
- Test the widget to ensure it displays and works correctly (e.g., appointment requests can be submitted).
- Check for any conflicts with other scripts or plugins on the Divi site.
by Charles Oropallo | Sep 27, 2024 | Do-It-Yourself, Technical Help, The CW Corner, Web Hosting, WordPress
You updated PHP on your hosting account and suddenly your WordPress site displays a white screen or error messages. Sound familiar? You’re not alone. PHP updates break WordPress sites more often than you’d think, but the good news is that most issues have straightforward fixes.
The problem usually stems from outdated plugins, themes, or even WordPress core files that aren’t compatible with newer PHP versions. Think of it like trying to run old software on a brand-new computer – sometimes it just doesn’t work without updates.
Don’t panic. Here’s your step-by-step recovery plan to get your site back online and properly updated.
Step 1: Revert PHP Version Immediately
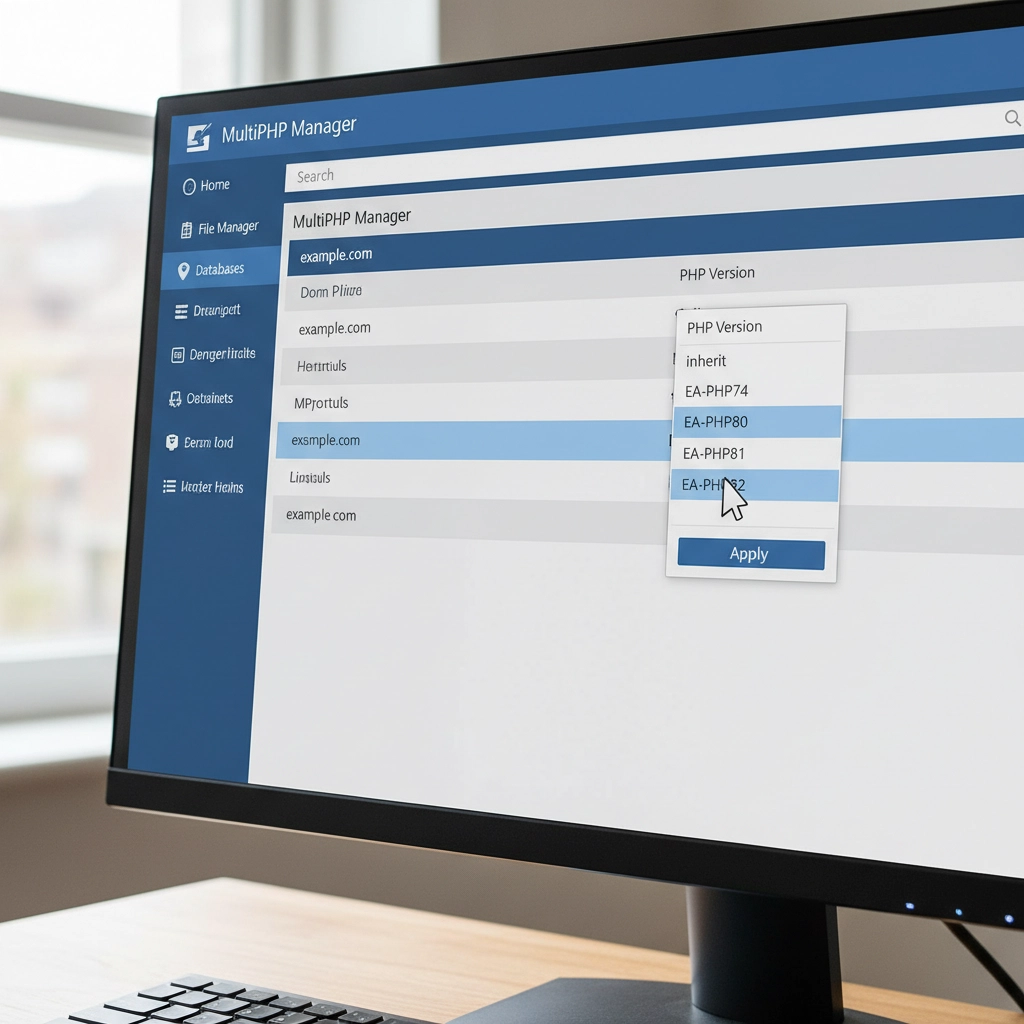
Your first priority is getting your site back online. Log into your hosting control panel (like cPanel) and find the PHP settings. This might be called “MultiPHP Manager,” “PHP Version,” or “Select PHP Version.”
Switch back to your previous PHP version – usually PHP 7.4 or 8.0. Your site should come back online within minutes. This buys you time to properly diagnose and fix the underlying compatibility issues.
Remember, this is a temporary fix. Running outdated PHP versions leaves your site vulnerable to security threats. PHP 7.4 stopped receiving security updates in November 2022, and even PHP 8.0 support ended in November 2023.
Step 2: Create a Full Site Backup
Before making any changes, backup everything. Use a plugin like UpdraftPlus or your hosting provider’s backup tool. You need both your website files and database.
Think of this as insurance. If something goes wrong during the update process, you can restore your site to its current working state. Many hosting providers offer one-click backups through their control panels.
Don’t skip this step. I’ve seen too many sites get worse instead of better because someone tried to fix things without a safety net.
Step 3: Update WordPress Core, Themes, and Plugins
Head to your WordPress dashboard and navigate to Updates. Install all pending updates for WordPress core, your active theme, and plugins. Newer versions often include compatibility patches for recent PHP versions.
Pay special attention to plugins you haven’t updated in months or years. Abandoned plugins are the biggest culprits in PHP compatibility issues. If you see plugins that haven’t been updated in over two years, consider finding alternatives.
Update your active theme too. Custom themes from developers who no longer provide support can be particularly problematic. If your theme hasn’t been updated recently, contact the developer or consider switching to a well-maintained alternative.
Step 4: Run a PHP Compatibility Check
Install the PHP Compatibility Checker plugin by WP Engine. This free tool scans your entire site and generates a report showing which themes and plugins won’t work with newer PHP versions.
Run a scan targeting your desired PHP version (usually PHP 8.1 or 8.2). The report will flag specific files and functions that need attention. This gives you a roadmap for what needs fixing before you can safely update PHP.
The scan might take several minutes depending on your site size. Don’t close your browser tab while it’s running. The detailed report will show you exactly which plugins or themes are causing problems.
Step 5: Test in a Staging Environment
If your hosting provider offers staging sites, use one. Create a copy of your live site where you can safely test the PHP update without affecting visitors.
Apply the PHP update to your staging site first. If everything works correctly there, you can confidently update your live site. If problems occur, you can troubleshoot without any downtime.
Many hosts include staging tools in their control panels. WordPress.com, WP Engine, and SiteGround all offer easy staging environments. Some plugins like WP Staging can create staging sites on any host.
Step 6: Isolate Problematic Components
If your site still breaks after updating everything, you need to identify the specific culprit. Start by deactivating all plugins and switching to a default WordPress theme like Twenty Twenty-Four.
Try the PHP update again. If your site works with all plugins disabled and the default theme active, you know the problem is with a plugin or your theme.
Reactivate plugins one by one, testing your site after each activation. When your site breaks, you’ve found the problematic plugin. Do the same process with your theme by switching back to it after testing all plugins.
Step 7: Handle Incompatible Extensions
Found the troublemaker? You have several options. First, check if there’s a newer version available. Plugin developers often release compatibility updates shortly after new PHP versions.
If no update exists, look for alternative plugins that provide the same functionality. The WordPress plugin directory has thousands of options, and newer plugins typically support current PHP versions.
For premium plugins or themes, contact the developer directly. Many offer compatibility updates for paying customers even if they haven’t released public updates.
Sometimes you might need to hire a developer to update custom code or modify a theme. This is especially common with heavily customized sites or older premium themes.
Step 8: Reapply the PHP Update
Once you’ve resolved all compatibility issues, it’s time to update PHP again. Go back to your hosting control panel and select your target PHP version.
Most sites work well with PHP 8.1 or 8.2. These versions offer significant performance improvements over older versions. WordPress officially supports PHP 8.0 and higher, with PHP 8.1 being the recommended version.
Apply the change and test your site thoroughly. Check your homepage, admin area, contact forms, and any special functionality like e-commerce checkout processes.
Step 9: Post-Update Monitoring
After updating PHP, monitor your site closely for the first few days. Clear all caches – server-level caches, plugin caches, and your browser cache.
Check your hosting control panel’s error logs for any PHP errors or warnings. Look for the “Error Logs” section in cPanel or similar tools in other hosting panels. WordPress also creates debug logs if you enable debugging in wp-config.php.
Set up website monitoring tools to alert you if your site goes down. Services like UptimeRobot or Pingdom can send email alerts when problems occur.
Prevention Tips for Future Updates
Stay proactive with updates. Install WordPress, theme, and plugin updates regularly instead of letting them accumulate. Regular small updates are much safer than jumping multiple versions at once.
Remove unused plugins and themes. Every piece of code on your site is a potential compatibility problem. If you’re not actively using a plugin, delete it completely.
Consider managed WordPress hosting. Companies like WP Engine, Kinsta, and Pressable handle PHP updates more carefully, often testing compatibility before applying updates to your site.
When to Get Professional Help
Some situations require expert assistance. If you’re running a mission-critical e-commerce site, have heavily customized code, or feel overwhelmed by the technical steps, consider hiring a WordPress professional.
Custom-built themes and plugins often need developer attention for PHP compatibility. The cost of professional help is usually much less than the revenue lost from extended downtime.
Don’t let pride keep your site broken. Sometimes the smartest move is admitting you need help and getting your site fixed quickly and correctly.
Your WordPress site doesn’t have to break every time PHP updates. With proper preparation and systematic troubleshooting, you can keep your site running smoothly on current, secure PHP versions. The key is taking it step by step and not rushing the process.
by Charles Oropallo | Aug 23, 2024 | Do-It-Yourself, Security, Technical Help, The CW Corner, WordPress
WordPress powers over 40% of all websites on the internet. That popularity makes it a prime target for hackers. Every day, thousands of WordPress sites get compromised because owners make simple security mistakes.
The good news? Most of these mistakes are easy to fix. You don’t need to be a security expert to protect your website. You just need to know what you’re doing wrong and how to fix it.
Let’s dive into the seven biggest WordPress security mistakes and their solutions.
Mistake #1: Ignoring Updates (The Silent Site Killer)
Here’s the harsh truth: 97% of WordPress security problems come from plugins. Yet only 30% of WordPress users have auto-updates enabled.
Think about it this way. When developers find a security hole, they release an update to fix it. The longer you wait to update, the more time hackers have to exploit that known weakness.
How to Fix It:
Enable automatic updates for WordPress core, plugins, and themes. Most hosting providers offer this feature in their control panels. If yours doesn’t, consider switching to a managed WordPress host.
Check your plugins weekly. Delete any you’re not using. Inactive plugins can still be exploited by hackers.
Set calendar reminders if auto-updates aren’t available. Manual updates beat no updates every time.
Pro Tip: Create a staging site to test updates before they go live. This prevents your main site from breaking during updates.
Mistake #2: Using Weak Passwords and Predictable Usernames
“admin” with password “password123” isn’t clever. It’s dangerous. 41% of WordPress users still use weak passwords or skip two-factor authentication entirely.
Hackers use bots that test thousands of password combinations per minute. A weak password like “ADMIN123” gets cracked in seconds.
How to Fix It:
Create strong passwords with at least 12 characters. Mix uppercase, lowercase, numbers, and special characters.
Never use “admin” as your username. Choose something unique that doesn’t relate to your business name.
Use a password manager like 1Password or Bitwarden. They generate complex passwords and store them securely.
Change default usernames immediately. If you already have an “admin” account, create a new administrator account with a different username, then delete the old one.
Quick Check: Can you guess your password by looking at your keyboard or personal information? If yes, change it now.
Mistake #3: Skipping Two-Factor Authentication (Your Security Backup Plan)
Passwords alone aren’t enough anymore. Even strong passwords can be compromised through data breaches or phishing attacks.
Two-Factor Authentication (2FA) adds a second layer of protection. Even if hackers get your password, they still need your phone or authentication app to get in.
How to Fix It:
Install a 2FA plugin like Wordfence or Google Authenticator for WordPress.
Set up 2FA for all user accounts, especially administrators and editors.
Use an authenticator app instead of SMS when possible. Apps like Google Authenticator or Authy are more secure than text messages.
Test your 2FA setup regularly. Make sure you can access backup codes if you lose your phone.
Remember: 2FA might seem inconvenient, but it’s much less inconvenient than rebuilding your hacked website.
Mistake #4: Forgetting to Back Up Your Website
“My hosting company handles backups.” Famous last words from website owners who lost everything.
Hosting backups might not include all your files. They might be stored on the same server that gets hacked. Or they might be overwritten before you realize you need them.
How to Fix It:
Set up automated daily backups that include your entire website and database.
Store backups in multiple locations. Use cloud services like Google Drive, Dropbox, or Amazon S3.
Test your backup restoration process monthly. A backup that doesn’t restore is useless.
Keep at least 30 days of backup history. Sometimes you don’t notice problems immediately.
Use plugins like UpdraftPlus or BackWPup for automated scheduling.
Reality Check: When did you last check if your backups actually work? If you can’t answer that, check today.
Mistake #5: Installing Themes and Plugins from Sketchy Sources
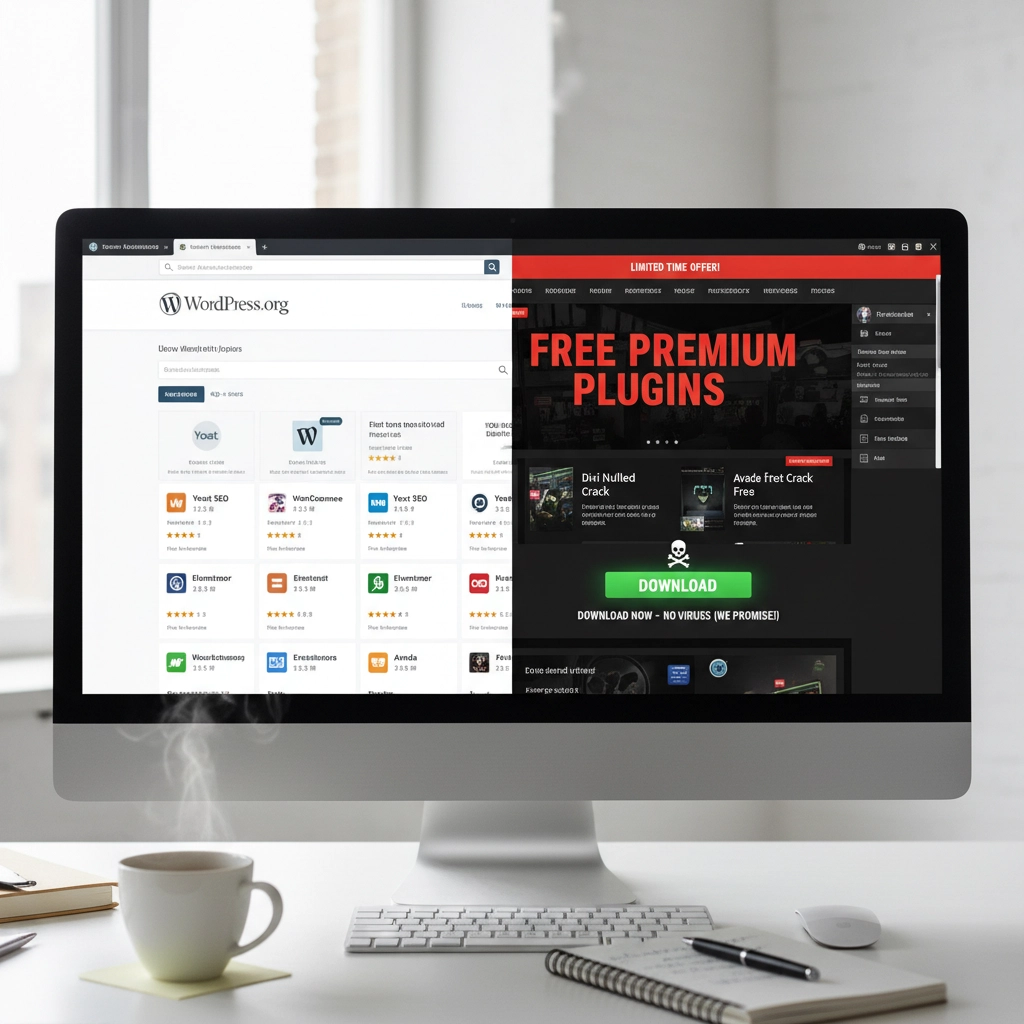
Free premium themes and plugins sound tempting. But they often come with hidden malware or backdoors that give hackers access to your site.
Even legitimate-looking themes can contain malicious code that steals user data or redirects visitors to scam sites.
How to Fix It:
Only download themes and plugins from the official WordPress repository or established developers.
Check ratings and reviews before installing anything. Look for recent updates and active support.
Research the developer. Do they have other plugins? A professional website? Good reviews?
Scan new themes and plugins with security tools before activation.
Delete unused plugins immediately. Don’t just deactivate them: remove them completely.
Warning Sign: If a “premium” theme or plugin is offered free on a random website, it’s probably infected with malware.
Mistake #6: Ignoring File Permissions (The Technical Blind Spot)
File permissions control who can access what on your server. Wrong permissions can let hackers read sensitive files or upload malicious code.
Most WordPress users never check their file permissions. They assume their hosting provider set them correctly. That’s a dangerous assumption.
How to Fix It:
Set correct file permissions: 755 for directories and 644 for files.
Never use 777 permissions unless absolutely necessary (and change them back immediately after).
Protect your wp-config.php file with 600 permissions.
Work with your hosting provider to audit permissions if you’re unsure.
Use security plugins that monitor and alert you about permission changes.
Technical Note: If file permissions sound too complex, ask your web developer or hosting support to check them for you.
Mistake #7: No Security Monitoring (Flying Blind)
Many WordPress owners only discover they’ve been hacked when visitors complain or Google flags their site. By then, the damage is done.
Hackers often work silently, stealing data or using your site to attack others. You need active monitoring to catch problems early.
How to Fix It:
Install security monitoring plugins like Wordfence, Sucuri, or iThemes Security.
Set up email alerts for suspicious login attempts, file changes, or malware detection.
Monitor your website traffic for unusual spikes or patterns.
Check your site regularly from different devices and browsers.
Use Google Search Console to monitor for security warnings.
Pro Tip: Set up uptime monitoring to alert you immediately if your site goes down. Services like UptimeRobot offer free basic monitoring.
Taking Action: Your Security Checklist
Security isn’t a one-time task. It’s an ongoing process. Here’s your priority order for fixing these mistakes:
- Enable automatic updates immediately – This fixes your biggest vulnerability right now
- Change weak passwords and usernames – Use a password manager to make this easy
- Set up 2FA on all accounts – Add that crucial second layer of protection
- Configure automated backups – Your safety net for when things go wrong
- Audit your plugins and themes – Remove anything suspicious or unused
- Check file permissions – Get help if this feels too technical
- Install security monitoring – Your early warning system
Don’t try to fix everything at once. Start with automatic updates and work down the list. Each step makes your site significantly more secure.
Remember: The best time to secure your WordPress site was yesterday. The second-best time is right now.
Need help implementing these security measures? Our team specializes in WordPress security and can audit your site for vulnerabilities. Contact us for a security consultation that could save your website from becoming another hacking statistic.





 European Union General Data Protection Regulation Compliant