by Charles Oropallo | Jan 17, 2025 | Security, Technical Help, The CW Corner, Web Hosting
Recently, I encountered an issue while attempting to renew an SSL certificate for one of my domains, (let’s call it) testdomain.com, using Let’s Encrypt on a server running Virtualmin on Debian 12. The process was more complicated than I expected due to a small oversight that many others could easily make. This article details my experience, the errors I encountered due to Let’s Encrypt rate limits (which I didn’t know existed), and steps to avoid or resolve such issues.
The Problem: Let’s Encrypt Rate Limits for Failed Authorizations
 A padlock that shows with an encrypted site using https in some browsers.
Let’s Encrypt provides free SSL certificates for securing websites. However, it enforces rate limits to ensure fair usage and prevent abuse. While attempting to renew the SSL certificate for testdomain.com, I discovered that the DNS settings were not pointed to my server, causing repeated failed validation attempts. By the time I fixed the DNS settings, I had hit Let’s Encrypt’s rate limit for failed authorizations.
This limit restricts requests for the same domain to 5 failed attempts per hour. Once you hit this limit, you must wait for the cooldown period to expire before trying again.
How the Error Appeared in Virtualmin
In the Virtualmin interface, I attempted to renew the certificate by navigating to:
- Virtualmin > Server Configuration > SSL Certificate
- Clicking on the Let’s Encrypt tab
- Ensuring the domain and subdomain (e.g.,
testdomain.com and www.testdomain.com) were selected
- Clicking the Request Certificate button
The renewal process failed with an error that Virtualmin reported as “an unknown issue.” Upon further investigation, I found the detailed error logs in the Let’s Encrypt log file located at:
/var/log/letsencrypt/letsencrypt.log
From the log, I saw this message:
urn:ietf:params:acme:error:rateLimited :: There were too many requests of a given type :: too many failed authorizations (5) for "testdomain.com" in the last 1h0m0s, retry after [time].
Understanding Let’s Encrypt Rate Limits
Let’s Encrypt enforces several types of rate limits. Here are the key ones:
- Failed Validation Limit:
- 5 failed validations per domain per hour.
- This applies to any validation failure, such as DNS misconfigurations or inaccessible
.well-known/acme-challenge directories.
- Duplicate Certificate Limit:
- 5 identical certificates per week.
- If you request the same set of domains repeatedly, you’ll hit this limit.
- Certificates per Registered Domain:
- 50 certificates per registered domain per week.
- All subdomains count toward this limit.
- Account-Level Requests:
- 50 certificates per account per week.
These limits are described in detail at Let’s Encrypt’s rate limit documentation.
Diagnosing the Problem
If you encounter a similar issue, here are the steps to diagnose and resolve it:
1. Check DNS Settings
- Ensure the domain’s DNS A records correctly point to your server.
- Use tools like
dig or online DNS propagation checkers to verify.
2. Verify Webroot Accessibility
3. Examine Let’s Encrypt Logs
4. Check Cooldown Period
- If you’ve hit the rate limit, the log will indicate a
Retry-After time in UTC. Convert it to your local timezone to determine when you can retry.
5. Dry Run Your Request
Steps to Avoid Future Issues
1. Ensure DNS Settings Before Requesting Certificates
- Double-check that DNS records point to the correct server and have propagated globally before initiating an SSL request.
2. Test Webroot Configuration
- Verify that the
.well-known/acme-challenge/ directory is accessible for all domains you’re requesting.
3. Use the Dry-Run Option
- Always test with
--dry-run before making a live request to avoid hitting limits.
4. Automate Renewals
- Virtualmin and Certbot support automated renewals. Ensure the cron job is configured correctly and DNS remains stable.
5. Avoid Forcing Duplicate Requests
- Options like
--duplicate and --force-renewal can lead to unnecessary requests. Only use them when absolutely necessary.
Conclusion
Hitting Let’s Encrypt’s rate limits can be frustrating, but understanding the causes and solutions can save time and effort. By checking DNS settings, verifying webroot accessibility, and using dry runs, you can prevent failed authorizations and avoid cooldown periods.
If you’re using Virtualmin, remember to check the Let’s Encrypt logs for detailed error messages, and plan your certificate renewals carefully to stay within the rate limits. Hopefully, my experience with testdomain.com helps you navigate and prevent similar issues.
As always, proactive testing and attention to detail go a long way in maintaining a secure and smoothly running server.


by Charles Oropallo | Oct 18, 2024 | Do-It-Yourself, Security, Technical Help, The CW Corner, Web Hosting
 If you secure many sites with free Let’s Encrypt SSL, you may hit a wall. Suddenly, certificate requests stop cold. One day everything works. The next, you see rate-limit errors and wonder what happened.
Here’s the thing. Let’s Encrypt secures over 350 million websites with free SSL. To keep things stable and safe, they enforce strict rate limits. These limits can surprise even seasoned developers. They bite hardest when securing many domains or subdomains at once.
Understanding these limits prevents headaches. It also keeps your sites secure and your business running. I’ll explain what the limits mean. I’ll share five practical steps to avoid SSL issues before they happen.
What Are Let’s Encrypt Rate Limits?
Think of Let’s Encrypt rate limits like a busy restaurant. It can serve only so many guests each hour. They are not there to hassle you. They ensure fair access and protect the system.
The key limit is 50 certificates per registered domain every 7 days. “Registered domain” means your eTLD+1, or main domain. If you own example.com, all subdomains share that weekly pool. That includes www, blog, and shop subdomains.
That’s not the only limit. You get 5 failed validation attempts per domain per hour. Repeated failures trigger a temporary lockout. Common causes include DNS or firewall issues. There’s also a duplicate certificate limit of 5 per week. Renewals do not count against the 50-certificate quota.
Account creation is limited too: 10 accounts per IP every 3 hours. This prevents abuse through mass accounts. It can also affect legitimate teams that need several accounts.
Step 1: Use Wildcard Certificates for Multiple Subdomains
Here’s your first defense against rate limits. Use a single wildcard certificate, not many subdomain certificates. One wildcard covers all subdomains under your domain.
A wildcard for *.example.com secures www, blog, shop, and new subdomains. You issue only one certificate. This slashes issuance volume and stays within Let’s Encrypt limits.
Even better, a single certificate can list up to 100 domains. Managing many brands? Combine domains into fewer certificates. One cert can cover yourcompany.com, .net, and .org.
Look at your setup. Are you requesting one certificate per subdomain? If so, you burn limits quickly. Switching to wildcard certificates is often the top fix.
Step 2: Test in the Staging Environment First
Before deploying live, test in Let’s Encrypt’s staging environment. It’s a safe practice kitchen. Mistakes don’t affect customers.
Staging has relaxed limits: 50 new registrations per IP per 3 hours. Production allows only 10. Use staging to test SSL, fix DNS, and refine deployment.
Many teams skip this step in a rush to go live. That’s when rate-limit problems strike. You issue, it fails, you retry, and hit five failures. Now you must wait.
Follow this rule. Do not issue a production certificate until staging succeeds. Spend 15 extra minutes. It could save days later.
Step 3: Implement Protective Safeguards
Smart hosting platforms add safeguards to prevent runaway certificate requests. You should do the same.
Many platforms lock SSL provisioning after three failures. They stop before Let’s Encrypt’s limit of five. That buffer prevents retry loops and protects weekly limits.
If you manage SSL yourself, add similar safeguards. Monitor requests per domain and per week. Create alerts near the limits. Add automatic delays between retries.
Do not rely on manual steps. SSL issues feel urgent, and pressure creates mistakes. Automation removes human error in Let’s Encrypt rate-limit management.
Step 4: Monitor and Space Out Certificate Requests
If you manage many sites or a SaaS, timing matters. Be strategic with certificate requests. Avoid securing everything at once.
Let’s Encrypt allows 10 certificates per IP every three hours. Migrating dozens at once? Pace your requests. Spread them over days, not one afternoon.
Keep detailed logs of issuance times and domains. This is essential for weekly limits. Know exact counts for each domain over seven days before requesting more.
Use a spreadsheet or database to track issuance dates, renewals, and limit usage. Seeing requests visually helps avoid accidental Let’s Encrypt limit hits.
Step 5: Fix Root Causes Before Retrying Failed Requests
This might be the most important step. When provisioning fails, do not retry immediately. The seven-day window also tracks failed attempts per domain.
Instead, find and fix the root cause. Common causes include DNS mistakes, blocked HTTP validation, or domain verification issues. Retrying without fixes only wastes your limits.
Some common issues to check when certificates fail:
- DNS records pointing to the correct IP address
- Firewall rules allowing HTTP validation on port 80
- Web server configuration properly handling validation requests
- Domain ownership verification working correctly
Follow this rule of thumb. Wait at least an hour between failures. Do not retry until you fix the specific problem. Many providers recommend this. It prevents accidental lockouts.
What Happens When You Hit Rate Limits
Despite your best efforts, you may still hit limits. When it happens, wait for the window to reset. The main certificate limit resets after seven days.
While you wait, consider alternatives. Issue wildcard certificates where missing. Consolidate domains into fewer certificates. For critical needs, consider a commercial CA as a temporary last resort.
Most important, learn from the incident. Review what happened. Update processes to prevent repeats. Confirm your safeguards work properly.
Remember, Let’s Encrypt rate limits keep the service stable for everyone. Follow the five steps. Use wildcards. Test in staging. Add safeguards. Monitor usage. Fix root causes early.
The key is proactive planning, not reactive troubleshooting. With preparation, you can keep sites secure without hitting these limits.
by Charles Oropallo | Aug 23, 2024 | Do-It-Yourself, Security, Technical Help, The CW Corner, WordPress
WordPress powers over 40% of all websites on the internet. That popularity makes it a prime target for hackers. Every day, thousands of WordPress sites get compromised because owners make simple security mistakes.
The good news? Most of these mistakes are easy to fix. You don’t need to be a security expert to protect your website. You just need to know what you’re doing wrong and how to fix it.
Let’s dive into the seven biggest WordPress security mistakes and their solutions.
Mistake #1: Ignoring Updates (The Silent Site Killer)
Here’s the harsh truth: 97% of WordPress security problems come from plugins. Yet only 30% of WordPress users have auto-updates enabled.
Think about it this way. When developers find a security hole, they release an update to fix it. The longer you wait to update, the more time hackers have to exploit that known weakness.
How to Fix It:
Enable automatic updates for WordPress core, plugins, and themes. Most hosting providers offer this feature in their control panels. If yours doesn’t, consider switching to a managed WordPress host.
Check your plugins weekly. Delete any you’re not using. Inactive plugins can still be exploited by hackers.
Set calendar reminders if auto-updates aren’t available. Manual updates beat no updates every time.
Pro Tip: Create a staging site to test updates before they go live. This prevents your main site from breaking during updates.
Mistake #2: Using Weak Passwords and Predictable Usernames
“admin” with password “password123” isn’t clever. It’s dangerous. 41% of WordPress users still use weak passwords or skip two-factor authentication entirely.
Hackers use bots that test thousands of password combinations per minute. A weak password like “ADMIN123” gets cracked in seconds.
How to Fix It:
Create strong passwords with at least 12 characters. Mix uppercase, lowercase, numbers, and special characters.
Never use “admin” as your username. Choose something unique that doesn’t relate to your business name.
Use a password manager like 1Password or Bitwarden. They generate complex passwords and store them securely.
Change default usernames immediately. If you already have an “admin” account, create a new administrator account with a different username, then delete the old one.
Quick Check: Can you guess your password by looking at your keyboard or personal information? If yes, change it now.
Mistake #3: Skipping Two-Factor Authentication (Your Security Backup Plan)
Passwords alone aren’t enough anymore. Even strong passwords can be compromised through data breaches or phishing attacks.
Two-Factor Authentication (2FA) adds a second layer of protection. Even if hackers get your password, they still need your phone or authentication app to get in.
How to Fix It:
Install a 2FA plugin like Wordfence or Google Authenticator for WordPress.
Set up 2FA for all user accounts, especially administrators and editors.
Use an authenticator app instead of SMS when possible. Apps like Google Authenticator or Authy are more secure than text messages.
Test your 2FA setup regularly. Make sure you can access backup codes if you lose your phone.
Remember: 2FA might seem inconvenient, but it’s much less inconvenient than rebuilding your hacked website.
Mistake #4: Forgetting to Back Up Your Website
“My hosting company handles backups.” Famous last words from website owners who lost everything.
Hosting backups might not include all your files. They might be stored on the same server that gets hacked. Or they might be overwritten before you realize you need them.
How to Fix It:
Set up automated daily backups that include your entire website and database.
Store backups in multiple locations. Use cloud services like Google Drive, Dropbox, or Amazon S3.
Test your backup restoration process monthly. A backup that doesn’t restore is useless.
Keep at least 30 days of backup history. Sometimes you don’t notice problems immediately.
Use plugins like UpdraftPlus or BackWPup for automated scheduling.
Reality Check: When did you last check if your backups actually work? If you can’t answer that, check today.
Mistake #5: Installing Themes and Plugins from Sketchy Sources
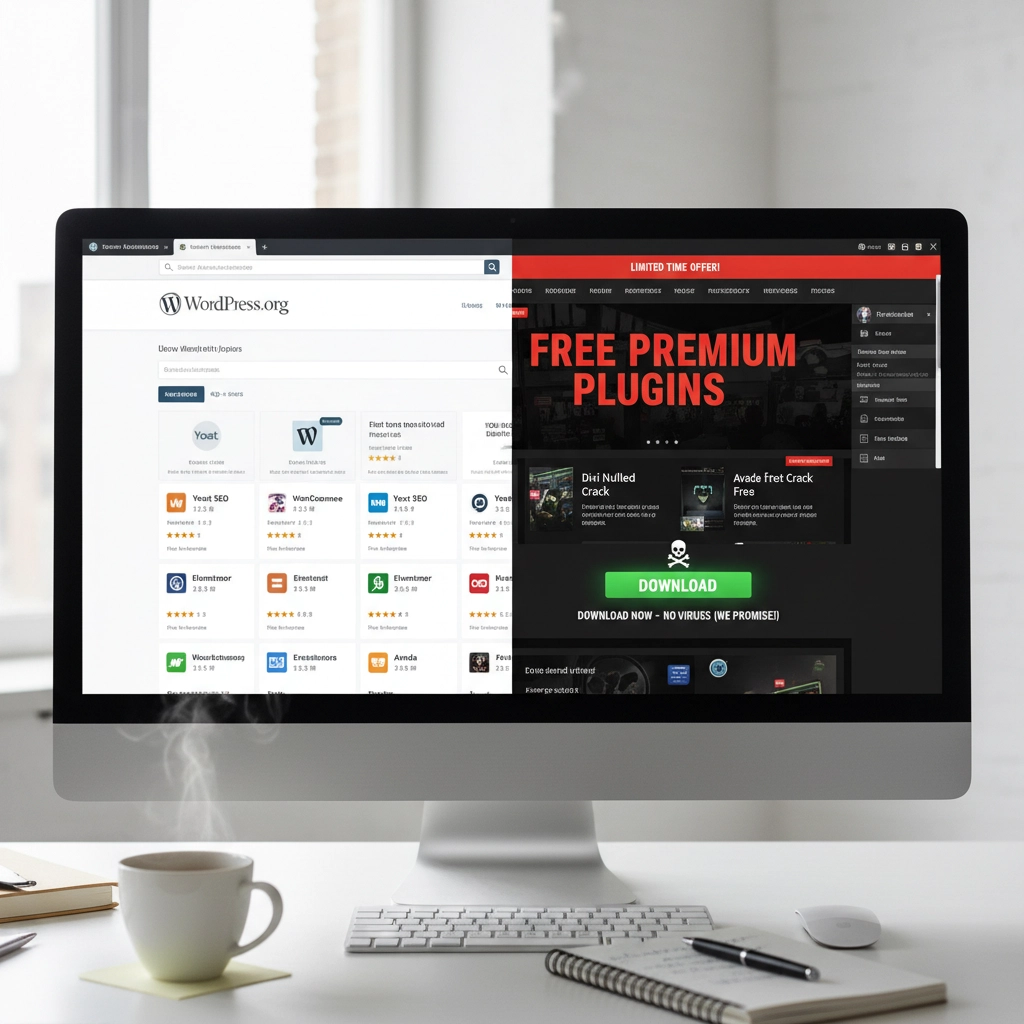
Free premium themes and plugins sound tempting. But they often come with hidden malware or backdoors that give hackers access to your site.
Even legitimate-looking themes can contain malicious code that steals user data or redirects visitors to scam sites.
How to Fix It:
Only download themes and plugins from the official WordPress repository or established developers.
Check ratings and reviews before installing anything. Look for recent updates and active support.
Research the developer. Do they have other plugins? A professional website? Good reviews?
Scan new themes and plugins with security tools before activation.
Delete unused plugins immediately. Don’t just deactivate them: remove them completely.
Warning Sign: If a “premium” theme or plugin is offered free on a random website, it’s probably infected with malware.
Mistake #6: Ignoring File Permissions (The Technical Blind Spot)
File permissions control who can access what on your server. Wrong permissions can let hackers read sensitive files or upload malicious code.
Most WordPress users never check their file permissions. They assume their hosting provider set them correctly. That’s a dangerous assumption.
How to Fix It:
Set correct file permissions: 755 for directories and 644 for files.
Never use 777 permissions unless absolutely necessary (and change them back immediately after).
Protect your wp-config.php file with 600 permissions.
Work with your hosting provider to audit permissions if you’re unsure.
Use security plugins that monitor and alert you about permission changes.
Technical Note: If file permissions sound too complex, ask your web developer or hosting support to check them for you.
Mistake #7: No Security Monitoring (Flying Blind)
Many WordPress owners only discover they’ve been hacked when visitors complain or Google flags their site. By then, the damage is done.
Hackers often work silently, stealing data or using your site to attack others. You need active monitoring to catch problems early.
How to Fix It:
Install security monitoring plugins like Wordfence, Sucuri, or iThemes Security.
Set up email alerts for suspicious login attempts, file changes, or malware detection.
Monitor your website traffic for unusual spikes or patterns.
Check your site regularly from different devices and browsers.
Use Google Search Console to monitor for security warnings.
Pro Tip: Set up uptime monitoring to alert you immediately if your site goes down. Services like UptimeRobot offer free basic monitoring.
Taking Action: Your Security Checklist
Security isn’t a one-time task. It’s an ongoing process. Here’s your priority order for fixing these mistakes:
- Enable automatic updates immediately – This fixes your biggest vulnerability right now
- Change weak passwords and usernames – Use a password manager to make this easy
- Set up 2FA on all accounts – Add that crucial second layer of protection
- Configure automated backups – Your safety net for when things go wrong
- Audit your plugins and themes – Remove anything suspicious or unused
- Check file permissions – Get help if this feels too technical
- Install security monitoring – Your early warning system
Don’t try to fix everything at once. Start with automatic updates and work down the list. Each step makes your site significantly more secure.
Remember: The best time to secure your WordPress site was yesterday. The second-best time is right now.
Need help implementing these security measures? Our team specializes in WordPress security and can audit your site for vulnerabilities. Contact us for a security consultation that could save your website from becoming another hacking statistic.
by Charles Oropallo | Feb 27, 2024 | Do-It-Yourself, Security, Technical Help, The CW Corner, WordPress
Think your WordPress site is secure? You might be shocked to learn that 97% of WordPress security problems stem from plugin vulnerabilities alone. Even worse, hackers know exactly which mistakes you’re making, and they’re counting on you to keep making them.
Don’t panic. Most WordPress security breaches happen because site owners unknowingly leave the digital equivalent of their front door wide open. The good news? These mistakes are completely preventable once you know what to look for.
Let’s dive into the seven most dangerous security mistakes that make your WordPress site an easy target for cybercriminals.
1. Running Outdated or Inactive Plugins
Here’s a scary statistic: only 30% of WordPress users have auto-updates enabled on their websites. That means 70% are sitting ducks for hackers who specifically target outdated plugins.
How Hackers Exploit This: Cybercriminals use automated scanning tools that crawl the web looking for sites running vulnerable plugin versions. When they find one, they already have the exploit code ready to go. It’s like leaving your house key under the doormat with a sign pointing to it.
Take the 2023 vulnerabilities in WP Fastest Cache and Essential Add-ons for Elementor. Thousands of websites running outdated versions became instant targets. Hackers didn’t need to be clever, they just needed to find sites that hadn’t updated.
The Fix: Enable automatic updates for plugins whenever possible. If you prefer manual control, check for updates weekly. More importantly, delete any plugins you’re not actively using. Inactive plugins are still attack vectors that hackers love to exploit.
2. Using Weak Passwords and Skipping Two-Factor Authentication
Here’s a reality check: 41% of WordPress users don’t use strong passwords or two-factor authentication (2FA). If your admin password is “password123” or your business name plus the year, you’re basically sending hackers an invitation.
How Hackers Exploit This: Brute force attacks are the digital equivalent of trying every key until one opens the lock. Hackers use bots that attempt thousands of login combinations per minute. Since WordPress allows unlimited login attempts by default, these bots can run 24/7 until they crack your password.
Once they’re in, they own your site. Customer data, financial information, email addresses, everything becomes theirs to sell or exploit.
The Fix: Use passwords that are at least 12 characters long with a mix of letters, numbers, and symbols. Better yet, use a password manager to generate unique passwords for every account. Enable 2FA immediately, Google’s research shows it stops 100% of automated bot attacks.
3. Installing Plugins and Themes from Sketchy Sources
Free premium themes and plugins sound tempting, right? Those “nulled” versions of expensive plugins seem like a steal. Here’s the truth: if something seems too good to be true, it probably contains malware.
How Hackers Exploit This: Malicious developers embed backdoors directly into these “free” premium plugins. The moment you install them, hackers have a secret entrance to your site. Some plugin viruses are designed to automatically infect every other plugin and theme on your installation, spreading like wildfire through your entire WordPress setup.
These backdoors often go undetected for months, giving hackers plenty of time to steal data, inject spam links, or use your server for cryptocurrency mining.
The Fix: Stick to plugins and themes from WordPress.org, reputable commercial developers, or well-established marketplaces. Yes, you might pay more upfront, but it’s infinitely cheaper than dealing with a hacked website.
4. Ignoring File Permissions
File permissions might sound technical, but they’re basically your site’s security guard. When configured incorrectly, they’re like having a security guard who lets anyone walk into your building.
How Hackers Exploit This: Loose file permissions allow attackers to access sensitive files they shouldn’t see. Once they have limited access, they can often escalate their privileges and gain control of critical system files. It’s like giving someone permission to use your bathroom, and they end up with keys to your entire house.
With proper access, hackers can modify your site’s code, steal database information, or install persistent backdoors that survive even when you clean up other security issues.
The Fix: Follow the principle of least privilege. Files should be set to 644 permissions, directories to 755. Your wp-config.php file should be 600. If these numbers look like gibberish, ask your hosting provider to audit your file permissions.
5. Procrastinating on WordPress Updates
Those update notifications aren’t suggestions: they’re security bulletins. Every WordPress update includes patches for newly discovered vulnerabilities. When you ignore them, you’re essentially leaving known security holes open for hackers to exploit.
How Hackers Exploit This: WordPress developers openly publish what each security update fixes. This creates a roadmap for hackers who can easily identify which sites haven’t updated and target the specific vulnerabilities that remain unpatched.
It’s like fixing a broken lock on your front door but announcing to the neighborhood exactly when the repair will happen. Unpatched sites become obvious targets.
The Fix: Update WordPress core, plugins, and themes as soon as updates become available. Schedule a weekly maintenance window to check for and install updates. Most hosting providers offer staging environments where you can test updates before applying them to your live site.
6. Skipping Backups and Security Monitoring
Not having backups is like driving without insurance: you’ll only realize how crucial it is when disaster strikes. Similarly, running a WordPress site without security monitoring is like closing your eyes and hoping nothing bad happens.
How Hackers Exploit This: Without backups, when (not if) your site gets compromised, you have no clean version to restore. Hackers know this, which is why some attacks are designed to corrupt or encrypt your existing files, leaving you with no recovery options.
Without security monitoring, attacks can run undetected for weeks or months. During this time, hackers can steal customer data, inject malicious code, or use your site to attack other websites.
The Fix: Set up automated daily backups stored off-site (not on the same server as your website). Install a security plugin that monitors file changes, login attempts, and suspicious activity. For critical business sites, consider our email security services that include comprehensive monitoring.
7. Installing Software from Unknown Repositories
This mistake often flies under the radar but can be the most dangerous. Installing plugins or themes from forums, random websites, or commercial repositories outside the WordPress ecosystem introduces unknown code into your installation.
How Hackers Exploit This: Unlike WordPress.org plugins that undergo community scrutiny, third-party sources may lack any security review process. These repositories are often intentionally compromised or simply don’t have the resources to properly vet code.
Hackers exploit this by creating legitimate-looking plugins or themes that contain hidden malware. Once installed, these give attackers automatic access to your site without needing to break in through other methods.
The Fix: Stick to WordPress.org for free plugins and themes. For premium options, buy directly from the developer or established marketplaces like CodeCanyon. Never download “nulled” versions of paid plugins: they’re almost always infected with malware.
Your Next Steps
WordPress security isn’t rocket science, but it does require consistent attention. Start by auditing your current setup against these seven mistakes. Update everything, remove unused plugins, strengthen your passwords, and enable 2FA.
Remember, hackers are counting on you to make these mistakes. Don’t give them the satisfaction. A few hours of security maintenance now can save you weeks of cleanup later: not to mention the potential loss of business and customer trust.
Need help securing your WordPress site? We specialize in helping businesses protect their digital assets without the technical headaches. Your website is too important to leave to chance.
by Charles Oropallo | Dec 17, 2023 | Do-It-Yourself, Security, The CW Corner
Let’s be honest, you didn’t start your business to become a cybersecurity expert. You’ve got products to sell, customers to serve, and a bottom line to protect. But here’s the thing: spending hours wrestling with complicated security tutorials isn’t the answer.
The good news? Website security doesn’t have to eat up your entire weekend. With these seven practical hacks, you can lock down your site without needing a computer science degree. These aren’t theoretical tips, they’re battle-tested strategies that take minutes to implement but provide months of protection.
Think of this as your security cheat sheet. No fluff, no technical jargon, just straight-forward steps that actually work.
1. Turn On Multi-Factor Authentication (MFA) Everywhere
Here’s your first quick win: enable multi-factor authentication on every account that touches your business. This means requiring two forms of identification, like your password plus a code sent to your phone, before anyone can access your systems.
Why does this matter? Even if hackers crack your password, they still can’t get in without that second verification step. It’s like having a deadbolt and a security chain on your front door.
Set this up on your website admin panel, email accounts, social media profiles, and any business applications you use. Most platforms make this incredibly easy, usually just a toggle switch in your security settings.
Don’t skip this step because it seems like a hassle. The extra 30 seconds during login is nothing compared to the weeks you’d spend recovering from a breach.
2. Get That SSL Certificate Installed (And Keep It Updated)
If your website URL doesn’t start with “https://”, you’re broadcasting to the world that your site isn’t secure. Visitors see those dreaded “Not Secure” warnings, search engines penalize your rankings, and hackers see an easy target.
An SSL certificate encrypts data between your website and visitors. It’s like putting your conversation in a locked briefcase instead of shouting it across a crowded room.
Most hosting providers offer SSL certificates for free or under $20 per year. If you’re not sure whether yours is installed correctly, just look at your address bar. You should see a little lock icon next to your domain name.
Pro tip: Set a calendar reminder to check your SSL certificate renewal date. An expired certificate means your site goes back to showing security warnings, not exactly the professional image you want.
3. Schedule Monthly 15-Minute Security Checkups
Here’s where most business owners go wrong: they set up security once and forget about it. That’s like installing smoke detectors and never checking the batteries.
Instead, block out 15 minutes each month for a quick security review. During this time, scan for suspicious login attempts, check for broken or modified pages, and verify your backups are working.
You don’t need fancy tools for this. Most content management systems have built-in activity logs that show recent changes and user logins. Look for anything unusual, logins from strange locations, files you didn’t create, or pages that suddenly load slowly.
Think of this as preventive maintenance for your digital storefront. Catching problems early means fixing them takes minutes instead of days.
4. Enable Automatic Updates (Yes, Really)
“But what if an update breaks my site?” This fear keeps many business owners running outdated, vulnerable software. Here’s the reality: the risk of a hacker exploiting an old security hole far outweighs the small chance an update causes problems.
Software updates aren’t just about new features, they’re about patching security vulnerabilities that hackers actively target. Running outdated software is like leaving your keys in an unlocked car.
Enable automatic updates for your website’s core software, plugins, and themes. If your platform doesn’t support automatic updates, set weekly calendar reminders to install them manually.
Still worried about updates breaking things? That’s what backups are for (more on that in tip #6). The peace of mind from staying current on security patches is worth the occasional minor glitch.
5. Implement a Real Password Policy
“Password123!” doesn’t count as secure, no matter how many exclamation points you add. Weak passwords are like having a “Welcome” mat for hackers.
Create a simple password policy for your team: minimum 12 characters, mix of letters/numbers/symbols, and no reusing passwords across accounts. Better yet, use a password manager to generate and store complex passwords automatically.

Think about what’s connected to your email accounts, your website admin panel, and your business applications. One compromised password can unlock everything. Don’t make it easy for the bad guys.
If remembering complex passwords feels overwhelming, password managers like Bitwarden or LastPass do the heavy lifting. They generate random passwords and fill them in automatically, security made simple.
6. Set Up Automatic Backups and Vulnerability Scanning
Imagine losing months of work because your website got hacked or your server crashed. Now imagine getting everything back with the click of a button. That’s the power of automatic backups.
Configure daily backups of your entire website: files, database, everything. Store these backups off-site, not on the same server as your website. Many hosting providers include this service, or you can use plugins that backup to cloud storage.
Pair this with vulnerability scanning. Services like Sucuri or Wordfence automatically check your site for malware, outdated software, and security holes. They send email alerts when they find problems, so you can fix issues before hackers exploit them.
The goal isn’t to never have problems: it’s to bounce back quickly when they happen. Automatic backups and scanning give you that resilience without ongoing effort.
7. Audit Your Plugins and Third-Party Tools
Your website is only as secure as its weakest link. That forgotten plugin you installed two years ago might be full of security holes, giving hackers a backdoor into your site.
Conduct a quarterly audit of every plugin, integration, and third-party tool connected to your website. Ask yourself: “Do I actually use this? Is it from a reputable developer? When was it last updated?”
Delete anything you don’t actively use. For the tools you keep, enable security notifications so you know about vulnerabilities immediately. Subscribe to security blogs or newsletters from your plugin developers.
This includes seemingly harmless additions like social media widgets, analytics tools, and contact forms. Each one represents a potential entry point. The fewer doors you have, the fewer you need to guard.
The Bottom Line: Security as a Business Habit
These seven hacks work because they create multiple layers of protection without requiring constant attention. You’re not trying to become a security expert: you’re building good habits that run on autopilot.
The key is treating security like any other business routine. You wouldn’t skip payroll or forget to pay rent. Website security deserves the same consistent attention.
Start with multi-factor authentication and SSL certificates: these give you the biggest security boost for the least effort. Then work through the other tips over the next few weeks.
Your future self will thank you when you’re running a secure, professional website instead of dealing with the aftermath of a security breach. And your customers will appreciate knowing their information is safe in your hands.
Need help implementing any of these security measures? Our team at The CharlesWorks Corner specializes in making website security simple and manageable for busy business owners. Don’t let security concerns keep you up at night when practical solutions are just a click away.
by Charles Oropallo | Jun 30, 2022 | Do-It-Yourself, Email, Internet, Passwords, Security, The CW Corner, Website Updates, WordPress
We at CharlesWorks are often asked by our web clients if their site is protected from malware and getting hacked. They also want to know if there site IS hacked, whether there be a charge to fix it.
The totally hack-proof website
The totally hack proof website has no access to it. So it’s not connected to the Internet. No one can view it. Such a website doesn’t sound like its of much use if no one can see it.
So, let’s agree that it is unrealistic to believe that a publicly accessible website can be totally hack-proof. Any website that is accessible via the public Internet is consistently subjected to attempts to break into it. Believe it or not, that’s the norm as opposed to the anomaly.
That being said, however, there ARE things you can do to mitigate website hacks. I have to stress the word mitigate here. Mitigation is defined as the action of reducing the severity, seriousness, or painfulness of something.
Site hacks are based on odds
My goal here is to simply remind you of what you most likely already know: that we can reduce the probability – the odds – of your site being hacked. We at CharlesWorks want that probability to be so low that it hopefully it doesn’t ever happen to you.
The major hacking causes
I have been operating CharlesWorks since 1998. In my experience, there appear to be two major reasons why sites get hacked:
-
- The access credentials/passwords have been compromised.
- The software that operates them wasn’t kept up to date.
Lets take a look at each of these below.
Compromised Access Credentials
Compromised passwords and bad actors gaining access to website login credentials is the major reason we see sites hacked. Think about this in terms of your car. You could have alarms on it. But if you make a copy of your car key and give it to someone, they can do whatever they like with the car. Whether its a drive along the beach or to rob a bank, your car is theirs to use with the key you gave them. Credentials – log in and passwords – work pretty much the same way.
CharlesWorks has many clients who want to be able to do things themselves. We are strong proponents of doing it yourself when it’s feasible and convenient. This is especially true for adding posts or page materials. It also makes sense when making other changes or modifications to your site. It is, after all, YOUR website.
However, many people fall prey to phishing schemes. Directly or indirectly, they usually end up tricked into giving out their website access credentials (as well as credentials to everything else they own). This is especially true if your email account is hacked and the hackers are able to access emails containing your website’s (and other) login credentials.
This problem is exacerbated if you have shared your website’s administrative or other access with others. Think of your emails containing various authorizations or login information as a potential weak link in a chain. If you have shared that information with others you have now created more weak links. This increases the odds of a potential compromise.
One of the best ways to mitigate these situations is to change your site’s access passwords so they are different than those possibly stored in your emails. And, to hope that anyone you may have shared your website access with has done the same.
Obviously, should site access be gained in such a manner, it would be your burden to have the site restored. I’ll expound upon this a little more at the end of this article.
Out of Date Security/Software Updates
Malware and virus protection on home computers operates a little differently than the same types of protection on servers. Website servers operate in the publicly accessible Internet. This results in many more entry points for potential issues. There are a number of very standard server protections available (which we utilize here at CharlesWorks).
After bad actors getting (or guessing) your passwords, the next major reason sites get hacked surrounds unapplied security updates and other software update issues. At CharlesWorks we mitigate such issues by running anti-malware software on our servers. Also, WordPress sites hosted on our servers are kept up to date automatically via automatic updating of the WordPress core as well as automatic updating of the the website’s plugins and themes.
There are literally thousands of individual pieces of software that must work in unison to operate most websites. These are developed by many more thousands of developers around the world. Unfortunately, no company can guarantee that a website will never get hacked. They can only mitigate security compromises and hope against the worst.
Restoring your Website
Regardless of which of the two situations above may have led to your website’s issues, your website will most likely need to be restored. That’s because after a bad actor or a hack back doors into the site will most likely have been installed for the bad actors to gain access again.
Many Internet companies claim to have automatic backups. In most of those, those backups are accessible to the user in their account. If the account is hacked, how safe do you suppose that is?
Some Internet companies delete and account upon a website being hacked. In those cases I have seen many left with no website or backup as a result.
What I believe is most important regarding this topic is the manner in which our WordPress sites are backed up every day for 30 days. Our backups are made to separate servers – external to those your the site operates on. For security reasons, the site administrators do not have access to these backups. So even with a site administrator’s compromised passwords there is no access to the backups. With these backups we can usually restore an average site in about 10-30 minutes if it needs restoring. And we can go back as far back as 30 days. We would only bill our web client for the 10-30 minutes (again – for an average website) which results in only a minor charge to restore it. Note that some websites are extremely large and require much more time to restore but these are very rare).
In my experience running CharlesWorks since 1998, we’ve built and handled more than 5,000 websites. At this point in time, I do not recall the last time a website we built and totally maintained was hacked (unfortunately I recall several instances of sites maintained by others that failed to ensure the site was updated and/or had their passwords compromised).
Sites getting hacked for out of date software happens far less frequently (if at all) when security updates are kept up to date and bad actors are kept out.
I hope this helps you understand a little more about this topic.





 European Union General Data Protection Regulation Compliant